








Python WSGI based GraphQL server
Grok based form framework
Zope Toolkit support for Zeam Form
vincentfretin/aframe-sandbox 5
https://vincentfretin.github.io/aframe-sandbox/
thefunny42/Zeam-Form-Composed 4
Composed form support for Zeam Form
Layout integration for Zeam Form
Form table support for Zeam Form
Pyramid convenience package to create robotFramework tests
cedricmessiant/collective.taxonomy 1
Create, edit and use hierarchical taxonomies in Plone!
pull request commentsupermedium/aframe-environment-component
Enable static-body on ground with a Heightfield shape (wip)
I don't plan to work on it myself for the time being. It was really a proof of concept for me back in October 2017, time flies :) I know that the physics system switched from cannon to ammo, so if somebody works on this, they should use ammo now I think. I know @arpu did similar thing in vrland.io, what tech did you use @arpu for your https://vrland.io/worldg/in map?

comment created time in 10 hours
issue commentscaleway/terraform-provider-scaleway
scaleway_instance_server private ip changes after modifications that imply a forced reboot
related issues about private ip change: #573 and #529 Like @Sh4d1 said on slack, the provider currently stop/start that can trigger a new private ip assignment instead of a reboot apparently.

comment created time in 6 days
PR opened scaleway/terraform-provider-scaleway
pr created time in 7 days
push eventvincentfretin/terraform-provider-scaleway
commit sha acde5c3fa023411ebacb47f9e9bc2d33e10c2837
doc: fix import command for registry namespace
push time in 7 days
issue closedcollective/plone.app.locales
Can we have a new release for Plone 5.2.3? The Italians will be happy. :-)
closed time in 18 days
mauritsvanrees
issue commentcollective/plone.app.locales
plone.app.locales 5.1.26 released
comment created time in 18 days
push eventplone/buildout.coredev
commit sha 3b9fbd03d6e25fb2642588e4d5fc1c249cb7a528
plone.app.locales 5.1.26
push time in 18 days
push eventcollective/plone.app.locales
commit sha e4a493fb687d0bf3ce02903ed4e2deb10808144f
Preparing release 5.1.26
commit sha 4755d3c902cba8726a8688a400c559299738136d
Back to development: 5.1.27
push time in 18 days
PR opened scaleway/terraform-provider-scaleway
pr created time in 20 days
push eventvincentfretin/terraform-provider-scaleway
commit sha 766b9d746ae384c4dd77d8a55aea6ba183ab2c07
doc: specify root_volume size_in_gb to have a working example
push time in 20 days
PR opened scaleway/terraform-provider-scaleway
pr created time in 20 days
push eventvincentfretin/terraform-provider-scaleway
commit sha ce2c00ba598c922c87db876d2a24027cb2a31ee6
doc: typo environment
push time in 20 days
fork vincentfretin/terraform-provider-scaleway
Terraform Scaleway provider
https://www.terraform.io/docs/providers/scaleway/
fork in 20 days
pull request commentplone/mockup
[WIP] Structure: added hidden badge like expired
Go ahead! :)

comment created time in 20 days
issue commentscaleway/terraform-provider-scaleway
Load balancer server_ips may not be updated if an instance change modify its private ip
I got a discussion on the support ticket. So this was a misunderstanding of my part, the Server IPs showed in the "Load balancers" tab is the two internal ips of the load balancer, something completely different from the backend server ips. I proposed to rename this label to something like "Load balancer internal ips" to the Front-End team.
comment created time in 23 days
issue commentscaleway/terraform-provider-scaleway
Load balancer server_ips may not be updated if an instance change modify its private ip
Ok, I just created a support ticket. I tried to reproduce the issue creating an instance and load balancer via the web console. I see two ips for Server IPs on the load balancer from the Load balancers tab, that is different for the single server ip I added when I created the load balancer. Maybe it's not a bug? Is Server IPs showed in the load balancer here something different that a backend server ips? Anyway it's confusing. I put that in the support ticket. :)
comment created time in 23 days
issue commentscaleway/terraform-provider-scaleway
Load balancer server_ips may not be updated if an instance change modify its private ip
@remyleone @Sh4d1 About the issue of the "Load balancers" tab in the web console showing old server ips for a load balancer I described above with my screenshots, do you have another tracker for web console issues to track it?
comment created time in 23 days
issue openedscaleway/terraform-provider-scaleway
importing an object bucket doesn't import acl
<!--- Please note the following potential times when an issue might be in Terraform core:
- Configuration Language or resource ordering issues
- State and State Backend issues
- Provisioner issues
- Registry issues
- Spans resources across multiple providers
If you are running into one of these scenarios, we recommend opening an issue in the Terraform core repository instead. --->
<!--- Please keep this note for the community --->
Community Note
- Please vote on this issue by adding a 👍 reaction to the original issue to help the community and maintainers prioritize this request
- Please do not leave "+1" or other comments that do not add relevant new information or questions, they generate extra noise for issue followers and do not help prioritize the request
- If you are interested in working on this issue or have submitted a pull request, please leave a comment
<!--- Thank you for keeping this note for the community --->
Terraform Version
<!--- Please run terraform -v to show the Terraform core version and provider version(s). If you are not running the latest version of Terraform or the provider, please upgrade because your issue may have already been fixed. Terraform documentation on provider versioning. --->
- Terraform v0.13.3
- provider.scaleway v1.16.0
Affected Resource(s)
<!--- Please list the affected resources and data sources. --->
- scaleway_object_bucket
Terraform Configuration Files
resource "scaleway_object_bucket" "terraform-state-bucket" {
  name = "myproject-terraform-state"
  acl = "private"
}
Expected Behavior
importing an object bucket should import the acl = "private"
Actual Behavior
acl = "null" instead of acl = "private"
Steps to Reproduce
<!--- Please list the steps required to reproduce the issue. --->
terraform applymv terraform.tfstate terraform.tfstate.beforeterraform import scaleway_object_bucket.terraform-state-bucket fr-par/myproject-terraform-state"acl" = "null"instead of"acl" = "private"terraform applywill proceed with changes.
If I modify by hand terraform.tfstate to put "acl": "private", then terraform apply won't do any change.
created time in 23 days
issue commentscaleway/terraform-provider-scaleway
New release including ingress=traefik2
@remyleone You can close this one I think.

comment created time in 24 days
issue commentscaleway/terraform-provider-scaleway
scaleway_k8s_cluster_beta auto_upgrade options reset after changing ingress
This was a quick fix :) Thanks.
comment created time in 24 days
issue commentscaleway/terraform-provider-scaleway
New release including ingress=traefik2
In #573 I tested to deploy ingress traefik2 with provider scaleway 1.17, it worked.
comment created time in 24 days
issue openedscaleway/terraform-provider-scaleway
scaleway_k8s_cluster_beta auto_upgrade options reset after changing ingress
<!--- Please note the following potential times when an issue might be in Terraform core:
- Configuration Language or resource ordering issues
- State and State Backend issues
- Provisioner issues
- Registry issues
- Spans resources across multiple providers
If you are running into one of these scenarios, we recommend opening an issue in the Terraform core repository instead. --->
<!--- Please keep this note for the community --->
Community Note
- Please vote on this issue by adding a 👍 reaction to the original issue to help the community and maintainers prioritize this request
- Please do not leave "+1" or other comments that do not add relevant new information or questions, they generate extra noise for issue followers and do not help prioritize the request
- If you are interested in working on this issue or have submitted a pull request, please leave a comment
<!--- Thank you for keeping this note for the community --->
Terraform Version
- Terraform v0.13.3
- provider.scaleway v1.17.0
Affected Resource(s)
- scaleway_k8s_cluster_beta
Terraform Configuration Files
resource "scaleway_k8s_cluster_beta" "main" {
  ....
  ingress           = "none"
  auto_upgrade {
    enable                        = true
    maintenance_window_day        = "sunday"
    maintenance_window_start_hour = 7
  }
}
Expected Behavior
auto_upgrade options shouldn't be modified if I update the ingress.
Actual Behavior
The auto_upgrade is reset to maintenance_window_day="any" and maintenance_window_start_hour = 0 if I update only the ingress.
Steps to Reproduce
terraform applyThe cluster is created withmaintenance_window_day="sunday"andmaintenance_window_start_hour = 7as I can see those values in the web console- change ingress from "none" to "traefik2" and run again
terraform applyI can see in the web console that the ingress changed to "traefik2" but the maintenance was reset to "Any" and "0". terraform applyI can see it wants to updatemaintenance_window_day="any" -> "sunday"andmaintenance_window_start_hour = 0 -> 7Applying it gives me traefik2, sunday and 7 in the we web console, so I need toterraform applytwice for the change to work correctly.
created time in 24 days
issue commentscaleway/terraform-provider-scaleway
Load balancer server_ips may not be updated if an instance change modify its private ip
If creating the load balancer and one instance used in the server_ips is marked as changed, the following can happen:
Error: Provider produced inconsistent final plan

When expanding the plan for
scaleway_lb_backend_beta.backend01 to include new values
learned so far during apply, provider
"registry.terraform.io/scaleway/scaleway" produced an invalid new value for
.server_ips[0]: was cty.StringVal("10.69.130.95"), but now
cty.StringVal("10.69.70.1").

This is a bug in the provider, which should be reported in the provider's own
issue tracker.
So for now, I will apply changes to the instances first, then add the load balancer. :)
comment created time in a month
pull request commentplone/Products.CMFPlone
zope.app.locales is no longer needed, all zope.app.* was removed
Yes you can do that.

comment created time in a month
pull request commentplone/Products.CMFPlone
zope.app.locales is no longer needed, all zope.app.* was removed
FYI in zope/schema/interfaces.py there is some messages that are translated in zope.app.locales, like min and max for number fields ("Start of the range", "End of the range (including the value itself)"), and also "Required" and "Tells whether a field requires its value to exist." that show up in dexterity schema editor if I remember. I know those ones were used in Plone 4.3.x because I overrode the translations in a project.
comment created time in a month
issue commentscaleway/terraform-provider-scaleway
Load balancer server_ips may not be updated if an instance change modify its private ip
Ah the server ips really changed in the load balancer, there seems to be a cache issue in the Overview panel in the console. In the backends tab, the server ips are correct. Backends are not responding though, so maybe not just a cache issue.


comment created time in a month
issue commentscaleway/terraform-provider-scaleway
Load balancer server_ips may not be updated if an instance change modify its private ip
Another issue, if I change instance_type from DEV1-M to DEV1-S, I got the following plan (which is good):
An execution plan has been generated and is shown below.
Resource actions are indicated with the following symbols:
  ~ update in-place
+/- create replacement and then destroy

Terraform will perform the following actions:

  # module.app.scaleway_instance_server.app[0] must be replaced
+/- resource "scaleway_instance_server" "app" {
      - additional_volume_ids            = [] -> null
      ~ boot_type                        = "local" -> (known after apply)
        cloud_init                       = <<~EOT
            #!/bin/bash
            apt update -y -qq
            apt install nginx -y
            cat > /var/www/html/index.html <<EOF
            <h1>${HOSTNAME}</h1>
            EOF
        EOT
        disable_dynamic_ip               = false
        disable_public_ip                = false
        enable_dynamic_ip                = false
        enable_ipv6                      = false
      ~ id                               = "fr-par-1/4a840851-7a2d-4db7-9433-1cc5e27c15aa" -> (known after apply)
        image                            = "ubuntu-focal"
      + ipv6_address                     = (known after apply)
      + ipv6_gateway                     = (known after apply)
      ~ ipv6_prefix_length               = 0 -> (known after apply)
        name                             = "tf-sandbox-srv-app-0"
      + organization_id                  = (known after apply)
      ~ private_ip                       = "10.70.76.61" -> (known after apply)
      + public_ip                        = (known after apply)
        security_group_id                = "fr-par-1/7eb2a36b-7d18-498d-a47d-9908d876e3b3"
        state                            = "started"
        tags                             = [
            "FocalFossa",
            "AppInstance",
        ]
      ~ type                             = "DEV1-M" -> "DEV1-S" # forces replacement
      ~ zone                             = "fr-par-1" -> (known after apply)

      ~ root_volume {
            delete_on_termination = true
          ~ size_in_gb            = 40 -> (known after apply)
          ~ volume_id             = "fr-par-1/3520162f-dd88-4029-8cd3-4edf9fc20111" -> (known after apply)
        }
    }

  # module.app.scaleway_instance_server.app[1] must be replaced
+/- resource "scaleway_instance_server" "app" {
      - additional_volume_ids            = [] -> null
      ~ boot_type                        = "local" -> (known after apply)
        cloud_init                       = <<~EOT
            #!/bin/bash
            apt update -y -qq
            apt install nginx -y
            #apt upgrade -y -qq
            cat > /var/www/html/index.html <<EOF
            <h1>${HOSTNAME}</h1>
            EOF
        EOT
        disable_dynamic_ip               = false
        disable_public_ip                = false
        enable_dynamic_ip                = false
        enable_ipv6                      = false
      ~ id                               = "fr-par-1/a1d5e9c6-6c03-43c8-a14e-563aec25fa27" -> (known after apply)
        image                            = "ubuntu-focal"
      + ipv6_address                     = (known after apply)
      + ipv6_gateway                     = (known after apply)
      ~ ipv6_prefix_length               = 0 -> (known after apply)
        name                             = "tf-sandbox-srv-app-1"
      + organization_id                  = (known after apply)
      ~ private_ip                       = "10.70.76.55" -> (known after apply)
      + public_ip                        = (known after apply)
        security_group_id                = "fr-par-1/7eb2a36b-7d18-498d-a47d-9908d876e3b3"
        state                            = "started"
        tags                             = [
            "FocalFossa",
            "AppInstance",
        ]
      ~ type                             = "DEV1-M" -> "DEV1-S" # forces replacement
      ~ zone                             = "fr-par-1" -> (known after apply)

      ~ root_volume {
            delete_on_termination = true
          ~ size_in_gb            = 40 -> (known after apply)
          ~ volume_id             = "fr-par-1/120e29b6-4902-45ae-9a28-0b3eb805012b" -> (known after apply)
        }
    }

  # module.app.scaleway_lb_backend_beta.backend01 will be updated in-place
  ~ resource "scaleway_lb_backend_beta" "backend01" {
        forward_port             = 80
        forward_port_algorithm   = "roundrobin"
        forward_protocol         = "http"
        health_check_delay       = "1m0s"
        health_check_max_retries = 2
        health_check_port        = 80
        health_check_timeout     = "30s"
        id                       = "fr-par/2739ce27-006b-4284-b5f9-9643024d2680"
        lb_id                    = "fr-par/0188bc7c-9d8c-4923-802f-ac7b6b61a6f5"
        name                     = "backend01"
        on_marked_down_action    = "none"
        send_proxy_v2            = false
      ~ server_ips               = [
          - "10.70.76.61",
          - "10.70.76.55",
        ] -> (known after apply)
        sticky_sessions          = "none"

        health_check_tcp {}
    }

Plan: 2 to add, 1 to change, 2 to destroy.

Changes to Outputs:
  ~ app_private_ip                       = [
      - "10.70.76.61",
      - "10.70.76.55",
      + (known after apply),
      + (known after apply),
    ]

Apply complete! Resources: 2 added, 1 changed, 2 destroyed.

Outputs:

app_lb_ip = [
  "x.x.x.x",
]

app_private_ip = [
  "10.70.76.37",
  "10.70.76.43",
]
but the server_ips did change in the terraform.tfstate but didn't change on the load balancer when I look into the web console. It still references the old private ips.
comment created time in a month
issue openedscaleway/terraform-provider-scaleway
Load balancer server_ips may not be updated if an instance change modify its private ip
<!--- Please note the following potential times when an issue might be in Terraform core:
- Configuration Language or resource ordering issues
- State and State Backend issues
- Provisioner issues
- Registry issues
- Spans resources across multiple providers
If you are running into one of these scenarios, we recommend opening an issue in the Terraform core repository instead. --->
<!--- Please keep this note for the community --->
Community Note
- Please vote on this issue by adding a 👍 reaction to the original issue to help the community and maintainers prioritize this request
- Please do not leave "+1" or other comments that do not add relevant new information or questions, they generate extra noise for issue followers and do not help prioritize the request
- If you are interested in working on this issue or have submitted a pull request, please leave a comment
<!--- Thank you for keeping this note for the community --->
Terraform Version
<!--- Please run terraform -v to show the Terraform core version and provider version(s). If you are not running the latest version of Terraform or the provider, please upgrade because your issue may have already been fixed. Terraform documentation on provider versioning. --->
Terraform v0.13.3 provider.scaleway v1.16.0
Affected Resource(s)
<!--- Please list the affected resources and data sources. --->
- scaleway_instance_server private_ip
- scaleway_lb_backend_beta server_ips
Terraform Configuration Files
<!--- Information about code formatting: https://help.github.com/articles/basic-writing-and-formatting-syntax/#quoting-code --->
cloud_init.bash file:
#!/bin/bash
apt update -y -qq
apt install nginx -y
cat > /var/www/html/index.html <<EOF
<h1>${HOSTNAME}</h1>
EOF
main.tf file:
terraform {
  required_version = ">= 0.13, < 0.14"
  required_providers {
    scaleway = {
      source  = "scaleway/scaleway"
      version = "~> 1.16"
    }
  }
}

resource "scaleway_instance_server" "app" {
  count = 2
  name = "tf-srv-app-${count.index}"
  type  = "DEV1-S"
  image = "ubuntu-focal"

  tags = [ "FocalFossa", "AppInstance" ]
  cloud_init = file("${path.module}/cloud_init.bash")
}

resource "scaleway_lb_ip_beta" "ip" {
}

resource "scaleway_lb_beta" "lb" {
  name = "tf-lb-app"
  ip_id = scaleway_lb_ip_beta.ip.id
  region      = "fr-par"
  type        = "LB-S"
}

resource "scaleway_lb_backend_beta" "backend01" {
  lb_id = scaleway_lb_beta.lb.id
  name = "backend01"
  forward_protocol = "http"
  forward_port = "80"
  server_ips = scaleway_instance_server.app[*].private_ip
}

resource "scaleway_lb_frontend_beta" "frontend01" {
  lb_id = scaleway_lb_beta.lb.id
  backend_id = scaleway_lb_backend_beta.backend01.id
  name = "frontend01"
  inbound_port = "80"
}
outputs.tf file:
output "lb_ip" {
  value = scaleway_lb_beta.lb.ip_address
  description = "Public ip of the load balancer"
}
Expected Behavior
scaleway_lb_backend_beta server_ips needs to be updated if instance private ip changed.
So terraform plan/apply should always shows the following:
      ~ server_ips               = [
          - "10.70.76.37",
          - "10.70.76.43",
        ] -> (known after apply)
if private ips can potentially be changed.
Actual Behavior
terraform plan/apply says there will be no required change for scaleway_lb_backend_beta server_ips but this is not true.
Steps to Reproduce
<!--- Please list the steps required to reproduce the issue. --->
First time:
terraform apply
Load balancer is working fine
watch curl --silent http://<app_lb_ip>/
alternate between tf-srv-app-0 and tf-srv-app-1.
Now change the tags of scaleway_instance_server and run terraform apply
The 2 instances will be changed (rebooted) and may some times have a different private ip assigned, but the scaleway_lb_backend_beta server_ips will still reference the old private ips.
You will see in this case Service Unavailable with the watch curl --silent http://<app_lb_ip>/ command.
To be sure the private ips didn't change, I need to run terraform apply again, if I see no changes, all is good. If there are changes in scaleway_lb_backend_beta server_ips, I need to apply the changes.
References
<!--- Information about referencing Github Issues: https://help.github.com/articles/basic-writing-and-formatting-syntax/#referencing-issues-and-pull-requests
Are there any other GitHub issues (open or closed) or pull requests that should be linked here? Vendor documentation? For example: --->
- similar issue with private ip that changed #529
created time in a month
issue commentscaleway/terraform-provider-scaleway
I just had a similar issue with private ip that changed (some times, not always) when an instance changed (if you modify the tags for example). The problem is that I reference the private ip for a load balancer, so here I need to run terraform apply a second time to verify if the private ips changed, if yes, apply the changes for the load balancer.
extract of my config:
resource "scaleway_instance_server" "app" {
  count = 2
  ...
}

resource "scaleway_lb_backend_beta" "backend01" {
  ...
  server_ips = scaleway_instance_server.app[*].private_ip
}
I don't think this can be solved in the provider. The provider don't know in advance that the private ip will change, so it can't say that the load balancer config will be changed. It can maybe detect during the execution that the private ip changed, but it shouldn't apply changes to the load balancer config that I didn't validate.

comment created time in a month
issue openedcollective/plone.app.locales
Hi everyone,
We need to update the i18n team on plone.org @cdw9 just gave me the permission to modify this page.
Does anyone still use IRC? Does the channel plone.org still exist? I think we can remove reference to IRC there.
For the list of members, I think this list is quite old, lots of inactive members. Same for https://github.com/collective/plone.app.locales/blob/master/docs/TRANSLATORS.html I think it's very old info, and there is no rendering of this page! I propose to remove TRANSLATORS.html from the repo, remove the old list of members on the i18n page, and create a new one based on latest active contributors like I did in https://github.com/collective/plone.app.locales/issues/294#issuecomment-646071169 and really add github handles instead of irc nickname. And maybe add which language has not current maintainer? What do you think? If you don't want to be listed there, please tell me. If you want to be listed, please also tell me. :-)
There is still mention of the plone-i18n mailing-list that has long been inactive (maybe it already has been archived or removed, I'm not sure). Instead we need to add a reference to the i18n category of the forum https://community.plone.org/c/development/i18nl10n/42 Do you want your local community to be listed there too? If yes, give me the link and eventually a small paragraph to add on the page.
If there is other changes you want to make to this page, please add a comment.
created time in a month
startedscaleway/terraform-provider-scaleway
started time in a month
issue closedcollective/plone.app.locales
I am making a Plone 5.1.7rc1 as we speak. Could we have a new plone.app.locales release? The only changes since the last release of 14 July are two updated German translations, so there is not much need. But I am happy include to a new release if there is one.
closed time in a month
mauritsvanrees
issue commentcollective/plone.app.locales
plone.app.locales 5.1.25 released
comment created time in a month
push eventplone/buildout.coredev
commit sha d3828947d2e5c15daf38bfe6dcae0842e3673587
plone.app.locales 5.1.25
push time in a month
push eventplone/buildout.coredev
commit sha f54acbacc33f6d6fc03e86e1ccf0ff4580286413
plone.app.locales 5.1.25
push time in a month
push eventcollective/plone.app.locales
commit sha 9f84f78f50f56f910d6f1631ed3b1e046ed8016b
Preparing release 5.1.25
commit sha 1715144dc0afd732fd246bb4627f65a78398c463
Back to development: 5.1.26
push time in a month
pull request commentmozilla/hubs
Add uv-scroll component to animate UV offsets
Ah I found it again on youtube, this video: https://www.youtube.com/watch?v=zOzTGby8Iag

comment created time in a month
pull request commentmozilla/hubs
Add uv-scroll component to animate UV offsets
@andybak I watched the full video some weeks ago, not only the highlight. As far I understand it, the component is meant to be used via a gltf model created with blender with https://github.com/MozillaReality/hubs-blender-exporter
comment created time in a month
pull request commentmozilla/hubs
Add uv-scroll component to animate UV offsets
I think https://www.twitch.tv/videos/689725972 is related to this.
comment created time in a month
pull request commentplone/Products.CMFPlone
New resource registry bundles for Plone 5.1.7.
Hi @mauritsvanrees sorry I was in vacation last week. You did good. FYI For Plone 5.1.x this doc applies https://github.com/plone/Products.CMFPlone/blob/56147f7c15bddb4ae9c4573f6593f4b3e1546a86/DEVELOPING_BUNDLES.rst Btw this doc is still on master, but it's not relevant for Plone 5.2.x.
comment created time in a month
issue commentmozilla/janus-plugin-sfu
could not compile on fresh debian 10 install
I don't know a thing of rust, but I can say the build works fine with rustc 1.43.0 (rustc --version) on Ubuntu 18.04.

comment created time in 2 months
issue commentmozilla/dialog
using this with an NAF project?
As far as I understand, Hubs server reticulum uses the guardian elixir module https://github.com/ueberauth/guardian to generate the jwt perms token here https://github.com/mozilla/reticulum/blob/e50b16244a3ef6b41617fd4c81c0537dc2830306/lib/ret/perms_token.ex#L27
It uses the private RSA 2048 key to sign the token with the RS512 algorithm and I think perms variable is here { join_hub: true, kick_users: true} you can see in the Rust struct.
The Rust code want a JWT token encoded with the RS512 algorithm as well https://github.com/mozilla/janus-plugin-sfu/blob/14a33464726166fa0d3a20bd452ad05d2f7c53a6/src/auth.rs#L19
In the janus conf auth_key should point to the public RSA key
https://github.com/mozilla/hubs-ops/blob/0c27ac2bf5b29a3988ce0a5e85f4903fb66177d9/plans/janus-gateway/habitat/config/janus.plugin.sfu.cfg#L3
I guess you can generate a 2048 RSA key with openssl command like they do here https://github.com/mozilla/hubs-ops/blob/73a82208d071baf3aa692b737c6f863f01c149e9/ansible/roles/janus/tasks/main.yml#L67
or with ssh-keygen -t rsa -b 2048 ?
If you have already a node app on the server, you can try creating a JWT token with https://github.com/auth0/node-jsonwebtoken You can see an example with node and express here https://stormpath.com/blog/nodejs-jwt-create-verify The following should be enough to create the token:
var jwt = require('jsonwebtoken');
var privateKey = fs.readFileSync('private.key');
var token = jwt.sign({ join_hub: true, kick_users: true}, privateKey, { algorithm: 'RS512' }, expiresIn: 300 });
When your user is logged in with your node app, return this token and set it with adapter.setJoinToken(token).
comment created time in 2 months
issue commentmozilla/dialog
using this with an NAF project?
The data did not match any variant of untagged enum OptionalField error can show up if you didn't call setClientId.
Here is a simple code:
function genClientId() {
  let num = '';
  for (let i = 0; i < 16; i++) {
    num += Math.floor(Math.random() * 10).toString();
  }
  return num;
}

AFRAME.scenes[0].addEventListener("adapter-ready", ({ detail: adapter }) => {
  const clientId = genClientId();  // generate an random 16 characters string, but you can use a uuid4 for example
   adapter.setClientId(clientId);
   //adapter.setJoinToken(...);
   const constraints = {audio: true};
   navigator.mediaDevices.getUserMedia(constraints).then((mediaStream) => {
     NAF.connection.adapter.setLocalMediaStream(mediaStream);
     NAF.connection.adapter.enableMicrophone(true);  // note that networked-scene audio:true option has no effect with the janus adapter, the code doesn't use it
   });
 });
});
comment created time in 2 months
issue commentmozilla/dialog
using this with an NAF project?
About horizontal scaling, you may find some answers here https://github.com/mozilla/hubs/discussions/2887
A note about version 4.0.x of naf-janus-adapter, this version changed the syncOccupants behavior to fix some issues when using another app for user presence (phoenix app), so you may find the latest version useful, see description of https://github.com/mozilla/naf-janus-adapter/pull/100
comment created time in 2 months
Pull request review commentmozilla/reticulum
+defmodule RetWeb.Resolvers.RoomResolver do+ @moduledoc """+ Resolvers for room queries and mutations via the graphql API+ """+ alias Ret.{Hub, Repo}+ alias RetWeb.Api.V1.{HubView}+ import Canada, only: [can?: 2]++ def my_rooms(_parent, args, %{context: %{account: account}}) do+ {:ok, Hub.get_my_rooms(account, args)}+ end++ def my_rooms(_parent, _args, _resolutions) do+ {:error, "Not authorized"}+ end++ def favorite_rooms(_parent, args, %{context: %{account: account}}) do+ {:ok, Hub.get_favorite_rooms(account, args)}+ end++ def favorite_rooms(_parent, _args, _resolutions) do+ {:error, "Not authorized"}+ end++ def public_rooms(_parent, args, _resolutions) do+ {:ok, Hub.get_public_rooms(args)}+ end++ def create_room(_parent, args, %{context: %{account: account}}) do+ args = Map.put(args, :name, Map.get(args, :name, "Delightful Cooperative Meetup"))++ case Hub.create(args) do+ {:ok, hub} ->+ hub+ |> Hub.add_attrs_to_changeset(args)+ |> Hub.maybe_add_member_permissions(hub, args)+ |> Hub.maybe_add_promotion(account, hub, args)+ |> maybe_add_new_scene_to_changeset(args)+ |> Hub.changeset_for_creator_assignment(account, hub.creator_assignment_token)+ |> Repo.update()++ {:error, reason} ->+ {:error, reason}+ end+ end++ def create_room(_parent, args, _resolutions) do+ Hub.create(args)+ end++ def embed_token(hub, _args, %{context: %{account: account}}) do+ if account |> can?(embed_hub(hub)) do+ {:ok, hub.embed_token}+ else+ {:ok, nil}+ end+ end++ def embed_token(_hub, _args, _resolutions) do+ {:ok, nil}+ end++ def port(_hub, _args, _resolutions) do+ {:ok, Hub.janus_port()}+ end++ def turn(_hub, _args, _resolutions) do+ {:ok, Hub.generate_turn_info()}+ end++ def member_permissions(hub, _args, _resolutions) do+ {:ok, Hub.member_permissions_for_hub_as_atoms(hub)}+ end++ def room_size(hub, _args, _resolutions) do+ {:ok, Hub.room_size_for(hub)}+ end++ def member_count(hub, _args, _resolutions) do+ {:ok, Hub.member_count_for(hub)}+ end++ def lobby_count(hub, _args, _resolutions) do+ {:ok, Hub.lobby_count_for(hub)}+ end++ # def scene(hub, _args, _resolutions) do+ # {:ok, Hub.scene_or_scene_listing_for(hub)}+ # end++ def update_room(_, %{id: hub_sid} = args, %{context: %{account: account}}) do+ hub = Hub |> Repo.get_by(hub_sid: hub_sid) |> Repo.preload([:hub_role_memberships, :hub_bindings])+ update_room_with_account(hub, account, args)+ end++ def update_room(_, _, _) do+ {:error, "Not authorized"}+ end++ defp update_room_with_account(nil, _account, %{id: hub_sid}) do+ {:error, "Cannot find room with id " <> hub_sid}+ end++ defp update_room_with_account(hub, account, args) do+ case can?(account, update_roles(hub)) do+ false ->+ {:error, "Account does not have permission to update this hub."}++ true ->+ changeset =+ hub+ |> Hub.add_attrs_to_changeset(args)+ |> Hub.maybe_add_member_permissions(hub, args)+ |> Hub.maybe_add_promotion(account, hub, args)+ |> maybe_add_new_scene_to_changeset(args)++ try_do_update_room(changeset, account)+ end+ end++ defp maybe_add_new_scene_to_changeset(changeset, %{scene_id: scene_id}) do+ scene_or_scene_listing = Hub.get_scene_or_scene_listing_by_id(scene_id)++ if is_nil(scene_or_scene_listing) do+ {:error, "Cannot find scene with id " <> scene_id}+ else+ Hub.add_new_scene_to_changeset(changeset, scene_or_scene_listing)+ end+ end++ defp maybe_add_new_scene_to_changeset(changeset, _args) do+ changeset+ end++ defp try_do_update_room({:error, reason}, _) do+ {:error, reason}+ end++ defp try_do_update_room(changeset, account) do+ case changeset |> Repo.update() do+ {:error, changeset} ->+ {:error, changeset}++ {:ok, hub} ->+ hub = Repo.preload(hub, Hub.hub_preloads())++ case broadcast_hub_refresh(hub, account) do+ {:error, reason} -> {:error, reason}+ :ok -> {:ok, hub}+ end+ end+ end++ defp broadcast_hub_refresh(hub, account) do+ payload =+ HubView.render("show.json", %{+ hub: hub,+ embeddable: account |> can?(embed_hub(hub))+ })+ |> Map.put(:stale_fields, [+ # TODO: Only include fields that have changed in stale_fields+ "name",+ "description",+ "member_permissions",+ "room_size",+ "allow_promotion",+ "scene",+ "member_permissions"
member_permissions is twice in the list.

comment created time in 2 months
issue commentmozilla/dialog
using this with an NAF project?
Btw, I don't know if you found the example at https://github.com/mozilla/naf-janus-adapter/blob/master/examples/index.html this is not linked in the README and both the example index.html and the code snippet in the README used really old versions of aframe and networked-aframe. I completely missed this example at first, I found the relevant element to set the audio with setLocalMediaStream directly in hubs.js. Ah ah. For networked-aframe at https://github.com/MozillaReality/networked-aframe you need to include it with npm or build your own dist version to have the latest version. The dist bundle in the repo wasn't updated with the latest commits.
comment created time in 2 months
issue commentmozilla/janus-plugin-sfu
Plugin no longer loads with latest libnice and janus-gateway
FYI, Janus 0.9.x (0.9.5 is the latest compatible) is not maintained anymore, Janus 0.10.x contains bugfixes for several CVEs, see https://github.com/meetecho/janus-gateway/pull/2214 and https://github.com/meetecho/janus-gateway/pull/2229
I don't know if it will be an issue with this plugin, but with Janus 0.10.5 and videoroom plugin, you need to specify the h264 profile now, profile id is "42e01f". I see this is specified in the new dialog sfu https://github.com/mozilla/dialog/blob/dc4e59cc775f88949043c145595bd7b08fd6fcb6/config.js#L115 but I didn't find it in the rust code. Anyway we should test the video between Firefox and Chrome if you update the plugin.
A bit off topic, I had a conversation with @kylebakerio about janus-plugin-sfu integration in a naf project here https://github.com/mozilla/dialog/issues/8 If you have some more insights, you can add a comment there. You can follow the repo there too if you want to be alerted.

comment created time in 2 months
issue commentmozilla/dialog
using this with an NAF project?
You will need the JWT to work if you want the kick a user feature though. I currently don't have it. :-)
comment created time in 2 months
issue commentmozilla/dialog
using this with an NAF project?
I'm glad you're making progress. I remember having the data did not match any variant of untagged enum OptionalField error, doing a search in the rust code, you see this is related to decoding a json message. I think I got the error when I tried to set the JWT token with adapter.setJoinToken. At one point I gave up to understand what it wanted, I didn't even know what was JWT at that time so I tried just to send like a json string with adapter.setJoinToken(JSON.stringify({join_hub: true})) I think but a JWT is more complicated than that. At the end I didn't use adapter.setJoinToken and left auth_key commented in janus.plugin.sfu.cfg as I don't currently have a way to authenticated user and I have no backend.
For the transport, you're right. For sendData or sendDataGuaranteed defined in https://github.com/mozilla/naf-janus-adapter/blob/v3.0.20/src/index.js#L933-L939 the default "datachannel" will send the message { clientId, dataType, data } to janus and janus will broadcast it to everyone in the room, so be careful. I saw this behavior when adding a feature to send a text message to a specific user in the room and saw that everyone received it. :-)
The api documented at https://github.com/mozilla/janus-plugin-sfu/blob/master/docs/api.md#data with the whom to send a private message apply only to the "websocket" adapter, like you see in the sendData that's the only one using whom.
You're fine with the "datamanager" transport if you don't plan to add the feature to send a private message to your app.
I'm not connected anymore on slack aframe, but I will open it again.
comment created time in 2 months
issue commentmozilla/dialog
using this with an NAF project?
I have a naf project where I use Janus 0.9.5 with janus-plugin-sfu master from mozilla, and js client naf-janus-adapter 3.0.20 (not master with version 4.0.x)
For chat and component updates, this uses by default "datachannel" transport, see
https://github.com/mozilla/naf-janus-adapter/blob/v3.0.20/src/index.js#L81-L82
If you want to send private message described in the api doc with the whom parameter https://github.com/mozilla/janus-plugin-sfu/blob/master/docs/api.md#data (the whom parameter is set automatically by naf-janus-adapter when you use NAF.connection.sendDataGuaranteed(toClientId, 'chatbox', data) for example)
you need the "websocket" transport. NAF.connection.adapter.reliableTransport = "websocket".
Some years ago, I guess Hubs did use this. Hubs now uses a Phoenix app (reticulum), chat and component updates go through the Phoenix websocket, this is configured here https://github.com/mozilla/hubs/blob/d7b33f24f8a76b27462bb3f6f42051a55a913dc2/src/hub.js#L637-L638
With the new naf-dialog-adapter I'm not sure if it handles datamanager webrtc connection or websocket to supports chat and components updates like we had in janus-sfu-plugin or if it's only for audio/video.
comment created time in 2 months
issue commentmozilla/dialog
using this with an NAF project?
Obviously you need your own backend where the user authenticate, and return a JWT token. Then on the naf adapter, you need to set a client id and jwt token, on hubs this is done here: https://github.com/mozilla/hubs/blob/bf78a09218109ede68a41c7fa504168011983d1a/src/hub.js#L1455-L1456 If you didn't read it already, look at https://github.com/mozilla/hubs/pull/2534 for some pointers where is the code in hubs that connect to the webrtc server.
comment created time in 2 months
issue commentmozilla/reticulum
As far as I understand the ExRated code, if you do a call to youtube every 8s https://github.com/mozilla/reticulum/blob/13c932e81869096ad73879abf0c5cb2a5410c537/lib/ret/media_resolver.ex#L21 the key change every 8s, see stamp_key at https://github.com/grempe/ex_rated/blob/744c14c679d7a82e5faf3559cb098679e3dd1c30/lib/ex_rated.ex#L203 and it will create a new key in the ETS table: https://github.com/grempe/ex_rated/blob/744c14c679d7a82e5faf3559cb098679e3dd1c30/lib/ex_rated.ex#L209
comment created time in 2 months
issue openedmozilla/reticulum
Hi, I'm learning Elixir and Phoenix, I looked at how you rate-limit calls to external services. I see you use https://hex.pm/packages/ex_rated in media_resolver https://github.com/mozilla/reticulum/blob/13c932e81869096ad73879abf0c5cb2a5410c537/lib/ret/media_resolver.ex#L564 but doing a "rated" search in the code https://github.com/mozilla/reticulum/search?q=rated&type=Code I didn't find that you start the ex_rated GenServer application that is needed to prune expired buckets from the ETS table at periodic interval (cleanup_rate, default to 60s). Maybe you do and I just didn't find it, if so please close the issue. Otherwise look at https://github.com/grempe/ex_rated#installation
created time in 2 months
pull request commentplone/mockup
Fix building of the docs bundle
Question, how https://plone.github.io/mockup is updated?

comment created time in 2 months
pull request commentplone/mockup
Fix building of the docs bundle
I really verified making the docs on Ubuntu 18.04. It works great.
comment created time in 2 months
issue commentmozilla/dialog
using this with an NAF project?
Just looked into the code. I found the following.
janus-plugin-sfu allowed the connection to a room if you didn't configure an auth_key in the plugin (so it didn't verify the JWT token).
https://github.com/mozilla/janus-plugin-sfu/blob/598359f4339e08f43c2781488f457582113c8aab/src/lib.rs#L407
In dialog defining the authKey is mandatory.
So you need a valid JWT token containing {join_hub: bool, kick_users: bool}
see the structure in rust https://github.com/mozilla/janus-plugin-sfu/blob/598359f4339e08f43c2781488f457582113c8aab/src/auth.rs#L12-L15 so I think those two booleans are the only thing you need in the JWT token for dialog too.
kick_users permission defined in reticulum: https://github.com/mozilla/reticulum/blob/0cde188f38f6ac4677ae261da178f65e6ea5f72d/lib/ret/hub.ex#L559 kick_users check in janus: https://github.com/mozilla/janus-plugin-sfu/blob/598359f4339e08f43c2781488f457582113c8aab/src/lib.rs#L494 kick_users check in dialog: https://github.com/mozilla/dialog/blob/007a5c8f02f73524cefcd1b7701f06087e083a04/lib/Room.js#L1421
comment created time in 2 months
pull request commentplone/mockup
Fix building of the docs bundle
Is this fixing https://github.com/plone/mockup/issues/980 ?
comment created time in 2 months
Pull request review commentmozilla/hubs
add preference to override browser locale
const DEFINITIONS = new Map([ [ CATEGORY_MISC, [+ {+ key: "locale",+ prefType: PREFERENCE_LIST_ITEM_TYPE.SELECT,+ options: availableLocales,+ defaultString: "browser",+ promptForRefresh: true
For the key={locale} yeah I read it somewhere, but can't find it in the current documentation. Anyway I saw you're using setState in your component, so this already force a rerender as far as I know.

comment created time in 2 months
issue commentmozilla/dialog
using this with an NAF project?
I followed the different Hubs PRs, so I can reply to some of your questions. (1) The adapter lives there https://github.com/mozilla/hubs/blob/master/src/naf-dialog-adapter.js and replace naf-janus-adapter (2) The networked-aframe that Hubs uses is https://github.com/MozillaReality/networked-aframe.git (3) As my understanding, I guess this node program replace completely janus and janus-sfu plugin (4) I don't know
comment created time in 2 months
Pull request review commentmozilla/hubs
add preference to override browser locale
const DEFINITIONS = new Map([ [ CATEGORY_MISC, [+ {+ key: "locale",+ prefType: PREFERENCE_LIST_ITEM_TYPE.SELECT,+ options: availableLocales,+ defaultString: "browser",+ promptForRefresh: true
Don't you just need to specify like key={locale} on the WrappedIntlProvider component to be sure react rerender the whole tree?
comment created time in 2 months
Pull request review commentmozilla/hubs
add preference to override browser locale
// For non "en" (since it's the default), use this mapping to define a fallback, // which will only be used if the specified locale file doesn't exist. +export const AVAILABLE_LOCALES = {+ en: "English",+ zh: "简体中文"+};
You already use react-intl in the code base, you may want to use Language Display Names, see https://formatjs.io/docs/intl#formatdisplayname and https://developer.mozilla.org/en-US/docs/Web/JavaScript/Reference/Global_Objects/Intl/DisplayNames Chrome implements it. For Firefox you need the polyfill.
comment created time in 2 months
pull request commentplone/mockup
fixed external description translation
Of course someone will need to rebuild the bundles if we want the fix in Plone 5.1.7 or Plone 5.2.3.

comment created time in 2 months
push eventplone/buildout.coredev
commit sha 62de3481e385c86555195770a238b2fe574a650a
checkout mockup
push time in 2 months
pull request commentplone/mockup
fixed external description translation
I squashed and merged in master and 2.7.x
comment created time in 2 months
push eventplone/mockup
commit sha 568b2e5a6e17184c6e000774f9fca514f42c23a2
Fix external description text in tinymce link popup (#1011) Fix external description text in tinymce link popup
push time in 2 months
push eventplone/mockup
commit sha 4458e3be5f9c086a7df3422acaae849e6050399f
Fix external description text in tinymce link popup (#1011) Fix external description text in tinymce link popup
push time in 2 months
PR merged plone/mockup
Fixed wrong translation text option in links popup
pr closed time in 2 months
pull request commentplone/mockup
fixed external description translation
You can merge.
comment created time in 2 months
issue commentplone/Products.CMFPlone
Lots of deprecation warnings in Plone 5.2.2
@mauritsvanrees I see you're fixing some of the warnings, don't forget to check them here. Thanks.
comment created time in 2 months
pull request commentmozilla/hubs
Fix WrappedIntlProvider import
Maybe one of the check of https://www.npmjs.com/package/eslint-plugin-import can catch that?

comment created time in 2 months
pull request commentplone/mockup
fixed external description translation
Can can squash your commits when you merge, and then cherry-pick your commit to 2.7.x branch?
comment created time in 2 months
Pull request review commentplone/mockup
fixed external description translation
+refs plone#1010 fixed external translation textin tinymce link popup
You don't need refs plone#1010 here (and it should be mockup, not plone), it's already in the filename, so this will be used when generating the changelog.
You can modify the changelog entry like this:
Fix external description text in tinymce link popup
[parruc]
comment created time in 2 months
pull request commentplone/mockup
fixed external description translation
This was fixed in https://github.com/plone/mockup/commit/80dc11b5f6a5c47a0d7c644c65c52d71b96d9e98 and then a regression in next commit https://github.com/plone/mockup/commit/a9ff1031710c0730a57aafbb6010e5a506535a48 and now fixed again. :-)
Before:
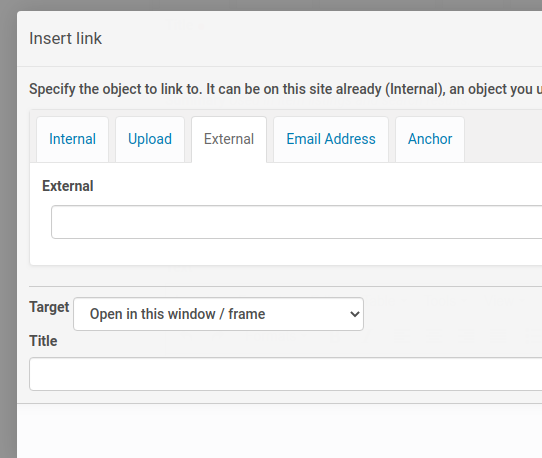
After:
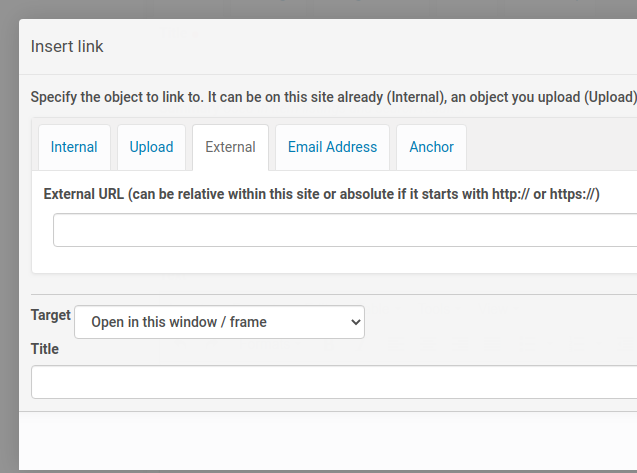
comment created time in 2 months
startedphoenixframework/phoenix
started time in 2 months
pull request commentplone/Products.CMFPlone
Put back content type icons in the Add new... menu. (Plone 5.1.x)
Please note that https://github.com/plone/plone.app.content/pull/209 that goes with https://github.com/plone/mockup/pull/1008 is merged. So all good to merge.
comment created time in 3 months
push eventplone/buildout.coredev
commit sha bce2f7ba0229349877ef14879d1f8864e99d3dbe
checkout plonetheme.barceloneta
push time in 3 months
push eventplone/plonetheme.barceloneta
commit sha 7166a30c15512cff04b21017d5946f9271712ec6
up to date barceloneta-compiled.css.map
push time in 3 months
issue closedplone/plonetheme.barceloneta
active form tabs should not have a bottom border
(This is for the 2.x LESS-based version. Seems to be fixed in master SCSS)
See image; here the Resource Types is the chosen tab yet it has a bottom border, making it impossible to distinguish which is active tab.
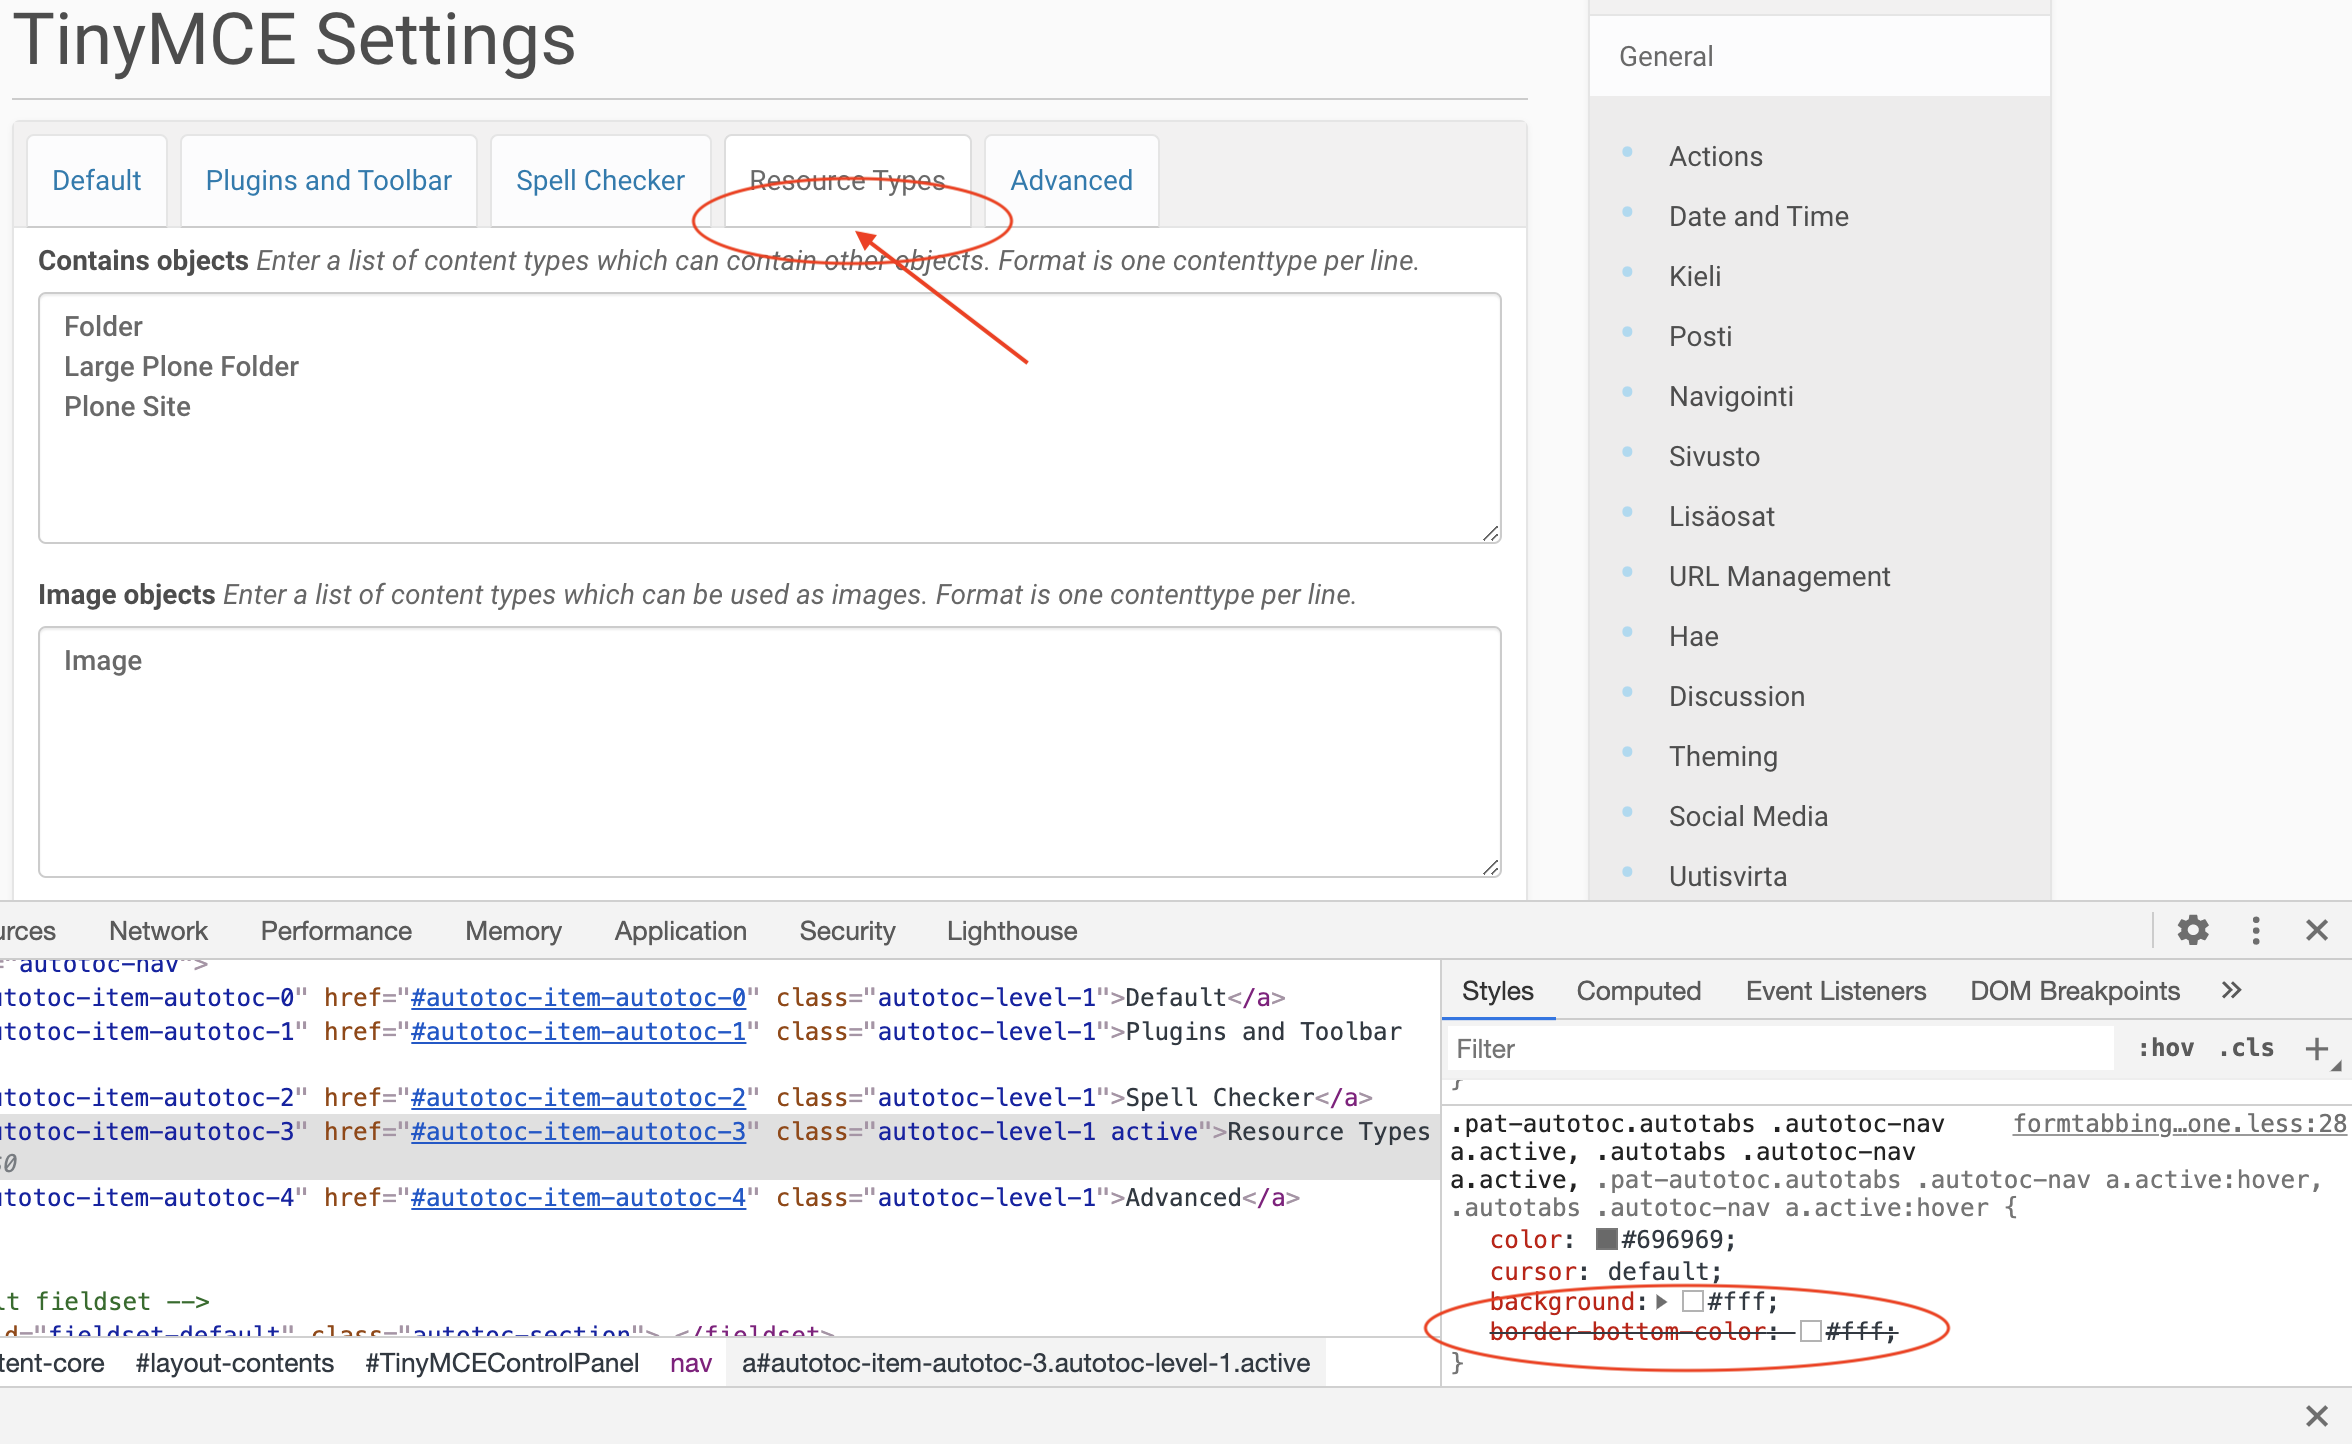
Could be fixed by adding !important here:
https://github.com/plone/plonetheme.barceloneta/blob/2.x/plonetheme/barceloneta/theme/less/formtabbing.plone.less#L32
EDIT: that seems to be not enough; turning the line into border-bottom: 1px solid @plone-portlet-content-bg ~'!important'; seems to work better.
closed time in 3 months
petri
push eventplone/plonetheme.barceloneta
commit sha 14b50aad7da6d5cd6e1111a01a9b92252f796415
fix #210 (distinguish active autotab)
commit sha 26c071a3e789e266b5f6a0dd5896ca16e1e8eef1
fix autotabs border color and move the fix to formtabbing.plone.less
commit sha b35929167b9d5f460daa80c8be2883a1cbf8eb3d
Merge pull request #211 from plone/fix-tabs-210 fix #210 (distinguish active autotab)
push time in 3 months
PR merged plone/plonetheme.barceloneta
For the 2.x LESS-based branch. Adds a specific rule in main less as suggested by @vincentfretin , rather than an !important.
pr closed time in 3 months
push eventplone/plonetheme.barceloneta
commit sha 26c071a3e789e266b5f6a0dd5896ca16e1e8eef1
fix autotabs border color and move the fix to formtabbing.plone.less
push time in 3 months
push eventplone/plonetheme.barceloneta
commit sha 4b0b3bc252631f433a2ab0d7f19439820c6d00b1
fix autotabs border color and move the fix to formtabbing.plone.less
push time in 3 months
pull request commentplone/plonetheme.barceloneta
fix #210 (distinguish active autotab)
The border bottom color for non active tabs was not right. I fixed it in https://github.com/plone/plonetheme.barceloneta/pull/211/commits/8325b279eac5b17a2d929d83cbf28824c0e2e916
comment created time in 3 months
push eventplone/plonetheme.barceloneta
commit sha 8325b279eac5b17a2d929d83cbf28824c0e2e916
fix autotabs border color and move the fix to formtabbing.plone.less
push time in 3 months
pull request commentplone/plone.staticresources
@jenkins-plone-org please run jobs
comment created time in 3 months
pull request commentplone/Products.CMFPlone
Put back content type icons in the Add new... menu. (Plone 5.1.x)
@jenkins-plone-org please run jobs
comment created time in 3 months
push eventplone/plone.staticresources
commit sha f06bf5b17379d0360c93467d141230628741cfa2
add changelog entry
push time in 3 months
push eventplone/Products.CMFPlone
commit sha 2b55090b2dc659189fa5d58b0cc66f87269638e6
add changelog entry
push time in 3 months
push eventplone/Products.CMFPlone
commit sha c38a8b0e26cb6a8d586952cb9fc01397f01cf5c5
add changelog entry
push time in 3 months