








rust-lang/miri 1366
An interpreter for Rust's mid-level intermediate representation
fasterthanlime/jooc-legacy 114
:crocodile: The historical, initial implementation of an ooc compiler in Java
relrod/bing_translator-gem 112
A simple Ruby interface to Bing's translation API.
Everyone who has a merged pull request is invited to become an admin of this repo.
:ledger: leg grammar for ooc
ooc development kit - collections, text manipulation, math, crypto, os - all nice and portable
Official documentation for ooc 0.3+
ooc compatibility kit - test suite and tools to verify the compliance of an ooc implementation
A stack-based virtual machine written in C
pull request commentdenoland/deno
fix(cli): Use safe shell escaping in `deno install`
Added cfg!(windows) to tests and rebased. All behaviour on Windows should be unchanged before and after this PR.

comment created time in 5 days
push eventsolson/deno
commit sha d596e85d71fed2ee3de23291499120e08d7480e6
fix(cli/installer): use safe shell escaping
commit sha 6082cd5416124581918bc3e6fc384b9f302788bc
fix(cli/installer): use `exec` in installed scripts Fixes #3961
commit sha b38a35e198d9993d5fbeab580019524eb6876b9c
test(cli/installer): add shell escaping test
commit sha 1006d4388aa1cf31881b7cacd43cd3745cb0d9d2
test(cli/installer): do separate windows and unix tests
push time in 5 days
push eventsolson/deno
commit sha 8c328ec1a3aef69812353f7ef7ceb5a8bb6c228b
fix(cli/installer): use safe shell escaping
commit sha 008b82c08d2489243e3f1c83f8cb2b7eaaf1ff14
fix(cli/installer): use `exec` in installed scripts Fixes #3961
commit sha 8de5aeb60f6814319f665063b0dc402822772279
test(cli/installer): add shell escaping test
commit sha 0fa848d55ed1f5427489663c4029c6da60341882
test(cli/installer): do separate windows and unix tests
push time in 5 days
issue openeddenoland/deno
Panics should not unwind into non-Rust code
I just noticed and investigated something in the output in https://github.com/denoland/deno/issues/7953 that I somehow missed the first time around, after the usual panic message:
fatal runtime error: failed to initiate panic, error 5
fish: “deno” terminated by signal SIGABRT (Abort)
A normal Rust panic does not SIGABRT. With the standard panic handler, first they print the panic message and backtrace, and then they try to unwind. That is where this panic aborts, because it happens inside a callback called by V8 and the unwinder gets confused by outer V8 stack frames. (In fact, it may be getting confused specifically by V8 JIT frames that don't show up in the gdb output.)
<details><summary>click for gdb backtrace (13 is C++ which calls 12 which is Rust)</summary>
(gdb) bt
#0  0x00007fceaaa3808a in raise () from /nix/store/9df65igwjmf2wbw0gbrrgair6piqjgmi-glibc-2.31/lib/libc.so.6
#1  0x00007fceaaa22528 in abort () from /nix/store/9df65igwjmf2wbw0gbrrgair6piqjgmi-glibc-2.31/lib/libc.so.6
#2  0x00005653a2f605a7 in std::sys::unix::abort_internal () at library/std/src/sys/unix/mod.rs:167
#3  0x00005653a2f60595 in std::sys_common::util::abort () at library/std/src/sys_common/util.rs:19
#4  0x00005653a2f6053d in std::panicking::rust_panic () at library/std/src/panicking.rs:620
#5  0x00005653a2f603ba in std::panicking::rust_panic_with_hook () at library/std/src/panicking.rs:588
#6  0x00005653a2f5ff58 in std::panicking::begin_panic_handler::{{closure}} () at library/std/src/panicking.rs:476
#7  0x00005653a2f5ff24 in std::sys_common::backtrace::__rust_end_short_backtrace () at library/std/src/sys_common/backtrace.rs:153
#8  0x00005653a2f5fedd in rust_begin_unwind () at library/std/src/panicking.rs:475
#9  0x00005653a2c20210 in core::panicking::panic_fmt () at library/core/src/panicking.rs:85
#10 0x00005653a2c272e2 in core::option::expect_none_failed () at library/core/src/option.rs:1221
#11 0x00005653a2a88d85 in core::result::Result<T,E>::unwrap ()
#12 0x00005653a2b8ad18 in <deno::inspector::InspectorSession as rusty_v8::inspector::ChannelImpl>::send_response ()
#13 0x00005653a34e2a77 in non-virtual thunk to v8_inspector::V8InspectorSessionImpl::SendProtocolResponse(int, std::__1::unique_ptr<v8_crdtp::Serializable, std::__1::default_delete<v8_crdtp::Serializable> >) ()
#14 0x00005653a34faa21 in v8_crdtp::DomainDispatcher::sendResponse(int, v8_crdtp::DispatchResponse const&, std::__1::unique_ptr<v8_crdtp::Serializable, std::__1::default_delete<v8_crdtp::Serializable> >) ()
    at ../../../../v8/third_party/inspector_protocol/crdtp/dispatch.cc:473
#15 0x00005653a34fa890 in v8_crdtp::DomainDispatcher::Callback::sendIfActive(std::__1::unique_ptr<v8_crdtp::Serializable, std::__1::default_delete<v8_crdtp::Serializable> >, v8_crdtp::DispatchResponse const&) ()
    at ../../../../v8/third_party/inspector_protocol/crdtp/dispatch.cc:442
#16 0x00005653a39a84a7 in v8_inspector::protocol::Runtime::EvaluateCallbackImpl::sendSuccess(std::__1::unique_ptr<v8_inspector::protocol::Runtime::RemoteObject, std::__1::default_delete<v8_inspector::protocol::Runtime::RemoteObject> >, v8_crdtp::detail::PtrMaybe<v8_inspector::protocol::Runtime::ExceptionDetails>) () at gen/v8/src/inspector/protocol/Runtime.cpp:879
#17 0x00005653a34f1245 in v8_inspector::(anonymous namespace)::EvaluateCallbackWrapper<v8_inspector::protocol::Runtime::Backend::EvaluateCallback>::sendSuccess(std::__1::unique_ptr<v8_inspector::protocol::Runtime::RemoteObject, std::__1::default_delete<v8_inspector::protocol::Runtime::RemoteObject> >, v8_crdtp::detail::PtrMaybe<v8_inspector::protocol::Runtime::ExceptionDetails>) () at ../../../../v8/src/inspector/v8-runtime-agent-impl.cc:76
#18 0x00005653a39b1761 in v8_inspector::InjectedScript::ProtocolPromiseHandler::thenCallback(v8::Local<v8::Value>) () at ../../../../v8/src/inspector/injected-script.cc:217
#19 0x00005653a39b0f8b in v8_inspector::InjectedScript::ProtocolPromiseHandler::thenCallback(v8::FunctionCallbackInfo<v8::Value> const&) () at ../../../../v8/src/inspector/injected-script.cc:125
#20 0x00005653a376d1a9 in v8::internal::FunctionCallbackArguments::Call(v8::internal::CallHandlerInfo) () at ../../../../v8/src/api/api-arguments-inl.h:158
#21 0x00005653a376c6c0 in v8::internal::MaybeHandle<v8::internal::Object> v8::internal::(anonymous namespace)::HandleApiCallHelper<false>(v8::internal::Isolate*, v8::internal::Handle<v8::internal::HeapObject>, v8::internal::Handle<v8::internal::HeapObject>, v8::internal::Handle<v8::internal::FunctionTemplateInfo>, v8::internal::Handle<v8::internal::Object>, v8::internal::BuiltinArguments) () at ../../../../v8/src/builtins/builtins-api.cc:111
#22 0x00005653a376bc9b in v8::internal::Builtin_Impl_HandleApiCall(v8::internal::BuiltinArguments, v8::internal::Isolate*) () at ../../../../v8/src/builtins/builtins-api.cc:141
#23 0x00005653a36306b8 in Builtins_CEntry_Return1_DontSaveFPRegs_ArgvOnStack_BuiltinExit ()
#24 0x00005653a367fbbb in Builtins_PromiseFulfillReactionJob ()
#25 0x00005653a35e3037 in Builtins_RunMicrotasks ()
#26 0x00005653a35c07f8 in Builtins_JSRunMicrotasksEntry ()
#27 0x00005653a31a114f in v8::internal::(anonymous namespace)::Invoke(v8::internal::Isolate*, v8::internal::(anonymous namespace)::InvokeParams const&) () at ../../../../v8/src/execution/execution.cc:383
#28 0x00005653a31a17e0 in v8::internal::(anonymous namespace)::InvokeWithTryCatch(v8::internal::Isolate*, v8::internal::(anonymous namespace)::InvokeParams const&) () at ../../../../v8/src/execution/execution.cc:428
#29 0x00005653a31a18de in v8::internal::Execution::TryRunMicrotasks(v8::internal::Isolate*, v8::internal::MicrotaskQueue*, v8::internal::MaybeHandle<v8::internal::Object>*) () at ../../../../v8/src/execution/execution.cc:505
#30 0x00005653a31c9405 in RunMicrotasks () at ../../../../v8/src/execution/microtask-queue.cc:165
#31 0x00005653a31c9227 in v8::internal::MicrotaskQueue::PerformCheckpoint(v8::Isolate*) () at ../../../../v8/src/execution/microtask-queue.cc:117
#32 0x00005653a31b8e38 in v8::internal::Isolate::FireCallCompletedCallback(v8::internal::MicrotaskQueue*) () at ../../../../v8/src/execution/isolate.cc:4066
#33 0x00005653a312e670 in v8::Function::Call(v8::Local<v8::Context>, v8::Local<v8::Value>, int, v8::Local<v8::Value>*) () at ../../../../v8/src/api/api.cc:4993
#34 0x00005653a2f383f2 in rusty_v8::function::<impl rusty_v8::data::Function>::call ()
#35 0x00005653a2bc346a in <deno::worker::Worker as core::future::future::Future>::poll ()
#36 0x00005653a2aeeae3 in <core::future::from_generator::GenFuture<T> as core::future::future::Future>::poll ()
#37 0x00005653a2ba9475 in deno::repl::run::{{closure}} ()
#38 0x00005653a2af9a68 in <core::future::from_generator::GenFuture<T> as core::future::future::Future>::poll ()
#39 0x00005653a2ab867b in tokio::runtime::Runtime::block_on ()
#40 0x00005653a2bcf39d in deno::main ()
#41 0x00005653a2a5fb48 in std::sys_common::backtrace::__rust_begin_short_backtrace ()
#42 0x00005653a2bd62ef in main ()
</details>
As I understand it, we should try to prevent ever unwinding into non-Rust stack frames by making callbacks like this one use catch_unwind and then either manually exit or convert the error into something that can be sensibly passed up into V8, whatever is most appropriate in each case. This should be done wherever Rust code is called from non-Rust code in Deno and its dependencies.
Quoting the catch_panic docs:
It is currently undefined behavior to unwind from Rust code into foreign code, so this function is particularly useful when Rust is called from another language (normally C). This can run arbitrary Rust code, capturing a panic and allowing a graceful handling of the error.
created time in 5 days
push eventsolson/deno
commit sha 92edc364426ddb4c80292ebe7e702c02f9344c5b
refactor: use futures and serde_json from deno_core (#7614)
commit sha 5c2e499c3a70ec58b7f5adab3a7801d601f9b2e1
fix: Response.arrayBuffer() doesn't return promise (#7618)
commit sha 9caeff3208a33098418ac2c64414010a3060a362
fix(cli/repl): interpret object literals as expressions (#7591)
commit sha 5a8a4da524a38fcade24ca7645ae0c034602b9aa
docs: minor documentation improvement (#7603) Closes #7602
commit sha 43fa68e5895b05a78c84d5837eaa754204b4b99c
docs: V8 is a JavaScript engine, not a runtime (#7619)
commit sha cca8856fbf9552ccd7c6fe4eb6cbb8d521978a21
refactor(cli/coverage): remove dependency on global state (#7616) This removes the dependency on global state and instead relies on the runtime's internal state to get the script sources it saw when it collected code coverage for them.
commit sha c30c782c2c22d725c007623dbf43009999a2b184
fix(logger): change log level to which prefix added (#7582)
commit sha a33315aaa70884c10968669c31adf3c6bb142e72
fix(cli/console): quote object symbol keys that are invalid identifiers (#7553)
commit sha a43984c9cfcea852ca18e1c575f9acdb8f023a5a
refactor(cli/fmt_errors): Color stack traces in Rust (#7628)
commit sha dd1cd4d95237359acd822143265d7d2365bf928c
fix: clearing timers race condition (#7617)
commit sha f601721851bdd64ee5b40bd3d408df063691b425
feat(std/node): implement getSystemErrorName() (#7624)
commit sha cf0c49191e9be862027f74f39318a3479fce3ba2
chore(std/hash): update crates (#7631)
commit sha 68fd7a927b26c3e72cf73515821450f3aa252014
refactor(core): support error stack, remove js_check (#7629) This commit adds support for stack traces in "deno_core". Implementation of "Display" trait for "JsError" has been updated and in consequence "deno_core::js_check" became obsolete and removed.
commit sha 751bb45a0a4ca4ab3baf5e5037c0b10f0430aeb6
fix: ignore fileExists in tsc host (#7635) Fixes #7630
commit sha ffd08a2249b3aab1e8e70d9cef9c350ab41f22a7
Actually remove js_check (#7636)
commit sha 49807ac4ac225f7a07282f6410476f529f7ad821
feat: bump TypeScript to 4.0.3 (#7637)
commit sha 8a6a3904574375e109ef98aaa07af11a9c994b89
docs: ts upgrade instructions to exclude some .d.ts files (#7638)
commit sha 29dd62b08cc1a6a95b242b7269fe1b8deefa7a24
fix(watch): watch importmap file for changes (#7580)
commit sha d68fb813428f31b21b8a46cdde21d9ab5170abdc
fix(cli/console): enclose symbol keys in brackets (#7642) This encloses symbol keys when used in objects with brackets (e.g [Symbol("Symbol.iterator")]).
commit sha 71c2497fd47829a177b81a884b75f705272156b2
Add example for deno_core (#7611)
push time in 6 days
Pull request review commentdenoland/deno
fix(cli/rt/console): fix inspection of Function
unitTest(function consoleTestStringifyCircular(): void { }); /* eslint-enable @typescript-eslint/explicit-function-return-type */ +unitTest(function consoleTestStringifyFunctionWithPrototypeRemoved(): void {+ const f = function f() {};+ Reflect.setPrototypeOf(f, null);+ assertEquals(stringify(f), "[Function: f]");+ const af = async function af() {};+ Reflect.setPrototypeOf(af, null);+ assertEquals(stringify(af), "[Function: af]");+ const gf = function gf() {};+ Reflect.setPrototypeOf(gf, null);+ assertEquals(stringify(gf), "[Function: gf]");+ const agf = function agf() {};+ Reflect.setPrototypeOf(agf, null);+ assertEquals(stringify(agf), "[Function: agf]");
@bartlomieju https://github.com/denoland/deno/issues/7962

comment created time in 7 days
issue openeddenoland/deno
Typos in `consoleTestStringifyFunctionWithPrototypeRemoved` unit test
https://github.com/denoland/deno/blob/f42d0fc99e37bb0583cddeca5367a1dcf83d53b8/cli/tests/unit/console_test.ts#L350-L363
In this unit test, gf and agf are currently both regular functions but appear to be intended to test against GeneratorFunction and AsyncGeneratorFunction the same way f and af are testing Function and AsyncFunction. Note that the output shouldn't change since it's intentionally setting prototypes to null to test the fallback to "Function". As discussed at https://github.com/denoland/deno/pull/7930#discussion_r504127789.
created time in 7 days
Pull request review commentdenoland/deno
fix(cli/rt/console): fix inspection of Function
unitTest(function consoleTestStringifyCircular(): void { }); /* eslint-enable @typescript-eslint/explicit-function-return-type */ +unitTest(function consoleTestStringifyFunctionWithPrototypeRemoved(): void {+ const f = function f() {};+ Reflect.setPrototypeOf(f, null);+ assertEquals(stringify(f), "[Function: f]");+ const af = async function af() {};+ Reflect.setPrototypeOf(af, null);+ assertEquals(stringify(af), "[Function: af]");+ const gf = function gf() {};+ Reflect.setPrototypeOf(gf, null);+ assertEquals(stringify(gf), "[Function: gf]");+ const agf = function agf() {};+ Reflect.setPrototypeOf(agf, null);+ assertEquals(stringify(agf), "[Function: agf]");
No, I'm saying they should be declared that way here in the test, as in const gf = function* gf() {}; to match async function af above, presumably to test this "set prototype to null" manipulation on all 4 of Function, AsyncFunction, GeneratorFunction, and AsyncGeneratorFunction. Currently, gf and agf are just testing the same thing as f.
comment created time in 7 days
Pull request review commentdenoland/deno
fix(cli/rt/console): fix inspection of Function
unitTest(function consoleTestStringifyCircular(): void { }); /* eslint-enable @typescript-eslint/explicit-function-return-type */ +unitTest(function consoleTestStringifyFunctionWithPrototypeRemoved(): void {+ const f = function f() {};+ Reflect.setPrototypeOf(f, null);+ assertEquals(stringify(f), "[Function: f]");+ const af = async function af() {};+ Reflect.setPrototypeOf(af, null);+ assertEquals(stringify(af), "[Function: af]");+ const gf = function gf() {};+ Reflect.setPrototypeOf(gf, null);+ assertEquals(stringify(gf), "[Function: gf]");+ const agf = function agf() {};+ Reflect.setPrototypeOf(agf, null);+ assertEquals(stringify(agf), "[Function: agf]");
I know this is already merged, but was this intended to test generator functions and async generator functions? (function* gf() {} and async function* agf() {})
comment created time in 7 days
issue openeddenoland/deno
REPL panics related to invalid unicode
I found a way to trip two different Rust panic messages in the REPL:
$ deno --version
deno 1.4.6
v8 8.7.220.3
typescript 4.0.3

$ deno
Deno 1.4.6
exit using ctrl+d or close()
> '\u{1f3b5}'
"🎵"
> '\u{1f3b5}'[0]
thread 'main' panicked at 'called `Result::unwrap()` on an `Err` value: Error("unexpected end of hex escape", line: 1, column: 60)', cli/inspector.rs:859:54
note: run with `RUST_BACKTRACE=1` environment variable to display a backtrace
fatal runtime error: failed to initiate panic, error 5
fish: “deno” terminated by signal SIGABRT (Abort)

$ deno
Deno 1.4.6
exit using ctrl+d or close()
> '\u{1f3b5}'[1]
thread 'main' panicked at 'called `Result::unwrap()` on an `Err` value: Error("lone leading surrogate in hex escape", line: 1, column: 59)', cli/inspector.rs:859:54
note: run with `RUST_BACKTRACE=1` environment variable to display a backtrace
fatal runtime error: failed to initiate panic, error 5
fish: “deno” terminated by signal SIGABRT (Abort)
Note that these panics only occur in the REPL, and regular Deno code is unaffected as far as I can tell.
cc @caspervonb
created time in 7 days
issue commentdenoland/deno
Should evaluation errors in the read-eval-print-loop go to stdout?
I agree with your rationale. I would reserve stderr for things like Rust panics (it's where they go by default) and other implementation errors in the REPL itself, and otherwise expect all output to go to stdout.
I took a look at the mentioned languages and was slightly surprised to find this:
| Language | REPL errors written to |
|---|---|
| Ruby | stdout |
| Python | stderr |
| Lua | stderr |
Given that I never noticed any difference between these, it probably doesn't matter too much whether we use stdout or stderr.

comment created time in 7 days
issue commentdenoland/deno
Deno.repl() feature suggestion
As for running something in the global context; is there anything wrong with just using pipes to stdin?
Yes, this will disable interactive readline features. I'm not familiar with unbuffer and didn't have it installed (so this would be an extra dependency for this usecase, and one that may not work on Windows at all), but when I try to do things like (echo "console.log('do your stuff')" && cat) | unbuffer deno it seems to hang and ignore input.
In general, I've never seen anything piping to an interactive REPL work well.

comment created time in 8 days
issue openedsharkdp/bat
Show headers only when multiple files are passed
Sorry if this has already been asked, but I couldn't find it.
Could it be made possible to configure bat to show headers (--style=header) only when more than one file is passed? I like to keep my --style quite minimal, and when viewing a single file, the filename is usually just extra noise to me, but with multiple files it's practically a necessity. Thanks!
created time in 8 days
push eventsolson/dotfiles
commit sha 24803770bd99a889de5840d4f2dc8521a10b1bf4
remove unused bin
push time in 8 days
push eventsolson/dotfiles
commit sha b0c331443bb5e63567255e4fd86afb11535e488b
remove unused config
push time in 8 days
push eventsolson/dotfiles
commit sha 73cfd9aba756e45e3cdffb2acf8f90f30e946621
fish: stop setting PATH — handled in bashrc
commit sha 13efda52d4c28793547e781ba98918307f3c8d82
use simpler nvim MANPAGER
commit sha 76abe6758663d856c24841e0ff0779f73d98419e
remove now-irrelevant ssh-agent config
commit sha 242953515e40d4a1d121ffc2e7f1dae4891b6a8a
move environment variables to bashrc
push time in 8 days
push eventsolson/dotfiles
commit sha 75cc2a5df022790d9a77cb98a96072bad38436da
move bins from .bin to .local/bin
commit sha 5ff583644ec820722989f2c2d58142439e4871f8
move ~/.netrc to ~/.local/share/netrc
commit sha d11ef6eb0c13bb512fcaa721a6adb631f46c7acd
build a minimal PATH from scratch
push time in 8 days
push eventsolson/dotfiles
commit sha 8eaab8be4e84f388668c7f72b848df97e0e42118
bash: move all configuration to .bashrc
commit sha 42e44c1c5e68db99bce57e0b85ec51ffda4ed058
force many programs to use XDG directories
commit sha 1f4fc3afa17fa501693f661cbeace591b0dda4c9
tmux: remove
push time in 8 days
issue commentNixOS/nixpkgs
Qt applications use Windows style regardless of style selected in KDE settings
It may be relevant that, for some reason, my KDE programs like plasmashell or kate are linking against Qt 5.14.2 libraries, while keepassxc and qjackctl are linking against Qt 5.15.0 libraries. The breeze-qt5 package is built under the plasma set of packages and also links against Qt 5.14.2 libraries.

comment created time in 8 days
issue commentNixOS/nixpkgs
Qt applications use Windows style regardless of style selected in KDE settings
I ran with QT_DEBUG_PLUGINS=1 and found this:
Cannot load library /nix/store/0mpi3gn7v5hah1h2lc5my3a0n7rfzngh-breeze-qt5-5.18.5-bin/lib/qt-5.14.2/plugins/styles/breeze.so: (/nix/store/g6r4b8vmj30v5a6cjwxz936h90xcxj7m-qtdeclarative-5.14.2/lib/libQt5Quick.so.5: undefined symbol: _ZN4QRhi10newSamplerEN11QRhiSampler6FilterES1_S1_NS0_11AddressModeES2_, version Qt_5_PRIVATE_API)
QLibraryPrivate::loadPlugin failed on "/nix/store/0mpi3gn7v5hah1h2lc5my3a0n7rfzngh-breeze-qt5-5.18.5-bin/lib/qt-5.14.2/plugins/styles/breeze.so" : "Cannot load library /nix/store/0mpi3gn7v5hah1h2lc5my3a0n7rfzngh-breeze-qt5-5.18.5-bin/lib/qt-5.14.2/plugins/styles/breeze.so: (/nix/store/g6r4b8vmj30v5a6cjwxz936h90xcxj7m-qtdeclarative-5.14.2/lib/libQt5Quick.so.5: undefined symbol: _ZN4QRhi10newSamplerEN11QRhiSampler6FilterES1_S1_NS0_11AddressModeES2_, version Qt_5_PRIVATE_API)"
Those are some annoyingly long lines, but the relevant bit is the loading of breeze.so complaining about an undefined symbol with this name:
> c++filt _ZN4QRhi10newSamplerEN11QRhiSampler6FilterES1_S1_NS0_11AddressModeES2_
QRhi::newSampler(QRhiSampler::Filter, QRhiSampler::Filter, QRhiSampler::Filter, QRhiSampler::AddressMode, QRhiSampler::AddressMode)
comment created time in 8 days
issue commentNixOS/nixpkgs
Theme is broken on several tabs of systemsettings5
How are we supposed to get the fix? For me (on nixos-unstable), it still looks like the widgets in the original post:

With a manually-specified QT_QUICK_CONTROLS_STYLE=Plasma it applies a native widget look, but it's broken in a different way (see "Orientation"):

Am I missing something, or can we reopen this issue?

comment created time in 8 days
issue commentNixOS/nixpkgs
Qt applications use Windows style regardless of style selected in KDE settings
I have the same problem with KeePassXC:
$ keepassxc -style=Breeze
QApplication: invalid style override 'Breeze' passed, ignoring it.
        Available styles: Breeze, Windows, Fusion
But setting -style=Fusion or -style=Windows explicitly actually works, so the problem is Breeze-specific, at least on my machine. I confirmed the same thing with qjackctl just now.
comment created time in 8 days
pull request commentNixOS/nixpkgs
nixos/x11: Respect XCOMPOSECACHE/XDG_DATA_HOME if set in xsession-wrapper
LGTM, I'd love to see this get merged. I've been trying to make my ~ more XDG Base Directory compliant.

comment created time in 8 days
issue commentNixOS/nixpkgs
SUID wrappers die when executed with NO_NEW_PRIVS
I just got surprised by this while trying out bubblewrap for the first time. To confirm, it dies on the same assertion:
bash:~$ sudo echo foo
sudo: /nix/store/v6l2sacryfr88yqq0pq7sia8wfgm9q31-wrapper.c:203: main: Assertion `!(st.st_mode & S_ISUID) || (st.st_uid == geteuid())' failed.
Aborted (core dumped)

comment created time in 10 days
push eventsolson/dotfiles
commit sha 86fafa8b37d9fd15ecaa1662e6a5d20268362e9a
xcompose: add pin emoji
commit sha e6b68dfda2d75e87ba124e34b9d0f4022b2d9804
broot: add `s` shortcut for `toggle_sizes`
push time in 10 days
push eventsolson/dotfiles
commit sha 90f079f94df841d73ceb76f3d20a643ea8ac2743
broot: init
push time in 10 days
push eventsolson/broot
commit sha c38c428a2a9f8f3f02af9183c58880abf08a7896
use PATH instead of absolute paths for all verbs The `chmod` verb was already using PATH, but others were using absolute paths that don't necessarily exist on every Linux distro.
push time in 10 days
push eventsolson/dotfiles
commit sha 3df47ddcee031423e162369860c764c65c93d8ea
nvim: customize look of diffs
commit sha c4ebe58ab326b6027545f2bd92e078b966a5722c
git: use nvim as difftool
commit sha cebe1cb25265a0ad5f054ee5153e9b588f037be9
fix install.sh
push time in 10 days
PR opened Canop/broot
Before this PR
The chmod verb was already using PATH, but others were using absolute paths that don't necessarily exist on every Linux distro. For example, on NixOS there is no /bin/rm, so the broot package rewrites /bin/ to a path in the "Nix store" (this is typical), which works just fine, but makes the UI's verb preview very verbose:

The chmod verb specifies chmod instead of /bin/chmod (relying on PATH lookup), which works just as well and has a cleaner verb preview:
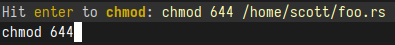
After this PR
I made all verbs work like chmod does, which cleans up the preview for me:
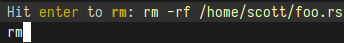
pr created time in 10 days
fork solson/broot
A new way to see and navigate directory trees : https://dystroy.org/broot
fork in 10 days
push eventsolson/dotfiles
commit sha d3776436fd85654ca993adbb74db955be483e327
vim: Use proper script-id function references.
push time in 10 days
push eventsolson/dotfiles
commit sha 9ba4d7c76e76f09ce2dde0605b761e22528a7d60
fish: Add alias for running broot on a nix package.
push time in 10 days
issue commentdenoland/deno
More granular priveldge separation
type PermissionDescriptor = RunPermissionDescriptor | ReadPermissionDescriptor | WritePermissionDescriptor | NetPermissionDescriptor | EnvPermissionDescriptor | PluginPermissionDescriptor | HrtimePermissionDescriptor

interface ReadPermissionDescriptor
  name: "read"
  path?: string
These types imply Deno.permissions.revoke({ name: "read", path: "/a/b/c" }) should work (and likewise for write).
One thing I'm not sure of is whether we actually can implement a pledge(2)-like yet. It seems like we would need a function to revoke "all except for this explicit allowlist" (like pledge(2)), or at least a way to enumerate all currently granted permissions so we could revoke all outside the allowlist manually.

comment created time in 11 days
startedCanop/broot
started time in 12 days
issue commentrust-lang/rust
Implementation detail exposed in short backtrace (RUST_BACKTRACE=1)
I reported this since it was a bit confusing that the Rust announcement post itself included the irrelevant (to the end user) call_once line. It seems unfortunate to me that debug mode has the more confusing backtrace in this case — I probably use backtraces most often during development, without optimizations.
comment created time in 12 days
issue openedrust-lang/rust
Implementation detail exposed in short backtrace (RUST_BACKTRACE=1)
Given this file foo.rs:
fn main() {
    panic!();
}
A short backtrace for this panic would ideally include only std::panicking::begin_panic and foo::main. And, indeed, the implementing PR has a test for this output:
https://github.com/rust-lang/rust/blob/5792840bf52e4cf77ebb7b3bd93e9c90dd23f4e7/src/test/ui/panics/issue-47429-short-backtraces.run.stderr#L1-L5
However, this is how the backtrace actually looks with various flags:
rustc (no flags; debug mode)
   0: std::panicking::begin_panic
   1: foo::main
   2: core::ops::function::FnOnce::call_once
rustc -O (release mode)
   0: std::panicking::begin_panic
   1: foo::main
rustc -O -C debuginfo=1 (release mode with debuginfo)
   0: std::panicking::begin_panic
             at ./.rustup/toolchains/nightly-x86_64-unknown-linux-gnu/lib/rustlib/src/rust/library/std/src/panicking.rs:505
   1: foo::main
             at ./foo.rs:2
   2: core::ops::function::FnOnce::call_once
             at ./.rustup/toolchains/nightly-x86_64-unknown-linux-gnu/lib/rustlib/src/rust/library/core/src/ops/function.rs:227
So I think the __rust_begin_short_backtrace implementation needs to account for this extra stack frame when it isn't optimized out by release mode. The test mentioned above only passes because it's compiled with -O:
https://github.com/rust-lang/rust/blob/5792840bf52e4cf77ebb7b3bd93e9c90dd23f4e7/src/test/ui/panics/issue-47429-short-backtraces.rs#L3
I tested this on 1.47.0 stable and a nightly version:
<details><summary><code>rustc --version --verbose</code></summary>
rustc 1.47.0 (18bf6b4f0 2020-10-07)
binary: rustc
commit-hash: 18bf6b4f01a6feaf7259ba7cdae58031af1b7b39
commit-date: 2020-10-07
host: x86_64-unknown-linux-gnu
release: 1.47.0
LLVM version: 11.0

rustc 1.49.0-nightly (91a79fb29 2020-10-07)
binary: rustc
commit-hash: 91a79fb29ac78d057d04dbe86be13d5dcc64309a
commit-date: 2020-10-07
host: x86_64-unknown-linux-gnu
release: 1.49.0-nightly
LLVM version: 11.0
</details>
ref #75048 cc @eggyal
created time in 12 days
push eventsolson/dotfiles
commit sha 32e5130b4ee94e0b9933de2a7296992475bcec3f
git: Set config filetype for vim.
commit sha 705d4c3282c845a5f54f8abaaa96f08695b68121
git: Remove ghq config.
push time in 12 days
push eventsolson/dotfiles
commit sha 7db47859dda4b176f796596da9c82737de2629dc
git: Reformat config.
commit sha ad6e4d72284c1c7ee240f5edc17a90ff1cd5c92c
git: Use diff-so-fancy unicode ruler.
push time in 12 days
push eventsolson/dotfiles
commit sha 25a321258e9e87b7bb80c2ec94582560d6626207
vim: Add coc-diagnostic for shellcheck.
commit sha 9eee54fab264fbb9d460a1fe9d4149c672aaafeb
git: Use verbose commit (diff in message editor).
commit sha 4406579b8fe267e3bddc008d4f63c438f8f5ecbf
vim: Show separate hint lines with rust-analyzer.
commit sha e21931cbd1355d7ed5b1aafe425b6286758b43e9
vim: Improve Coc diagnostic colors.
push time in 12 days
issue commentdenoland/deno
More granular priveldge separation
On Deno --unstable, I think you may be able to implement something like pledge(2) already (see deno doc --unstable --builtin Deno.Permissions):
  revoke(desc: PermissionDescriptor): Promise<PermissionStatus>
    Revokes a permission, and resolves to the state of the permission.

          const status = await Deno.permissions.revoke({ name: "run" });
          assert(status.state !== "granted")
Which would let a program start with broad permissions, do some setup, and then restrict to much narrower permissions for the rest of its runtime, so I guess this issue ties into the possible stabilization of that API. Is there anything else particular to pledge(2) that should be discussed here?
comment created time in 12 days
issue commentbe5invis/Iosevka
U+FFFD "REPLACEMENT CHARACTER" �
Usually, U+FFFD is used to represent conversion error
This is correct — and that's precisely the reason it came up when I was debugging code that does unicode conversions.
It's included in these fonts, for example:

comment created time in 15 days
issue openedbe5invis/Iosevka
U+FFFD "REPLACEMENT CHARACTER" �
- The requested character is...
- [ ] Latin
- [ ] Cyrillic
- [ ] Greek
- [ ] Punctuation
- [x] Symbol
- [x] Some other monospace/programming fonts supported this character. Provide images below.
I was dumping some data in a string while programming and noticed this rendering issue in my terminal, where I am using Iosevka:

I figured out the issue is that the U+FFFD � character was being rendered in Noto Sans Mono (my system monospace fallback) because Iosevka doesn't support the character, as far as I can tell. If my method of checking was correct, I think over half of my monospace fonts support this character, so it would be great if Iosevka did as well.
created time in 15 days
issue closeddenoland/deno
Some interfaces are hidden from `deno doc`
I noticed that deno doc --builtin WebSocket only shows this:
var WebSocket: { prototype: WebSocket; CLOSED: number; CLOSING: number; CONNECTING: number; OPEN: number; }
While if you browse through deno types output, you can find much more detail:
<details> <summary>(Folded for length)</summary>
/** Provides the API for creating and managing a WebSocket connection to a server, as well as for sending and receiving data on the connection. */
interface WebSocket extends EventTarget {
  /**
   * Returns a string that indicates how binary data from the WebSocket object is exposed to scripts:
   *
   * Can be set, to change how binary data is returned. The default is "blob".
   */
  binaryType: BinaryType;
  /**
   * Returns the number of bytes of application data (UTF-8 text and binary data) that have been queued using send() but not yet been transmitted to the network.
   *
   * If the WebSocket connection is closed, this attribute's value will only increase with each call to the send() method. (The number does not reset to zero once the connection closes.)
   */
  readonly bufferedAmount: number;
  /**
   * Returns the extensions selected by the server, if any.
   */
  readonly extensions: string;
  onclose: ((this: WebSocket, ev: CloseEvent) => any) | null;
  onerror: ((this: WebSocket, ev: Event | ErrorEvent) => any) | null;
  onmessage: ((this: WebSocket, ev: MessageEvent) => any) | null;
  onopen: ((this: WebSocket, ev: Event) => any) | null;
  /**
   * Returns the subprotocol selected by the server, if any. It can be used in conjunction with the array form of the constructor's second argument to perform subprotocol negotiation.
   */
  readonly protocol: string;
  /**
   * Returns the state of the WebSocket object's connection. It can have the values described below.
   */
  readonly readyState: number;
  /**
   * Returns the URL that was used to establish the WebSocket connection.
   */
  readonly url: string;
  /**
   * Closes the WebSocket connection, optionally using code as the the WebSocket connection close code and reason as the the WebSocket connection close reason.
   */
  close(code?: number, reason?: string): void;
  /**
   * Transmits data using the WebSocket connection. data can be a string, a Blob, an ArrayBuffer, or an ArrayBufferView.
   */
  send(data: string | ArrayBufferLike | Blob | ArrayBufferView): void;
  readonly CLOSED: number;
  readonly CLOSING: number;
  readonly CONNECTING: number;
  readonly OPEN: number;
  addEventListener<K extends keyof WebSocketEventMap>(type: K, listener: (this: WebSocket, ev: WebSocketEventMap[K]) => any, options?: boolean | AddEventListenerOptions): void;
  addEventListener(type: string, listener: EventListenerOrEventListenerObject, options?: boolean | AddEventListenerOptions): void;
  removeEventListener<K extends keyof WebSocketEventMap>(type: K, listener: (this: WebSocket, ev: WebSocketEventMap[K]) => any, options?: boolean | EventListenerOptions): void;
  removeEventListener(type: string, listener: EventListenerOrEventListenerObject, options?: boolean | EventListenerOptions): void;
}

declare var WebSocket: {
  prototype: WebSocket;
  new(url: string, protocols?: string | string[]): WebSocket;
  readonly CLOSED: number;
  readonly CLOSING: number;
  readonly CONNECTING: number;
  readonly OPEN: number;
};
</details>
The presence of declare makes the difference (export also seems to work). We can reproduce this locally:
$ cat example1.ts
interface Foo { x: number };
var Foo: { y: string };

$ deno doc example1.ts

$ cat example2.ts
interface Foo { x: number };
declare var Foo: { y: string };

$ deno doc example2.ts
Defined in file:///home/scott/Projects/dotfiles/scripts/docbug/example2.ts:2:8

var Foo: { y: string; }


$ cat example3.ts
declare interface Foo { x: number };
var Foo: { y: string };

$ deno doc example3.ts
Defined in file:///home/scott/Projects/dotfiles/scripts/docbug/example3.ts:1:0

interface Foo

  x: number


$ cat example4.ts
declare interface Foo { x: number };
declare var Foo: { y: string };

$ deno doc example4.ts
Defined in file:///home/scott/Projects/dotfiles/scripts/docbug/example4.ts:2:8

var Foo: { y: string; }

Defined in file:///home/scott/Projects/dotfiles/scripts/docbug/example4.ts:1:0

interface Foo

  x: number
The doc website has the same problem, as far as I can tell.
closed time in 16 days
solson
issue commentdenoland/deno
Some interfaces are hidden from `deno doc`
Yes, fixed by #7514.
comment created time in 16 days
pull request commentNixOS/nixpkgs
Ahh, that makes sense. I don't personally need that, I just misunderstood what state this PR was in.

comment created time in 17 days
pull request commentNixOS/nixpkgs
Deno has moved up to version 1.4.4.
comment created time in 17 days
push eventsolson/dotfiles
commit sha 0c6b07eb988eae936bb44cb876231b0ca356f56b
vim: Add vim-characterize.
push time in 18 days
issue commentdenoland/deno
Idle REPL uses CPU instead of actually idling
I figured out that line 450 here is waking up constantly, but I don't yet know why:
https://github.com/denoland/deno/blob/4c7f53b04bc631525a4512576fc0d7dca05dec09/cli/main.rs#L445-L452
comment created time in 18 days
issue commentdenoland/deno
REPL: inaccessible variables if not declared properly
Yeah, looks like we should close. I can also reproduce in the Chrome inspector:


comment created time in 18 days
issue openeddenoland/deno
Idle REPL uses CPU instead of actually idling
When I open the REPL on Deno master, the Deno process idles at around 12% CPU usage (and I can hear my fans spin up a bit), while Deno 1.4.2 actually idles at 0%.
Version info: https://github.com/denoland/deno/commit/e5348a6a38b3c06a916223ad0b99e8cfe47725b1 with cargo build --release
cc @caspervonb
created time in 18 days
issue commentdenoland/deno
REPL: inaccessible variables if not declared properly
After https://github.com/denoland/deno/pull/7784, we can now get around this with let a = ..., but a = ... still fails, in line with what @nayeemrmn said:
> let a = (() => { throw new Error(); })(); // The initializer throws.
Uncaught Error:
    at <anonymous>:2:24
    at <anonymous>:2:39
> a = "abc";
Uncaught ReferenceError: Cannot access 'a' before initialization
    at <anonymous>:2:3
> let a = "abc"
undefined
> a
"abc"
comment created time in 18 days
pull request commentNixOS/nixpkgs
wrapQtAppsHook: wrap binaries in all outputs
qdbusviewer is still broken today. Can we move towards merging this or figuring out the correct fix for qdbusviewer and any similarly broken apps?
For reference, qdbusviewer fails like this:
$ qdbusviewer
qt.qpa.plugin: Could not load the Qt platform plugin "xcb" in "" even though it was found.
This application failed to start because no Qt platform plugin could be initialized. Reinstalling the application may fix this problem.

Available platform plugins are: wayland-egl, wayland, wayland-xcomposite-egl, wayland-xcomposite-glx, eglfs, linuxfb, minimal, minimalegl, offscreen, vnc, xcb, wayland-org.kde.kwin.qpa.

Aborted (core dumped)

comment created time in 19 days
issue openeddenoland/deno
`--allow-read` allows writes to Unix sockets
Deno.connect({ transport: "unix", path: "/path/to/socket" }) only requires --allow-read=/path/to/socket, yet allows you to write to the socket. On typical Linux systems, that means deno run --unstable --allow-read foo.ts could connect to the DBus socket and potentially run arbitrary commands, depending on what services are running.
Note: transport: "unix" is only available with --unstable right now.
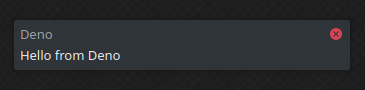
Here's a proof-of-concept script that should produce a little notification like this with deno run --unstable --allow-read dbus-notify.ts on a typical Linux system with systemd and a user ID of 1000.
created time in 19 days
push eventsolson/etc-nixos
commit sha f45a2b5bb28fb60d648ec0c221c20fc86638bfb8
Disable spammy firewall logging.
push time in 19 days
push eventsolson/etc-nixos
commit sha afd21591570b928ba0947c36d9aefc790b85b914
Serve .ts files as application/typescript.
push time in 19 days
startedtpope/vim-characterize
started time in 20 days
startedMartchus/syncthingtray
started time in 21 days
startedrfjakob/systembus-notify
started time in 21 days
startedrfjakob/earlyoom
started time in 21 days
issue closedmozilla/nixpkgs-mozilla
Combine efforts with rust-nightly-nix
I haven't looked into the details yet, but it's likely that we are dealing with the same problems. I made an issue over at https://github.com/solson/rust-nightly-nix/issues/21.
closed time in 22 days
solson
issue commentmozilla/nixpkgs-mozilla
Combine efforts with rust-nightly-nix
This issue is now out of date, see https://github.com/solson/rust-nightly-nix/issues/27 for a summary of the situation.
comment created time in 22 days
issue closedsolson/rust-nightly-nix
Looking for a new maintainer, otherwise abandoning
I have not used rust-nightly-nix for years now. The mozilla overlay worked better, from what I can remember, and I just use rustup now that the Nix package makes it do patchelf automatically.
In a couple weeks I'm going to archive this repo and close the open issues/PRs as stale, unless someone else wants to pick up maintainership (in which case I'd like to transfer the repo to your account).
cc @Ericson2314
closed time in 22 days
solson
issue commentsolson/rust-nightly-nix
Looking for a new maintainer, otherwise abandoning
Ok, archiving the repo now. If anyone has any further comments they can email me.
comment created time in 22 days
push eventsolson/nixpkgs
commit sha aba3abc79b233aa2d4836fc3a0e031aecdf5e715
dbus: build manpages from xml The `docbook_xml_dtd_44` and `docbook-xsl-nons` bits are necessary to prevent `xmlto` from trying to use the network during the build.
push time in 22 days
pull request commentNixOS/nixpkgs
I have squashed and rebased onto staging. I have no idea why GitHub did that mass review request.
comment created time in 22 days
push eventsolson/nixpkgs
commit sha c36cf877f17ce8cf547f921c3a65d9aad46c85bb
darwin.xcode: add hash for 11.3.1
commit sha 39c536c8db4e0982f89b67a194cd36ba9f4fbdd5
darwin.libtapi: update, fix installTargets
commit sha 3c6bd61560d042ce1e366989b92b615dfa1dffb3
darwin.cctools: 927.0.2 -> 949.0.1 Needed for iOS 13 support
commit sha bb5d0a47b738844d6e95768d995614062e22d119
systems/examples.nix: update to iOS 13 new apps need iOS 13, so we should try to use that here
commit sha 753e80125fd071f6d4cd3ea9988c3c4da86f6cba
darwin/xcode: default to 11.3.1
commit sha 95eabdfd5f6197c83e9e5f53ddb65dbbea3c13fd
xcode/sdk-pkgs.nix: set -platform_version in addition to -miphoneos-version-min The App Store looks at LC_VERSION_MIN_IPHONEOS to verify you have a new enough SDK version. This is not just the minimum version, but also the sdk version used. When the linker can’t figure it out, it tries to infer it from the sdk path[1]. When no sdk version is found, it defaults to just using the -miphoneos-version-min value[2]. So, to make sure we don’t rely on inference (which doesn’t work in the current directory structure), we have to specify -platform_version. [1]: https://github.com/tpoechtrager/cctools-port/blob/43f32a4c61b5ba7fde011e816136c550b1b3146f/cctools/ld64/src/ld/Options.cpp#L5355-L5376 [2]: https://github.com/tpoechtrager/cctools-port/blob/43f32a4c61b5ba7fde011e816136c550b1b3146f/cctools/ld64/src/ld/ld.hpp#L58
commit sha b418d4c6a4a3b34e317327ff7e80ab7a8fc1c02a
libtapi: fix build, install phase and install name installTarget looks like a typo for installTargets. This causes a lot of llvm and clang to be built and installed. Clang is not intended to be an external dependency. The source bundle includes llvm and clang. Adding include paths and building clangBasic first is sufficient to use the internal clang components.
commit sha 630f5d30df4256991b2e72658eedeb954f7559f6
stdenv/darwin: enable tapi support in cctools
commit sha b935375becd5334720cf375d7a5773f4e343ea8e
gts: Fix cross compilation gts generate binaries during the build process that are used during the build process. When building cross-platform, these binaries are not executable as they are built with for the target platform instead of the host platform. The boostrap build introduced here will first build gts natively and then cross-platform, using the native binaries in the cross-build.
commit sha b1700a73361284c6c0132e6caf5e0345223f3010
stdenv: unset SDKROOT on Darwin The Rust `cc` crate started running `xcrun` when SDKROOT is defined: https://github.com/alexcrichton/cc-rs/commit/a970b0ab0beecec1d9c589d2e6aa5f3ad1bd3f9b Consequently, building crates that use newer versions of the `cc` crate fail, because xcrun is not available in pure build environments.
commit sha 43eae86de2f0f08cac4cc8c8f0e73f928bf97ad4
libfido2: 1.4.0 -> 1.5.0
commit sha 8e4e38cdcdc5f2be6875e6506d0789e9e5411ea6
octave: Fix libtool framework link failure on Darwin This fix moves linker flags of the form `-framework foo` from dependency_libs to inherited_linker_flags, since libtool doesn't understand them. See #96977 for details. Fixes #96977
commit sha 749a260edd4b29c446a02b8bee5cdb44a3bf4a95
bmake: 20200710 -> 20200902
commit sha f03235e5289d2217544bd1a70c2a27433800b6d7
cimg: 2.9.1 -> 2.9.2
commit sha 6805511b625b6eb0900c9c2670280267b1aad4d6
Merge pull request #96979 from graham33/fix/96977_octave_libtool octave: Fix libtool framework link failure on Darwin
commit sha 18a8a9ff6acaa0cbb041e7063be6af45633b1e60
Merge pull request #97366 from r-ryantm/auto-update/bmake bmake: 20200710 -> 20200902
commit sha 9b7cf1aa42e1ad0892e2894c41562752050c0366
Merge pull request #97367 from r-ryantm/auto-update/cimg cimg: 2.9.1 -> 2.9.2
commit sha 90c5f2f9537cde699424943e2b63036ca50a479e
libuv: 1.38.1 -> 1.39.0
commit sha 204eb76c7eadc2dc90ecdbf24b7d2b30391d6340
nodejs-14_x: 14.9.0 -> 14.10.0 https://github.com/nodejs/node/releases/tag/v14.10.0
commit sha 682465a45ad7bc91336ca60418796f4fce922b44
perlPackages: make it easier for the parser
push time in 22 days
Pull request review commentNixOS/nixpkgs
stdenv.mkDerivation rec { --replace 'DBUS_DAEMONDIR"/dbus-daemon"' '"/run/current-system/sw/bin/dbus-daemon"' ''; - outputs = [ "out" "dev" "lib" "doc" ];+ preConfigure = ''+ for file in doc/*.xml doc/*.xml.in; do+ substituteInPlace "$file" --replace "http://www.oasis-open.org/docbook/xml/4.4/docbookx.dtd" \+ "${docbook_xml_dtd_44}/xml/dtd/docbook/docbookx.dtd"+ done+ '';++ preBuild = ''+ makeFlagsArray+=XMLTO="${xmlto}/bin/xmlto -x ${docbook_xsl}/xml/xsl/docbook/manpages/docbook.xsl"
Done, thanks! I wasn't sure how to deal with this and that is much cleaner.
comment created time in 22 days
push eventsolson/nixpkgs
commit sha 4f535156765077f636a31b3994ccff84f5958ec3
dbus: provide XML DTD/XSL more cleanly
push time in 22 days
PR opened NixOS/nixpkgs
Motivation for this change
I noticed that manual pages like dbus-send(1) and dbus-monitor(1) were missing from my system.
The docbook_xml_dtd_44 and docbook_xsl bits are necessary to prevent
xmlto from trying to use the network during build. I copied from other
nix packages that have the same issue.
Things done
- [ ] Tested using sandboxing (nix.useSandbox on NixOS, or option
sandboxinnix.confon non-NixOS linux) - Built on platform(s)
- [x] NixOS
- [ ] macOS
- [ ] other Linux distributions
- [ ] Tested via one or more NixOS test(s) if existing and applicable for the change (look inside nixos/tests)
- [ ] Tested compilation of all pkgs that depend on this change using
nix-shell -p nixpkgs-review --run "nixpkgs-review wip" - [ ] Tested execution of all binary files (usually in
./result/bin/) - [ ] Determined the impact on package closure size (by running
nix path-info -Sbefore and after) - [ ] Ensured that relevant documentation is up to date
- [x] Fits CONTRIBUTING.md.
I don't think my machine is powerful enough to run the nixpkgs-review for this change, given the sheer number of packages that depend on dbus. I confirmed the manpages were generated correctly and that simple binaries like dbus-send, dbus-monitor, and dbus-uuidgen work (I'm not sure how to use or test the others).
pr created time in 22 days
push eventsolson/dotfiles
commit sha 6fc63388d895f04c9ab0b038a2f9760d84068513
fish: Add aliases for getting nixpkgs sources easily.
commit sha 5e786e01ed72f148c45e7c75a2a8e2f4f9856ae3
vim: Add vim-xquery-syntax.
push time in 22 days
pull request commentdenoland/deno
fix(cli): Use safe shell escaping in `deno install`
I added a simple test for something which currently generates a syntactically invalid shell script:
$ deno install foo.ts '"'

$ /home/scott/.deno/bin/foo
/home/scott/.deno/bin/foo: line 3: unexpected EOF while looking for matching `"'
/home/scott/.deno/bin/foo: line 4: syntax error: unexpected end of file

$ cat /home/scott/.deno/bin/foo
#!/bin/sh
# generated by deno install
deno "run" "file:///home/scott/foo.ts" """ "$@"
On another note, the Windows tests are going to be broken — I just noticed that the existing tests assume the Windows batch scripts and the non-Windows shell scripts will contain the same syntax, which shouldn't generally be true. How would you prefer to deal with this? We could use platform-specific if cfg!(windows) assertions.
comment created time in a month
push eventsolson/deno
commit sha 19bf16933363a95e78d25771170bf12b50cd4648
test(cli): Add `deno install` shell escaping test
push time in a month
PR opened denoland/deno
I was hesitant to add a new dependency, but shell escaping is one of those things you really don't want to get wrong. The shell-escape crate is used by cargo itself.
I did not handle Windows, if any similar issue exists there, since I cannot easily test it.
This also adds exec so the parent shell process doesn't stick around — I think this should close https://github.com/denoland/deno/issues/3961.
pr created time in a month
push eventsolson/deno
commit sha aaa5e6613a739f8e2ff7579b69c2504bcdc37d4f
fix(cli/rt): make some web API constructors illegal at runtime (#7468)
commit sha b657d743a22802b8232fbf558f2f00bf2942096f
refactor: remove CliState, use OpState, add CliModuleLoader (#7588) - remove "CliState.workers" and "CliState.next_worker_id", instead store them on "OpState" using type aliases. - remove "CliState.global_timer" and "CliState.start_time", instead store them on "OpState" using type aliases. - remove "CliState.is_internal", instead pass it to Worker::new - move "CliState::permissions" to "OpState" - move "CliState::main_module" to "OpState" - move "CliState::global_state" to "OpState" - move "CliState::check_unstable()" to "GlobalState" - change "cli_state()" to "global_state()" - change "deno_core::ModuleLoader" trait to pass "OpState" to callbacks - rename "CliState" to "CliModuleLoader"
commit sha 51019dc2674de9b4f5c3beb09c193b98fd582d25
fix(cli/flags): Make --unstable a global flag (#7585)
commit sha db5004f2003486aa78751a5dd5bf2989824e724e
fix(fmt,lint): do not print number of checked files when `--quiet` is enabled (#7579)
commit sha 0a9d7e4e397a688dbd5d9448cdcbb119182ed446
fix(cli/installer): Don't reload by default (#7596)
commit sha d1b88510cf31e1a9e5218f3195d15390e904f38a
refactor: remove GlobalState::compile_lock (#7598)
commit sha 333462b9c2ca662a9a26c9de6eeddbd545428a18
docs: titles in examples should be sentence case (#7609)
commit sha dc6571909ba446fc732b2c6a48742eb4b9614513
fix: make --watch and --inspect conflicting args (#7610)
commit sha c4ed3fb7e767311dc5a6fc931fceaf4fdee885de
chore: add copyright (#7593)
commit sha e06875e9f7e4b3365b9f30322e3e5307903feed4
refactor(cli/coverage): await for inspector message response (#7584)
commit sha 42772845f6dde1b27a9e55c7738743388350f2b2
fix(info): add --importmap flag (#7424)
commit sha 9d738fc1977e0bd3d36f361198a1101e17c3b3b3
test(std/wasi): add fd_renumber test (#7574)
commit sha d88d26a0486c2b2d2cb34d65fd1b5521960002c5
fix(cli): Use safe shell escaping in `deno install`.
commit sha f982200e7a503acf18939492a6d678d6735921c9
fix(cli): Use `exec` in `deno install` scripts. Fixes #3961
push time in a month
push eventsolson/deno
commit sha 6ac50f67b62b2788e8bb4d3ea99b243270f1b8bf
fix(cli): Use safe shell escaping in `deno install`.
commit sha 925acd264a966ee550dd0cbcdd282b81d8170d75
fix(cli): Use `exec` in `deno install` scripts. Fixes #3961
push time in a month
push eventsolson/deno
commit sha 963a4babfdd56a2372d4474963bbdfa1541ab517
fix(cli): Use safe shell escaping in `deno install`.
commit sha 5d89e214d65609210e182be8e9b3264ab480a622
fix(cli): Use `exec` in `deno install` scripts. Fixes #3961
push time in a month
PR closed denoland/deno
This is a work-in-progress implementation of #7425. It supports the examples in that issue exactly as written.
The general idea is deno repl -i a=url,b=url -i c=url gives you a list of pairs [("a", "url"), ("b", "url"), ("c", "url")] that the REPL implementation will resolve before starting up. Both comma-separation and flag repetition are built-in clap features. The --allow-read (and similar) flags accept only the comma-separated form, but I think it's convenient to allow multiple flags here, so if someone has an alias foo to deno repl -i foo=url they can easily run foo -i bar=url to add an additional import.
TODO:
- [ ] Open questions: See #7425 - the Permissions section is especially important.
- [ ] Documentation: Should this be added to the manual and/or release notes, not just the CLI help?
- [ ] Tests: Do we have support for tests of interactive things like the REPL?
Regarding cargo test, I currently can't run every test because some of them download and run a deno binary from the internet, which doesn't work on NixOS without a patchelf step.
Regarding the implementation, I wanted some advice:
- Should I use a more semantic type than
Vec<(String, String)>for theimportsfield? - Should I hide the imports feature behind
--unstable? - Should we use
globalThis? I looked into the possibility of injectinglet/const/import-like local bindings with V8, but it currently seems quite difficult. @nayeemrmn suggestedglobalThiswould be okay. - I'm not sure if
file://${cwd}/is the right approach to the URL base, but it seems to make bothhttps://URLs and local file paths (both absolute and relative) work perfectly, so you can do things likedeno repl -i local=./local.tsinstead ofdeno repl -i "local=file://$(pwd)/local.ts".
pr closed time in a month
pull request commentdenoland/deno
feat(cli): add a REPL option for module imports
Closing in favour of a different approach — discussion of the feature should be had over on the issue, anyway.
comment created time in a month
push eventsolson/dotfiles
commit sha d7a08c7b187bcb5a1b5df6bba6d68521f8d9fb98
vim: Remove unused config.
push time in a month
startedjunegunn/vim-plug
started time in a month
push eventsolson/dotfiles
commit sha 55146733d35b5f65dfa9b59e7233d5564a4292f1
vim: Make config Neovim-only.
commit sha acc788ce285f226261b194087d94d01cae149987
vim: Enable undofile.
push time in a month
push eventsolson/dotfiles
commit sha b531dcb79c1903e7bff486259906ba5cc3c3651a
scripts: Add basic terminal colors test script.
push time in a month
push eventsolson/dotfiles
commit sha 5242611a410084954568c5554709bfee4163477a
install: Simplify by symlinking whole directories.
commit sha 387dbbdde57487ab8a7c1c80ceacdc62d55f9d3f
Consolidate .gitignores.
commit sha 1a23aabf52bd8d7fa973cc49d4da863c760b0c9a
fish: Work around bug with aliases and completion. Because aliases use `function --wraps` and the wrapped commands are `env` around the same name as the alias, Fish enters an infinite loop on autocompletion.
commit sha fd9e1d6a12fdd5a96d0fda4c7e87632fd0c8acd2
fish: Use a faster check for Nix shells.
commit sha 1616d1f4f32c90463354976300939951393ba51f
fish: Remove old commented code.
commit sha f022a3701fc19ddf5d31abf14576e7e0d8a04f04
fish: Pull in additional files from config dir.
commit sha f6b9416bbd66585e33b5ab3d372348a45ce9628e
vim: Define Coc extensions declaratively.
commit sha 43eb4ef291f2139527f0f7d07ead8dff0cf9cfa0
vim: Open vimrc without split view.
push time in a month
startedkeepassxreboot/keepassxc
started time in a month
issue commentdenoland/deno
feature proposal: Deno builtin function & ops to create an anonymous pipe.
I think this would solve the problem in https://github.com/denoland/deno/issues/2494 — using OS-level pipes between the child processes (with no copying through the parent Deno process) would work exactly like shell piping, and when the writing process quits and closes its stdout, the reading process will detect this on its stdin the usual way.

comment created time in a month
issue commentdenoland/deno
That's a good point, I didn't quite think it through. I just confirmed that deno run https://... (or deno cache or deno install) with a script that imports from http://... is blocked, so I agree. I think this issue could potentially be closed.

comment created time in a month
pull request commentdenoland/deno
feat(cli): add a REPL option for module imports
@bartlomieju Even when we have top-level await, I would still argue for including something like this flag. See the referenced issue for an explanation of my usecase that would go unmet ("Example 2" is the quickest thing to look at).
comment created time in a month
issue commentdenoland/deno
More granular priveldge separation
Maybe we should close this in favour of https://github.com/denoland/deno/issues/2620? It would be good to make sure all the discussion ends up in one place.
comment created time in a month
issue commentdenoland/deno
Potential security issues with shebang script with flags
I'm going through inactive issues doing some triage — it looks like this issue can be closed?

comment created time in a month