








EC2 tasks for Fabric
garethr/ansible-provisioner 77
A Digital Ocean specific provisioning and orchestration tool built around Ansible
garethr/appengine-image-host 45
Simple image resizing and hosting application
A simple web interface for running scripts and recording the results
Example of providing an Instant Messaging interface to App Engine application
Get capistrano hosts from puppet
garethr/bolt 17
A script runner
Super simple issue tracker for Google AppEngine, the code behind GitBug
site monitoring utility hosted on Google App Engine
Simple Queue for App Engine
push eventgarethr/pulumi-okteto-conftest-demo
commit sha 2caff8d14b41f442af45a23ff4bacb473d7e64e6
Try and fail the policy
push time in 4 days
push eventgarethr/pulumi-okteto-conftest-demo
commit sha b8d52ff73f3abcc3d8fe12b7655f80dae7c60e04
Try the documented release branch
push time in 4 days
push eventgarethr/pulumi-okteto-conftest-demo
commit sha d50ece503e9f51d01c571b9c3d9ff3ec8f3058c0
Try with the install CLI action instead
push time in 4 days
push eventgarethr/pulumi-okteto-conftest-demo
commit sha f1c9a758aa31c3200625df2929960cf834d5281a
Try with the CI ENV set
push time in 4 days
push eventgarethr/pulumi-okteto-conftest-demo
commit sha fdd26cc4e48a1b083f41892911ba33690b20c24a
Try without a virtuaneenv in the middle
push time in 4 days
push eventgarethr/pulumi-okteto-conftest-demo
commit sha 8b34446cdc36400085ffd1ac02c955551d40b24d
Try and install thee Kuberneetes plugin explicitly
push time in 4 days
push eventgarethr/pulumi-okteto-conftest-demo
commit sha 000599078e2b9d5dc9b5d63b4c9314ca5e5086f7
Install OPA plugin
push time in 4 days
push eventgarethr/pulumi-okteto-conftest-demo
commit sha 1cddd26c6f590175f0e9dd67e9732db66cd5a5f8
Install OPA plugin
push time in 4 days
push eventgarethr/pulumi-okteto-conftest-demo
commit sha 1b49cd198d8cab4006739fc7cf40b4b37f922600
Have workflow run on push to default branch
push time in 5 days
PR opened garethr/pulumi-okteto-conftest-demo
pr created time in 5 days
create barnchgarethr/pulumi-okteto-conftest-demo
created branch time in 5 days
push eventgarethr/pulumi-okteto-conftest-demo
commit sha a953b763882dfad12c56a0d8cc54987639b729e7
Still causing a clash, with pulumi not finding the venv
push time in 5 days
push eventgarethr/pulumi-okteto-conftest-demo
commit sha 3e7b82591db665745680f27f438a90da5cd8ca30
ENV may be affecting pulumi run, try and isolate
push time in 5 days
issue openedpulumi/pulumi-kubernetes
Output to YAML AND deploy using same Pulumi code
Problem description
<!--Briefly describe the issue that you've found. For general questions, join us on https://pulumi-community.slack.com/. -->
Following https://github.com/pulumi/pulumi-kubernetes/issues/1025 I was able to get render_yaml_to_directory to output YAML files from my Python code. However, I noticed (as documented) that this means I can’t then deploy those resources to the cluster with Pulumi as well. I'm looking though to do both:
- run pulumi up
- deploy to cluster
- generate YAML
I tried:
- Passing providers and a list of providers, but that didn’t seemed to revert to defaults :x:
- Using a config as a toggle between two providers, but this led to state problems :x:
- Abstracting the resources, and then applying twice in the same script, but Pulumi complains about them having the same name :x:
Appreciate this has a nice BETA FEATURE warning. I’d be interested if anyone has a pattern for doing the above, or if this might be supported in thee future.
:param pulumi.Input[str] render_yaml_to_directory: BETA FEATURE - If present, render resource manifests to this directory. In this mode, resources will not be created on a Kubernetes cluster, but the rendered manifests will be kept in sync with changes to the Pulumi program. This feature is in developer preview, and is disabled by default. Note that some computed Outputs such as status fields will not be populated since the resources are not created on a Kubernetes cluster. These Output values will remain undefined, and may result in an error if they are referenced by other resources. Also note that any secret values used in these resources will be rendered in plaintext to the resulting YAML.
Conversation in https://pulumi-community.slack.com/archives/CRFURDVQB/p1600518879011300
Affected product version(s)
- Pulumi
v2.10.1 - macOS
10.15.6 - Python
3.8.3
<!-- If the issue is specific to a Pulumi product version, let us know which version(s). -->
<!-- To improve this template, edit the .github/ISSUE_TEMPLATE.md file -->
created time in 5 days
push eventgarethr/pulumi-okteto-conftest-demo
commit sha f8e02c77c80c3c011474dacc138d7bfbb38d92d8
Add unit tests to workflow
push time in 5 days
push eventgarethr/pulumi-okteto-conftest-demo
commit sha 2ac16313eaa94de1ffbf76f4532c85f07b060afc
Explicitly specify the namespace
push time in 5 days
push eventgarethr/pulumi-okteto-conftest-demo
commit sha a3763b04a3d692f12ba7ad6e5fd6c96b9b02df7f
Added stack name
push time in 5 days
push eventgarethr/pulumi-okteto-conftest-demo
commit sha 3b3c6f23a9842191925c87a448331c716e24c002
Added a review workflow for changes
commit sha 600805e0112c3a3f65068ec38aef40276a94715a
Set Action to delpoy changes
push time in 5 days
push eventgarethr/pulumi-okteto-conftest-demo
commit sha f9df2339f55af2b881dadfbf8c5c30fae3b8ad39
Added a review workflow for changes
push time in 5 days
push eventgarethr/pulumi-okteto-conftest-demo
commit sha f4b1afadb3d8e7e8ea26241b5c253069ab386a4d
Test login to Okteto using the Actions
push time in 5 days
push eventgarethr/pulumi-okteto-conftest-demo
commit sha e7a4e142ddb0467a962da59fbf20538ca69e6b0b
Test login to Okteto using the Actions
push time in 5 days
push eventgarethr/pulumi-okteto-conftest-demo
commit sha d129a23db589b5b10923c6b7dc70290e9cebc10a
Added basic Kubernetes Pulumi example with a simple deployment
commit sha c4bb5a93850d4d711744c3d289423ed5dc616384
Added unit test example
commit sha d5e4f5dcd7e7314bf9b9dee525d60ac1ae283647
Added basic open policy agent policy for Kubernetes
commit sha d9021a2e1269a47ad78517e4e70a06b88e72869c
Test login to Okteto using the Actions
push time in 5 days
push eventgarethr/pysnyk
commit sha 322ec96ed8095b568fa8de3829d6bdbca34346a3
Added new container image attributes added recently to the API
push time in 7 days
PR merged snyk/actions
Annotated GitHub Actions example for IaC

pr closed time in 7 days
push eventsnyk/actions
commit sha 3f21934ba6d8b01dbf8dd905928f7dd2d8fab057
Annotated example for IaC
commit sha f1527148197a1251f9a29721b10fb8b2f92b2474
incorporated pr feedback
commit sha 401bcb72fe5d55d1b08454bdfea25e6d769ba057
fixed incomplete sentence
commit sha 9b5161e53634ad82054c8fc7f53ded303e7eed2e
Merge pull request #28 from snyk/feat/iac-github-action-example Annotated example for IaC
push time in 7 days
Pull request review commentsnyk/actions
+# A sample workflow which checks out your Infrastructure-as-Code Configuration files,+# such as Kubernetes, Helm & Terraform and scans them for any security issues.+# The results are then uploaded to GitHub Security Code Scanning+#+# For more examples, including how to limit scans to only high-severity+# issues, monitor images for newly disclosed vulnerabilities in Snyk and+# fail PR checks for new vulnerabilities, see https://github.com/snyk/actions/++name: Snyk Infrastructure as Code+on: push+jobs:+ snyk:+ runs-on: ubuntu-latest+ steps:+ - uses: actions/checkout@v2+ - name: Run Snyk to check configuration files for security issues+ # Snyk can be used to break the build when it detects security issues.+ # In this case we want to upload the issues to GitHub Code Scanning+ continue-on-error: true+ uses: snyk/actions/iac@master+ env:+ # In order to use the Snyk Action you will need to have a Snyk API token.+ # More details in https://github.com/snyk/actions#getting-your-snyk-token+ # or you can signup for free at https://snyk.io/login+ SNYK_TOKEN: ${{ secrets.SNYK_TOKEN }}+ with:+ # Add the path to the configuration file that you would like to test.
Worth explicitly specifying a Terraform file here as well I think, assuming we feel this will land in the next ~week. We might not be able to update them quickly after launch.
comment created time in 7 days
Pull request review commentsnyk/actions
+# A sample workflow which checks out your Infrastructure-as-Code Configuration files,+# such as Kubernetes, Helm & Terraform and scans them for any security issues.+# The results are then uploaded to GitHub Security Code Scanning+#+# For more examples, including how to limit scans to only high-severity+# issues, monitor images for newly disclosed vulnerabilities in Snyk and+# fail PR checks for new vulnerabilities, see https://github.com/snyk/actions/
Do we want to say vulnerabilities or stick with misconfigurations for IaC?
comment created time in 7 days
Pull request review commentsnyk/actions
+# A sample workflow which checks out your Infrastructure-as-Code Configuration files,+# such as Kubernetes, Helm & Terraform and scans them for any security issues.+# The results are then uploaded to GitHub Security Code Scanning+#+# For more examples, including how to limit scans to only high-severity+# issues, monitor images for newly disclosed vulnerabilities in Snyk and
images here should be something else. And monitor isn't applicable to snyk iac
comment created time in 7 days
Pull request review commentsnyk/actions
+# A sample workflow which checks out your Infrastructure-as-Code Configuration files,
Infrastructure-as-Code shouldn't be hyphenated I don't think. I don't think we do so elsewhere and common usage isn't to do so.
comment created time in 7 days
push eventsnyk/actions
commit sha 9f7e5614982cd96c3cf158a29e98dab2a65765f0
Added an annotated example for the docker action
commit sha c75628d834bd4a804426e1cb7b31a9aa43a54c31
Make outputting the SARIF file the default behaviour
push time in 7 days
pull request commentsnyk-labs/pysnyk
Added new container image attributes added recently to the API
@nirfuchs quick addition of a few container fields for a potential SnykCon demo when you have a moment.

comment created time in 7 days
push eventsnyk/actions
commit sha 29c7b1cfabcc7a93a966fd38b9781281c32a0ded
Use the smaller alpine image for IaC
push time in 8 days
push eventsnyk/actions
commit sha 6e2dae6a1271c9c58c5e924e0f6d5fd03acd39ef
Enable triggering a SARIF file with the Infrastructure as Code Action
push time in 9 days
push eventsnyk/snyk-images
commit sha d65f77f081800ef6ccf1d0e77a894e443b8fe067
Output SARIF if INPUT_FILE set, for IaC Action
push time in 9 days
push eventsnyk/snyk-images
commit sha a0740cd2772ca1455134f868f9cd5bb858bb1c2d
Use sh not bash for flag detection
push time in 9 days
push eventgarethr/snykus
commit sha 6cd876ad66d0ddfa816e06ecbe950ab83a641f6a
Try to generate a SARIF file on the default build
push time in 9 days
push eventsnyk/actions
commit sha 4b978fd1781371183aadeb63803accd61ba3dfef
Enable the docker action to enable SARIF output
push time in 9 days
push eventsnyk/snyk-images
commit sha 194393e90631fc411833498c873be93c2ba38c69
Automatically output a SARIF file if an ENV and file is set
push time in 9 days
push eventgarethr/snykt
commit sha 3133236bc8c3b925276d9447316fa5b203b93e93
Added a Snykout target
commit sha e1eb7538e9678c0174c377c520ee6a98c04a6c7d
Add Conftest example
commit sha e6f1191fd72e63e7be8ffedc0e753429c80c2ea8
Added policies for catching disallowed base images
push time in 10 days
push eventsnyk/snyk
commit sha 565df40fa25fa14e4422583e9145b733915bb5aa
feat: Add platform details to help for snyk container The snyk container CLI now supports passing an explicit platform value. This will then test the image with that platform, rather than just the default (probably amd64).
commit sha 5bf1e3eb50bd9f3aaf26329759e345b518761423
Merge pull request #1411 from snyk/feat/add-platform-details-to-help feat: Add platform details to help for snyk container
push time in 10 days
PR merged snyk/snyk


The snyk container CLI now supports passing an explicit platform value. This will then test the image with that platform, rather than just the default (probably amd64).
- [x] Ready for review
- [x] Follows CONTRIBUTING rules
- [x] Reviewed by Snyk internal team
What does this PR do?
Adds details about --platform to the help text.
How should this be manually tested?
snyk container --help
What are the relevant tickets?
See https://github.com/snyk/snyk/pull/1389
pr closed time in 10 days
issue commentsnyk/actions
Python Action can't find Pip dependencies
I think this is probably private dependencies. The best bet is the setup action, which should be faster and get you the latest version of Snyk installed with a single line.
 snyk:
    runs-on: ubuntu-latest
    steps:
    - uses: actions/checkout@v2
    - name: Set up Python
      uses: actions/setup-python@main
      with:
        python-version: '3.x'
    - name: Install dependencies
      run: |
        python -m pip install --upgrade pip wheel
        pip install -r requirements.txt
    - uses: snyk/actions/setup@master
    - name: Run Snyk to check for vulnerabilities
      continue-on-error: true
      env:
        SNYK_TOKEN: ${{ secrets.SNYK_TOKEN }}
      run: |
        snyk monitor --org=${{ secrets.SNYK_ORG }}

comment created time in 10 days
PR opened snyk/snyk
The snyk container CLI now supports passing an explicit platform value. This will then test the image with that platform, rather than just the default (probably amd64).
- [x] Ready for review
- [x] Follows CONTRIBUTING rules
- [ ] Reviewed by Snyk internal team
What does this PR do?
Adds details about --platform to the help text.
How should this be manually tested?
snyk container --help
What are the relevant tickets?
See https://github.com/snyk/snyk/pull/1389
pr created time in 10 days
push eventsnyk/snyk
commit sha 565df40fa25fa14e4422583e9145b733915bb5aa
feat: Add platform details to help for snyk container The snyk container CLI now supports passing an explicit platform value. This will then test the image with that platform, rather than just the default (probably amd64).
push time in 10 days
push eventinstrumenta/scoop-instrumenta
commit sha 8eefd63156435223492e9dacfc2c585ce4d5826e
Scoop update for conftest version v0.21.0
push time in 12 days
push eventinstrumenta/homebrew-instrumenta
commit sha e697e9e53eeff399c68b854bc319023fbe47a767
Brew formula update for conftest version v0.21.0
push time in 12 days
push eventopen-policy-agent/conftest
commit sha 46ec24604d36a34cb6c6f3b338cbc89df3b1f585
fixed gitlab-ci example Signed-off-by: HaveFun83 <[email protected]>
commit sha f74e0eaef3b19456e2f5b5ebafab027a0fd807f8
Merge pull request #382 from HaveFun83/gitlab-ci-fix fixed gitlab-ci example
push time in 12 days
PR merged open-policy-agent/conftest
Hi this PR fix a typo in the gitlab-ci example.
cheers

pr closed time in 12 days
created tagopen-policy-agent/conftest
Write tests against structured configuration data using the Open Policy Agent Rego query language
created time in 12 days
push eventsnyk/actions
commit sha be5ddb455d96749687433d06af4b2324f5fa9984
Missed bullet for list of actions
push time in 12 days
issue commentdeislabs/oras
As a consumer of Oras in Conftest, I think either model works in the short term, though the plugin model maybe works slightly better in the long term. If the plugin model is chosen having a discovery mechanism would be important. Given the small number of likely plugins a page in the documentation or a list in the repository would suffice.

comment created time in 12 days
push eventsnyk/actions
commit sha 7a35abcc9286579a1a6409c7d05f18a62dcffbb4
Apply the documentation changes to the README template
push time in 12 days
issue closedsnyk/actions
Resiliency request: Retry on "internal server error"
We have encountered an error that suggests the snyk action can encounter network problems when talking to snyk's servers:
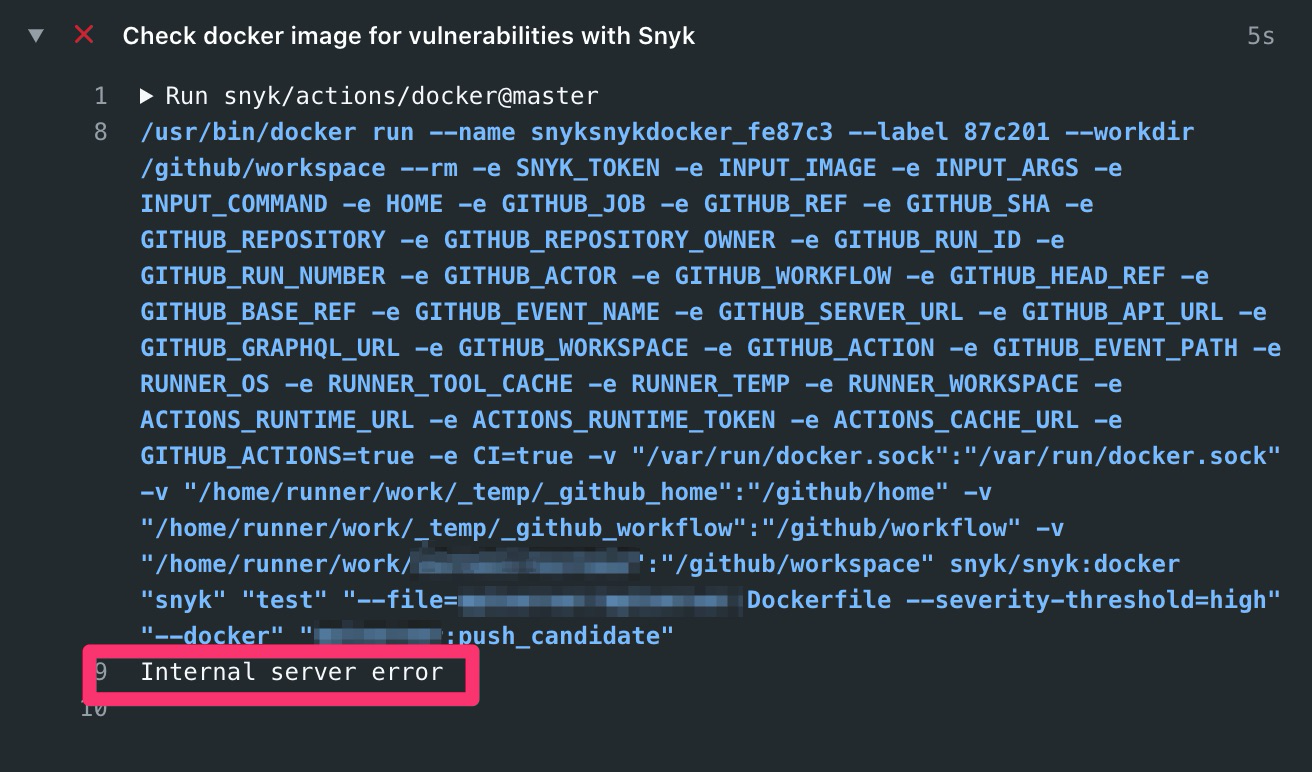
Normally in the case of a workflow that was merely verifying a PR's contents before merge, we'd just retry the build. In the case of the above build, however, this is a workflow that runs after a PR is merged and verifies the team's integration branch, so there's not an opportunity to re-run the workflow before this sets off a cascade of notifications to various parties.
In cases like these, if snyk encounters an error that can be identified as a brief problem with snyk's servers and not the scan per se, would it be reasonable to have a retry (with exponential backoff) feature?
closed time in 12 days
Maciek416
issue commentsnyk/actions
Resiliency request: Retry on "internal server error"
Thanks for the suggestion, and sorry for taking a while to get back to this. The Snyk Actions act as a minimal wrapper around the CLI, so I think functionality like this would belong there. This certainly feels useful for other integrations as well. Could I ask if you could open on https://github.com/snyk/snyk/issues if this is still an issue.
comment created time in 12 days
issue closedsnyk/actions
Hello I'm trying to run the snyk node action but throws an internal error
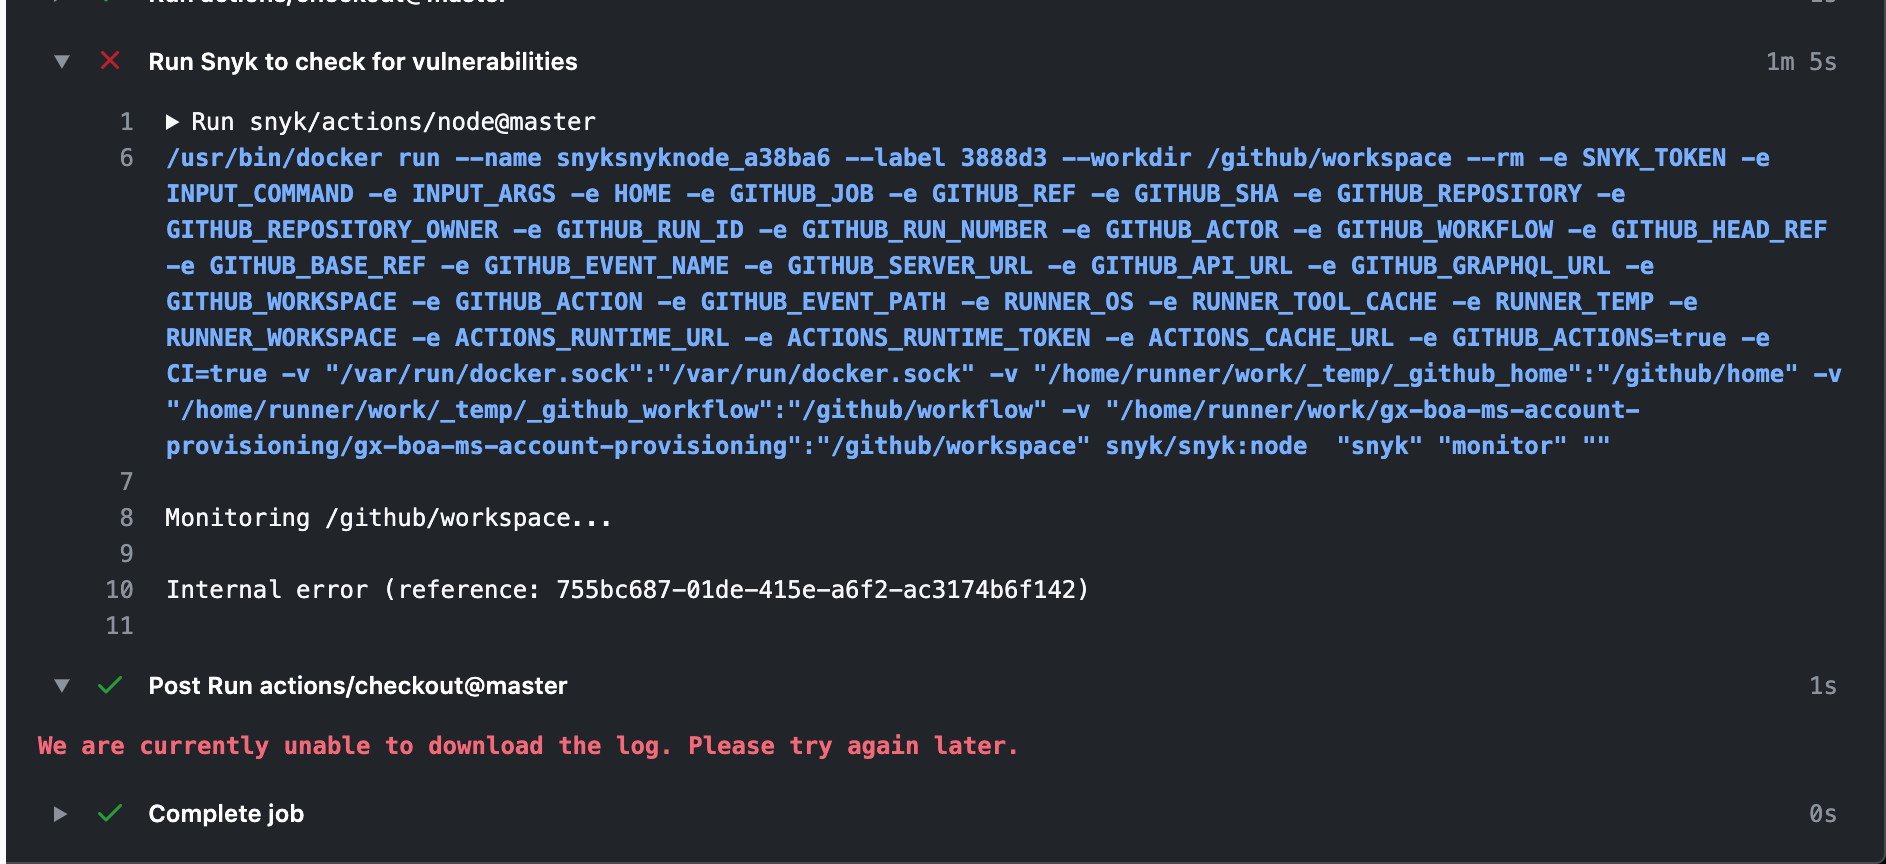
This is my .yml file
name: Code vulnerabilities with synk
on:
  pull_request:
    branches:
      - master
      - develop

jobs:
  security:
    runs-on: ubuntu-latest
    steps:
      - uses: actions/checkout@master
      - name: Run Snyk to check for vulnerabilities
        uses: snyk/actions/node@master
        env:
          SNYK_TOKEN: ${{ secrets.SNYK_TOKEN }}
        with:
          command: monitor
closed time in 12 days
Gmora08
issue commentsnyk/actions
Sorry for not getting back to close this out. Glad everything is working now.
comment created time in 12 days
issue closedsnyk/actions
Docker: action does not honor a snyk ignore'd vulnerabilty
When I generate an ignore rule with snyk ignore, the resulting .snyk file doesn't seem to be honored by the github action (or snyk test). That is to say, the action fails because the scan fails.
I've made a test case for this (the result is the same for the CLI):
https://github.com/Maciek416/snyk-test-case/blob/master/Dockerfile https://github.com/Maciek416/snyk-test-case/blob/master/.snyk
I invoke the action with the following yaml:
      - name: Check docker image for vulnerabilities with Snyk
        uses: snyk/actions/docker@master
        env:
          SNYK_TOKEN: ${{ secrets.SNYK_TOKEN }}
        with:
          image: apiserver:push_candidate
          args: --file=apiserver/apiserver.Dockerfile --exclude-base-image-vulns
I've tried locating the .snyk file both in the root of my repository and in the apiserver/ directory mentioned by the --file argument above. In both cases, the vulnerability SNYK-ALPINE38-PROCPS-309362 is flagged and fails the scan.
Does the action (or perhaps CLI) not support applying ignore rules to docker yet?
closed time in 12 days
Maciek416
issue commentsnyk/actions
Docker: action does not honor a snyk ignore'd vulnerabilty
I'll close this issue as it appears to be resolved. If you're still seeing the issue please do open with further information.
comment created time in 12 days
issue closedsnyk/actions
Python Action can't find Pip dependencies
I am attempting to run the Snyk Python action but am having issues with it resolving the dependencies I install. We are using self-hosted runners, but we are also limited in running only our own organization actions, so we have a process to mirror 3rd party repositories locally. Here's what I have for a workflow:
...
      - name: Checkout
        uses: <ourorg>/checkout@master
      - name: setup python
        uses: <ourorg>/setup-python@v2
      - uses: <ourorg>/cache@v2
        with:
          path: ~/.cache/pip
          key: ${{ runner.os }}-pip-${{ hashFiles('**/requirements.txt') }}
          restore-keys: |
            ${{ runner.os }}-pip-
      - name: install Python dependencies
        run: |
          pip install -r ./requirements/requirements.txt
      - name: Run Snyk to check for vulnerabilities
        uses: <ourorg>/snyk_actions/python@master
        with:
          command: test
          args: --file=requirements/requirements.txt --package-manager=pip
        env:
          SNYK_TOKEN: ${{ secrets.SNYK_TOKEN }}
However, when I run this, it still fails:
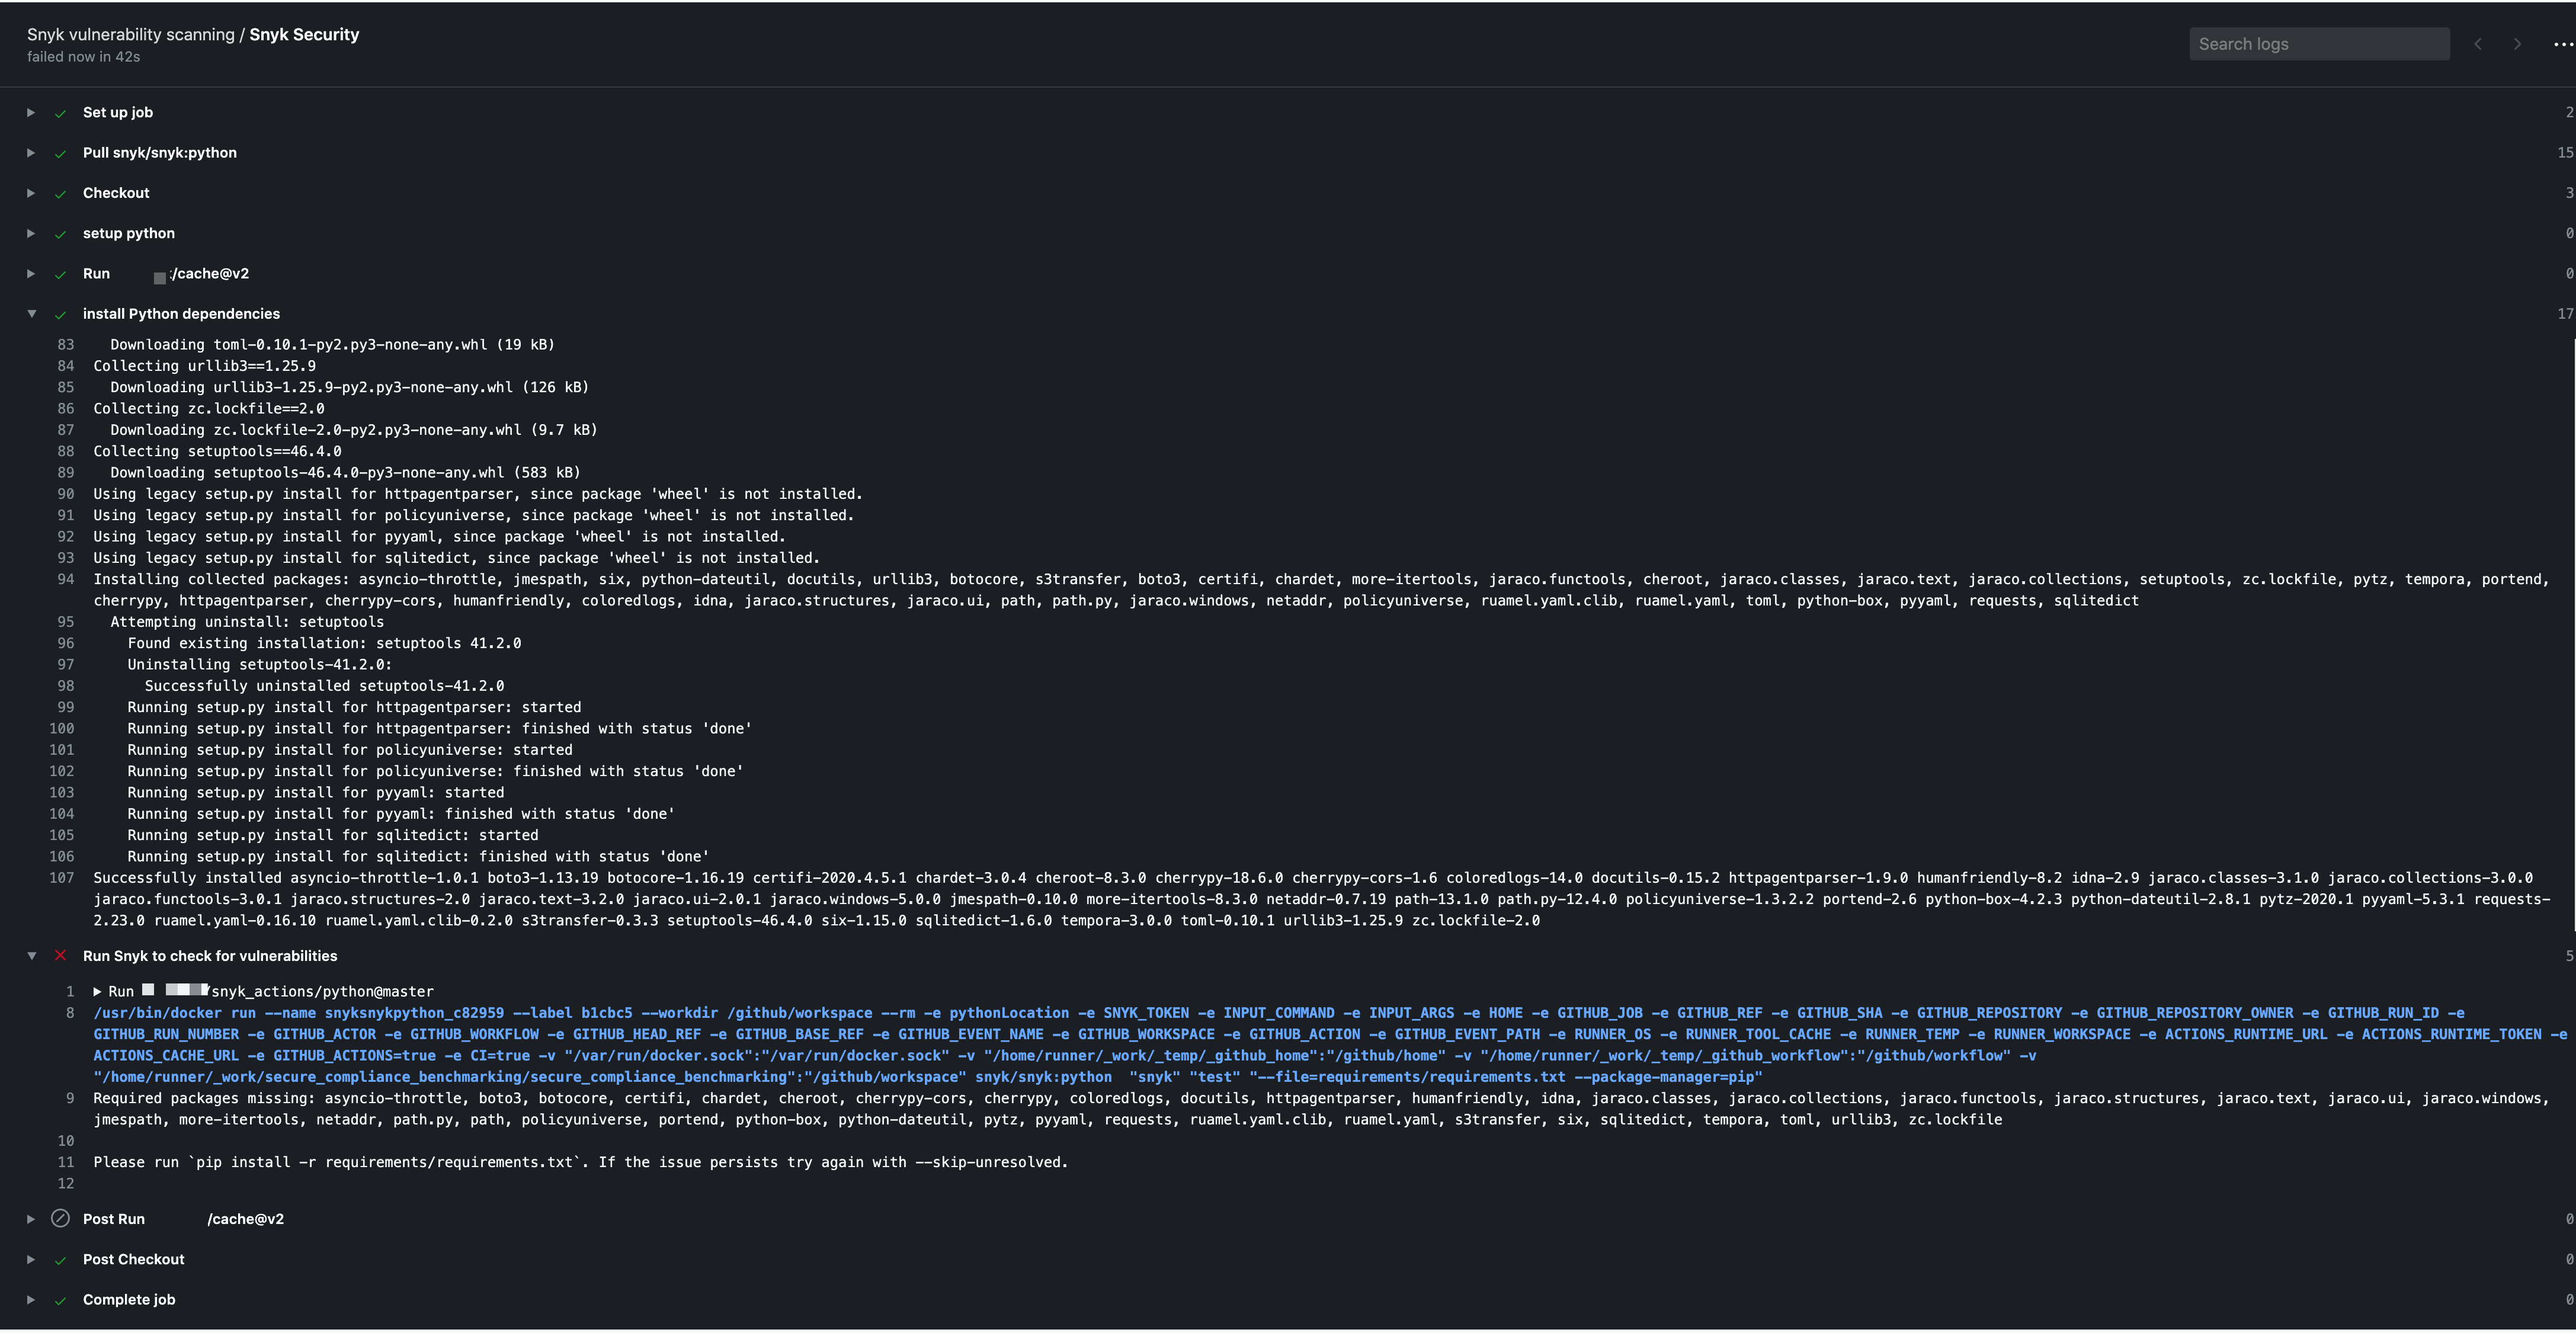
closed time in 12 days
klauern
issue commentsnyk/actions
Python Action can't find Pip dependencies
Apologies for talking a while to respond. My suspicion here is the Action is trying to access some private dependencies.
If this is still a problem, given you are already installing the packages, you could try the new setup action instead and use the already installed packages.
Please do reopen this issue if that doesn't work.
comment created time in 12 days
issue closedsnyk/actions
Docker: CLI option to disable suggestions for Dockerfile
We use Packer to build our containers, so there are no Dockerfiles available to add to the synk test cli command.
Is there an option for the cli to disable suggestions other than the synk config set ... shown in the response below?? This is run in CI/CD.
Organization:      myorg
Package manager:   apk
Docker image:      myapp:${IMAGE_TAG}
Licenses:          enabled

Tested 43 dependencies for known issues, found 4 issues.

Pro tip: use `--file` option to get base image remediation advice.
Example: $ snyk test --docker myapp:${IMAGE_TAG} --file=path/to/Dockerfile

To remove this message in the future, please run `snyk config set disableSuggestions=true`

##[error]Docker run failed with exit code 1
closed time in 12 days
stevenscg
issue commentsnyk/actions
Docker: CLI option to disable suggestions for Dockerfile
You can now specify an environment variable to disable this.
SNYK_CFG_DISABLESUGGESTIONS=true
comment created time in 12 days
created tagsnyk/actions
A set of GitHub actions for checking your projects for vulnerabilities
created time in 12 days
push eventsnyk/actions
commit sha abec0747818549380e93a2fb2b7539a982d3f1ae
Document the new setup action
push time in 12 days
push eventsnyk/actions
commit sha 32f47fe6615c9f6d98e508cf0602a1eff74ddc04
Document the new setup action
push time in 12 days
push eventgarethr/snykly
commit sha 5c3e08d793a8ea81de0bfa3587c39f3a62b5c9ab
Quote the output
push time in 12 days
push eventsnyk/actions
commit sha 54500275cdab7b778b8afb16c4d996af226bc5d1
Try and fix issue with echoing back the version
push time in 12 days
push eventsnyk/actions
commit sha f609ccfebb8989ddbfe82bb25c5ca02e78d63c9c
Correct escaping
push time in 12 days
push eventgarethr/snykly
commit sha 106cef30e30053c30094457d453ce1393806f5c9
Use output to show version
push time in 12 days
push eventsnyk/actions
commit sha 8351bef9ae7ae5a090e3dca40c10b6424cfde116
Deal with different types of runniing, and output snyk version
push time in 12 days
push eventsnyk/actions
commit sha 4d1354af64daba66b61403659d1e33cab7f0bfb2
Deal with different types of runniing, and output snyk version
push time in 12 days
push eventgarethr/snykly
commit sha a0b66213a0a8403fe7cc3df1148575cf10156db0
Add names to steps
push time in 12 days
push eventgarethr/snykly
commit sha 552c6044de5db246a9a67349ef76fde765021357
Add names to steps
push time in 12 days
push eventsnyk/actions
commit sha 8b574610fc9c03d22dfe18f5dfc1fab3d64eeca2
Set envs and try and handle specific versions
push time in 13 days
push eventgarethr/snykly
commit sha 20ecd44744768e23294dcee3dec571bf5f708366
Use new name for the action
push time in 13 days
push eventsnyk/actions
commit sha 795f351da25eb1bade0ffbaadd98d99ce78e7120
Rename to setup to match Actions conventions
push time in 13 days
push eventgarethr/snykly
commit sha 94a2f897cbf76575302a142e6ee91b5b6169dc50
Test with a specific Snyk version
push time in 13 days
push eventsnyk/actions
commit sha fdf7c83201b5c6d53fd83a74f218e81c5e7bdab5
Make the version explicit, similar to the setup standard actions
push time in 13 days
issue commentopen-policy-agent/opa
Download bundles from OCI-compatible registries
In my view this should be applicable to any user of Oras, rather than just Conftest. Implementing there has the advantage of it being useful and consistent for any consumer I feel.

comment created time in 13 days
push eventgarethr/snykus
commit sha a9a1dc14cb8d1e80ed16d56112a079e070a8de30
Add recommended labels and SHA tags
push time in 13 days
push eventsnyk/actions
commit sha 4c80f01a331a07f4694f13ef7e6cff87baa113f8
Add version environment variable
push time in 13 days
push eventgarethr/snykus
commit sha bcb836a112f03ab67aaa68b1cdc413ea9b74993e
Added a README
push time in 14 days
created taggarethr/snykus
A real-world workflow for using Docker, Snyk and GitHub to build, secure and publish container images.
created time in 14 days
created taggarethr/snykus
A real-world workflow for using Docker, Snyk and GitHub to build, secure and publish container images.
created time in 14 days
push eventgarethr/snykus
commit sha bde81621c7a23946d56d623f4a07a33c81f1d4d6
Added a license
push time in 14 days