








alibaba/macaca 2844
Automation solution for multi-platform. 多端自动化解决方案
aleafs/pm 275
A graceful node library to contribute a permanent "master-worker" server.
cancancan like authorization plugin for Egg.js
fengmk2/ChinaMobilePhoneNumberRegex 35
Regular expressions that match the mobile phone number in mainland China.
Node ZooKeeper Client in pure JS
client library for itier
Aliyun OCS(open cache storage) client. (Just a Memcache client)
Ask me anything!
Active, a user active loging and total service. 用户活跃跟踪统计系统
SDK on top of nodejs to build desktop apps using HTML5/CSS/JS
push eventcnpm/cnpmjs.org
commit sha 24a0039188b255dbc7709ce454404ce57578f34c
Release 3.0.0-rc.36
push time in 9 hours
push eventcnpm/cnpmjs.org
commit sha b7089d33d400f9fd4fc398479d4dac5aab26b633
fix: set maintainer to current user if maintainer is undefined (#1592) If pub with token, pkg has no default maintainer
push time in 9 hours
PR merged cnpm/cnpmjs.org
If pub with token, pkg has no default maintainer

pr closed time in 9 hours
Pull request review commentcnpm/cnpmjs.org
fix: set maintainer to current user if maintainer is undefined
describe('test/controllers/registry/package/save.test.js', function () { .expect(400, done); }); - it('should 400 when maintainers missing', function (done) {
这个测试保留
comment created time in 20 hours
Pull request review commentcnpm/cnpmjs.org
fix: set maintainer to current user if maintainer is undefined
var BASIC_PREFIX = /basic /i; var BEARER_PREFIX = /bearer /i; /**- * Parse the request authorization+ * Parse the request authorization222
222
comment created time in 20 hours
Pull request review commentcnpm/cnpmjs.org
fix: set maintainer to current user if maintainer is undefined
module.exports = function* save(next) { var versionPackage = pkg.versions[version]; var maintainers = versionPackage.maintainers; - // should never happened in normal request if (!maintainers) {- this.status = 400;- const error = '[maintainers_error] request body need maintainers';- this.body = {- error,- reason: error,- };- return;+ // With the token mode, pub lib with no maintainers
需要判断当前请求是 token 请求才能这样设置
comment created time in 20 hours
push eventcnpm/bug-versions
commit sha a3af24d6542fbd9323447c808b149fc7e158233b
feat: nodejs September 2020 Security Releases for Alinode (#110) Co-authored-by: fengmk2 <[email protected]>
push time in 2 days

PR closed cnpm/bug-versions

pr closed time in 2 days
pull request commentcnpm/bug-versions
feat: alinode September 2020 Security Releases
https://github.com/cnpm/bug-versions/pull/110
comment created time in 2 days
push eventlegendecas/bug-versions
commit sha f24cd16c6ff03ca92748c4e2ce9db870cf3da797
fix: report eslint-plugin-react bug version v7.21.0 (#112)
commit sha 4d42ccba4f54ca3f8454fbe713452580be6f82cc
fix: report eslint-plugin-react breaking version 7.21.1 (#113)
commit sha b04d893edf5ec71ac4053b12df490b174858ebcd
fix: eslint-plugin-react version (#114)
commit sha a41e78001a23c9ebbf6aeda79fbe14fc54ec1e86
fix: merge eslint-plugin-react config (#115)
commit sha 1d43a4f3d81eb193745b0085e771ddcf0d9eec83
Merge branch 'master' into sept-2020-sec-rel
push time in 2 days
push eventfengmk2/marky-markdown
commit sha dd700976ca43d5380fbbfcda3e471adda337217c
fix: package.json to reduce vulnerabilities The following vulnerabilities are fixed with an upgrade: - https://snyk.io/vuln/SNYK-JS-SANITIZEHTML-585892
push time in 2 days
create barnchfengmk2/marky-markdown
branch : snyk-fix-ca1abb700e40559b6083bcf3b63f7a85
created branch time in 2 days
PR opened cnpm/bug-versions
pr created time in 6 days
create barnchcnpm/bug-versions
branch : alinode-september-2020-security-releases
created branch time in 6 days
PR closed cnpm/bug-versions
package.json: codemirror": "^5.50.2"
使用版本:5.58.0

pr closed time in 6 days
issue closedeggjs/egg
egg router 写restful api的时候,访问不到路由是怎么回事?
路由上写了restful的路由,但是postman访问接口一直是{},啥都没有
router.js

控制器

postman返回

closed time in 8 days
TinchyChing
issue commenteggjs/egg
egg router 写restful api的时候,访问不到路由是怎么回事?
少了 await
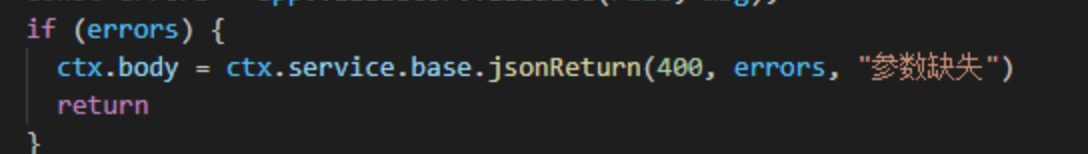
comment created time in 8 days
push eventcnpm/bug-versions
commit sha 36b018d48e80cc7e4870287d598c1b2229908943
feat: Node.js September 2020 Security Releases (#108) https://nodejs.org/en/blog/vulnerability/september-2020-security-releases/
push time in 8 days
delete branch cnpm/bug-versions
delete branch : september-2020-security-releases
delete time in 8 days
PR merged cnpm/bug-versions
https://nodejs.org/en/blog/vulnerability/september-2020-security-releases/
pr closed time in 8 days
PR opened cnpm/bug-versions
https://nodejs.org/en/blog/vulnerability/september-2020-security-releases/
pr created time in 8 days
create barnchcnpm/bug-versions
branch : september-2020-security-releases
created branch time in 8 days
push eventcnpm/cnpmjs.org
commit sha 2b74e00cb9ae20e9cf2f06c54ef8dbe6a36b4066
fix: release 3.0.0-rc.35 fix npm include functions dir
push time in 8 days
push eventcnpm/cnpmjs.org
commit sha d26e9fdff18e73b20567d8eeaac94dd3ad590af4
Release 3.0.0-rc.34
push time in 8 days
push eventcnpm/cnpmjs.org
commit sha 45f2f8b31f095eeadf0f47e234d6eb225e6b197f
feat: impl registry token api (#1590) Refs: - https://github.com/npm/registry/blob/master/docs/user/authentication.md
push time in 8 days
PR merged cnpm/cnpmjs.org
[x] doc added [x] test pass
Refs:
- https://github.com/npm/registry/blob/master/docs/user/authentication.md
pr closed time in 8 days
Pull request review commentcnpm/cnpmjs.org
+'use strict';++var should = require('should');+var uuid = require('uuid');+var Token = require('../../models').Token;+var TestUtil = require('../utils');++describe('models/token.test.js', function () {+ describe('deleteByKeyOrToken', function () {+ var token1;+ var token2;++ beforeEach(function *() {+ var token1Str = 'mock_token1_' + uuid.v4();+ var token2Str= 'mock_token2_' + uuid.v4();++ token1 = yield Token.add({+ token: token1Str,+ userId: TestUtil.admin,+ readonly: false,+ key: '1_token_1' + token1Str,+ cidrWhitelist: [],+ });++ token2 = yield Token.add({+ token: token2Str,+ userId: TestUtil.admin,+ readonly: false,+ key: '1_token_2' + token2Str,+ cidrWhitelist: [],+ });+ });++ describe('delete by key', function () {+ it('should work', function* () {+ yield Token.deleteByKeyOrToken(TestUtil.admin, '1_token_1');+ var tokenRow = yield Token.findByToken(token1.token);+ should.not.exist(tokenRow);+ });++ describe('key is ambiguous', function () {+ it('should not delete token', function* () {+ var error;+ try {+ yield Token.deleteByKeyOrToken(TestUtil.admin, '1_token_');+ } catch (e) {+ error = e;+ }+ should.exist(error);+ error.message.should.match(/Token ID ".+" was ambiguous/);
得加上一个判断,确保命中的 token 还在数据库里面没有被删除。
comment created time in 9 days
Pull request review commentcnpm/cnpmjs.org
+'use strict';++/*+CREATE TABLE IF NOT EXISTS `token` (+ `id` bigint(20) unsigned NOT NULL AUTO_INCREMENT COMMENT 'primary key',+ `gmt_create` datetime NOT NULL COMMENT 'create time',+ `gmt_modified` datetime NOT NULL COMMENT 'modified time',+ `token` varchar(100) NOT NULL COMMENT 'token',+ `user_id` varchar(100) NOT NULL COMMENT 'user name',+ `readonly` tinyint NOT NULL DEFAULT 0 COMMENT 'readonly or not, 1: true, other: false',+ `token_key` varchar(200) NOT NULL COMMENT 'token sha512 hash',+ `cidr_whitelist` varchar(500) NOT NULL COMMENT 'ip list, ["127.0.0.1"]',+ PRIMARY KEY (`id`),+ UNIQUE KEY `uk_token` (`token`),+ KEY `idx_user_id` (`user_id`)+) ENGINE=InnoDB DEFAULT CHARSET=utf8 COMMENT='token info';+ */++module.exports = function(sequelize, DataTypes) {+ return sequelize.define('Token', {+ token: {+ type: DataTypes.STRING(100),+ allowNull: false,+ comment: 'token',+ },+ userId: {+ field: 'user_id',+ type: DataTypes.STRING(100),+ allowNull: false,+ comment: 'user name'+ },+ readonly: {+ type: DataTypes.BOOLEAN,+ allowNull: false,+ defaultValue: false,+ comment: 'readonly or not, 1: true, other: false',+ },+ key: {+ field: 'token_key',+ type: DataTypes.STRING(256),+ allowNull: false,+ comment: 'token sha512 hash',+ },+ cidrWhitelist: {+ field: 'cidr_whitelist',+ type: DataTypes.STRING(500),+ allowNull: false,+ comment: 'ip list, ["127.0.0.1"]',+ get: function () {+ try {+ return JSON.parse(this.getDataValue('cidrWhitelist'));+ } catch (_) {+ return [];+ }+ },+ set: function (val) {+ try {+ var stringifyVal = JSON.stringify(val);+ this.setDataValue('cidrWhitelist', stringifyVal);+ } catch (_) {+ // ...+ }+ }+ },+ }, {+ tableName: 'token',+ comment: 'token info',+ indexes: [+ {+ unique: true,+ fields: [ 'token' ],+ },+ {+ fields: [ 'user_id' ],+ }+ ],+ classMethods: {+ findByToken: function* (token) {+ return yield this.find({ where: { token: token } });+ },+ add: function* (tokenObj) {+ var row = this.build(tokenObj);+ return yield row.save();+ },+ listByUser: function* (userId, offset, limit) {+ return yield this.findAll({+ where: {+ userId: userId,+ },+ limit: limit,+ offset: offset,+ order: 'id asc',+ });+ },+ deleteByKeyOrToken: function* (userId, keyOrToken) {+ var self = this;+ yield sequelize.transaction(function () {+ return self.destroy({+ where: {+ userId: userId,+ $or: [+ {+ key: {+ like: keyOrToken + '%',+ },+ }, {+ token: keyOrToken,+ }+ ],+ },+ }).then(function (affectedRows) {+ if (affectedRows > 1) {+ throw new Error(`Token ID "${keyOrToken}" was ambiguous`);
这样就能终止 destroy 不提交了?
comment created time in 9 days
Pull request review commentcnpm/cnpmjs.org
+'use strict';++/*+CREATE TABLE IF NOT EXISTS `token` (+ `id` bigint(20) unsigned NOT NULL AUTO_INCREMENT COMMENT 'primary key',+ `gmt_create` datetime NOT NULL COMMENT 'create time',+ `gmt_modified` datetime NOT NULL COMMENT 'modified time',+ `token` varchar(100) NOT NULL COMMENT 'token',+ `user` varchar(100) NOT NULL COMMENT 'user name',+ `readonly` tinyint NOT NULL DEFAULT 0 COMMENT 'readonly or not, 1: true, other: false',+ `token_key` varchar(200) NOT NULL COMMENT 'token sha512 hash',+ `cidr_whitelist` varchar(500) NOT NULL COMMENT 'ip list, ["127.0.0.1"]',+ PRIMARY KEY (`id`),+ UNIQUE KEY `uk_token` (`token`),+ KEY `idx_user` (`user`)+) ENGINE=InnoDB DEFAULT CHARSET=utf8 COMMENT='token info';+ */++module.exports = function(sequelize, DataTypes) {+ return sequelize.define('Token', {+ token: {+ type: DataTypes.STRING(100),+ allowNull: false,+ comment: 'token',+ },+ user: {
user 为什么是 string?而不是 userid 呢?
comment created time in 10 days
Pull request review commentcnpm/cnpmjs.org
+'use strict';++/*+CREATE TABLE IF NOT EXISTS `token` (+ `id` bigint(20) unsigned NOT NULL AUTO_INCREMENT COMMENT 'primary key',+ `gmt_create` datetime NOT NULL COMMENT 'create time',+ `gmt_modified` datetime NOT NULL COMMENT 'modified time',+ `token` varchar(100) NOT NULL COMMENT 'token',+ `user` varchar(100) NOT NULL COMMENT 'user name',+ `readonly` tinyint NOT NULL DEFAULT 0 COMMENT 'readonly or not, 1: true, other: false',+ `token_key` varchar(200) NOT NULL COMMENT 'token sha512 hash',+ `cidr_whitelist` varchar(500) NOT NULL COMMENT 'ip list, ["127.0.0.1"]',+ PRIMARY KEY (`id`),+ UNIQUE KEY `uk_token` (`token`),+ KEY `idx_user` (`user`)+) ENGINE=InnoDB DEFAULT CHARSET=utf8 COMMENT='token info';+ */++module.exports = function(sequelize, DataTypes) {+ return sequelize.define('Token', {+ token: {+ type: DataTypes.STRING(100),+ allowNull: false,+ comment: 'token',+ },+ user: {+ type: DataTypes.STRING(100),+ allowNull: false,+ comment: 'user name'+ },+ readonly: {+ type: DataTypes.BOOLEAN,+ allowNull: false,+ defaultValue: false,+ comment: 'readonly or not, 1: true, other: false',+ },+ key: {+ field: 'token_key',+ type: DataTypes.STRING(256),+ allowNull: false,+ comment: 'token sha512 hash',+ },+ cidrWhitelist: {+ field: 'cidr_whitelist',+ type: DataTypes.STRING(500),+ allowNull: false,+ comment: 'ip list, ["127.0.0.1"]',+ },+ }, {+ tableName: 'token',+ comment: 'token info',+ indexes: [+ {+ unique: true,+ fields: [ 'token' ],+ },+ {+ fields: [ 'user' ],+ }+ ],+ classMethods: {+ findByToken: function* (token) {+ return yield this.find({ where: { token: token } });+ },+ add: function* (tokenObj) {+ var whiteList = [];+ try {+ whiteList = JSON.stringify(tokenObj.cidrWhitelist);+ } catch (_) {+ // ...+ }+ var row = this.build({+ token: tokenObj.token,+ user: tokenObj.user,+ readonly: tokenObj.readonly,+ key: tokenObj.key,+ cidrWhitelist: whiteList,+ });+ return yield row.save();+ },+ listByUser: function* (user, offset, limit) {+ return yield this.findAll({+ where: {+ user: user,+ },+ limit: limit,+ offset: offset,+ order: 'id asc',+ });+ },+ deleteByKeyOrToken: function* (user, keyOrToken) {+ return yield this.destroy({+ where: {+ user: user,+ $or: [+ {+ key: {+ like: keyOrToken + '%',
模糊查询删除的需求是怎样的?如果我传 a,那么 a 开头的 key 都被删除了。。
comment created time in 10 days
Pull request review commentcnpm/cnpmjs.org
+'use strict';++/*+CREATE TABLE IF NOT EXISTS `token` (+ `id` bigint(20) unsigned NOT NULL AUTO_INCREMENT COMMENT 'primary key',+ `gmt_create` datetime NOT NULL COMMENT 'create time',+ `gmt_modified` datetime NOT NULL COMMENT 'modified time',+ `token` varchar(100) NOT NULL COMMENT 'token',+ `user` varchar(100) NOT NULL COMMENT 'user name',+ `readonly` tinyint NOT NULL DEFAULT 0 COMMENT 'readonly or not, 1: true, other: false',+ `token_key` varchar(200) NOT NULL COMMENT 'token sha512 hash',+ `cidr_whitelist` varchar(500) NOT NULL COMMENT 'ip list, ["127.0.0.1"]',+ PRIMARY KEY (`id`),+ UNIQUE KEY `uk_token` (`token`),+ KEY `idx_user` (`user`)+) ENGINE=InnoDB DEFAULT CHARSET=utf8 COMMENT='token info';+ */++module.exports = function(sequelize, DataTypes) {+ return sequelize.define('Token', {+ token: {+ type: DataTypes.STRING(100),+ allowNull: false,+ comment: 'token',+ },+ user: {+ type: DataTypes.STRING(100),+ allowNull: false,+ comment: 'user name'+ },+ readonly: {+ type: DataTypes.BOOLEAN,+ allowNull: false,+ defaultValue: false,+ comment: 'readonly or not, 1: true, other: false',+ },+ key: {+ field: 'token_key',+ type: DataTypes.STRING(256),+ allowNull: false,+ comment: 'token sha512 hash',+ },+ cidrWhitelist: {+ field: 'cidr_whitelist',+ type: DataTypes.STRING(500),+ allowNull: false,+ comment: 'ip list, ["127.0.0.1"]',+ },+ }, {+ tableName: 'token',+ comment: 'token info',+ indexes: [+ {+ unique: true,+ fields: [ 'token' ],+ },+ {+ fields: [ 'user' ],+ }+ ],+ classMethods: {+ findByToken: function* (token) {+ return yield this.find({ where: { token: token } });+ },+ add: function* (tokenObj) {+ var whiteList = [];+ try {+ whiteList = JSON.stringify(tokenObj.cidrWhitelist);+ } catch (_) {+ // ...+ }+ var row = this.build({+ token: tokenObj.token,+ user: tokenObj.user,+ readonly: tokenObj.readonly,+ key: tokenObj.key,+ cidrWhitelist: whiteList,+ });+ return yield row.save();+ },+ listByUser: function* (user, offset, limit) {+ return yield this.findAll({+ where: {+ user: user,+ },+ limit: limit,+ offset: offset,+ order: 'id asc',+ });+ },+ deleteByKeyOrToken: function* (user, keyOrToken) {
这里为啥没法分开按 key 还是 token 来查询删除呢?
comment created time in 10 days
Pull request review commentcnpm/cnpmjs.org
+'use strict';++/*+CREATE TABLE IF NOT EXISTS `token` (+ `id` bigint(20) unsigned NOT NULL AUTO_INCREMENT COMMENT 'primary key',+ `gmt_create` datetime NOT NULL COMMENT 'create time',+ `gmt_modified` datetime NOT NULL COMMENT 'modified time',+ `token` varchar(100) NOT NULL COMMENT 'token',+ `user` varchar(100) NOT NULL COMMENT 'user name',+ `readonly` tinyint NOT NULL DEFAULT 0 COMMENT 'readonly or not, 1: true, other: false',+ `token_key` varchar(200) NOT NULL COMMENT 'token sha512 hash',+ `cidr_whitelist` varchar(500) NOT NULL COMMENT 'ip list, ["127.0.0.1"]',+ PRIMARY KEY (`id`),+ UNIQUE KEY `uk_token` (`token`),+ KEY `idx_user` (`user`)+) ENGINE=InnoDB DEFAULT CHARSET=utf8 COMMENT='token info';+ */++module.exports = function(sequelize, DataTypes) {+ return sequelize.define('Token', {+ token: {+ type: DataTypes.STRING(100),+ allowNull: false,+ comment: 'token',+ },+ user: {+ type: DataTypes.STRING(100),+ allowNull: false,+ comment: 'user name'+ },+ readonly: {+ type: DataTypes.BOOLEAN,+ allowNull: false,+ defaultValue: false,+ comment: 'readonly or not, 1: true, other: false',+ },+ key: {+ field: 'token_key',+ type: DataTypes.STRING(256),+ allowNull: false,+ comment: 'token sha512 hash',+ },+ cidrWhitelist: {+ field: 'cidr_whitelist',+ type: DataTypes.STRING(500),+ allowNull: false,+ comment: 'ip list, ["127.0.0.1"]',+ },+ }, {+ tableName: 'token',+ comment: 'token info',+ indexes: [+ {+ unique: true,+ fields: [ 'token' ],+ },+ {+ fields: [ 'user' ],+ }+ ],+ classMethods: {+ findByToken: function* (token) {+ return yield this.find({ where: { token: token } });+ },+ add: function* (tokenObj) {+ var whiteList = [];+ try {+ whiteList = JSON.stringify(tokenObj.cidrWhitelist);+ } catch (_) {+ // ...+ }+ var row = this.build({+ token: tokenObj.token,+ user: tokenObj.user,+ readonly: tokenObj.readonly,+ key: tokenObj.key,+ cidrWhitelist: whiteList,+ });+ return yield row.save();+ },+ listByUser: function* (user, offset, limit) {+ return yield this.findAll({+ where: {+ user: user,+ },+ limit: limit,+ offset: offset,+ order: 'id asc',+ });+ },+ deleteByKeyOrToken: function* (user, keyOrToken) {+ return yield this.destroy({+ where: {+ user: user,+ $or: [+ {+ key: {+ like: keyOrToken + '%',
为什么这里是 like?key 应该是 sha256 啊
comment created time in 10 days
Pull request review commentcnpm/cnpmjs.org
+'use strict';++/*+CREATE TABLE IF NOT EXISTS `token` (+ `id` bigint(20) unsigned NOT NULL AUTO_INCREMENT COMMENT 'primary key',+ `gmt_create` datetime NOT NULL COMMENT 'create time',+ `gmt_modified` datetime NOT NULL COMMENT 'modified time',+ `token` varchar(100) NOT NULL COMMENT 'token',+ `user` varchar(100) NOT NULL COMMENT 'user name',+ `readonly` tinyint NOT NULL DEFAULT 0 COMMENT 'readonly or not, 1: true, other: false',+ `token_key` varchar(200) NOT NULL COMMENT 'token sha512 hash',+ `cidr_whitelist` varchar(500) NOT NULL COMMENT 'ip list, ["127.0.0.1"]',+ PRIMARY KEY (`id`),+ UNIQUE KEY `uk_token` (`token`),+ KEY `idx_user` (`user`)+) ENGINE=InnoDB DEFAULT CHARSET=utf8 COMMENT='token info';+ */++module.exports = function(sequelize, DataTypes) {+ return sequelize.define('Token', {+ token: {+ type: DataTypes.STRING(100),+ allowNull: false,+ comment: 'token',+ },+ user: {+ type: DataTypes.STRING(100),+ allowNull: false,+ comment: 'user name'+ },+ readonly: {+ type: DataTypes.BOOLEAN,+ allowNull: false,+ defaultValue: false,+ comment: 'readonly or not, 1: true, other: false',+ },+ key: {+ field: 'token_key',+ type: DataTypes.STRING(256),+ allowNull: false,+ comment: 'token sha512 hash',+ },+ cidrWhitelist: {+ field: 'cidr_whitelist',+ type: DataTypes.STRING(500),+ allowNull: false,+ comment: 'ip list, ["127.0.0.1"]',+ },+ }, {+ tableName: 'token',+ comment: 'token info',+ indexes: [+ {+ unique: true,+ fields: [ 'token' ],+ },+ {+ fields: [ 'user' ],+ }+ ],+ classMethods: {+ findByToken: function* (token) {+ return yield this.find({ where: { token: token } });+ },+ add: function* (tokenObj) {+ var whiteList = [];+ try {+ whiteList = JSON.stringify(tokenObj.cidrWhitelist);+ } catch (_) {+ // ...+ }+ var row = this.build({+ token: tokenObj.token,+ user: tokenObj.user,+ readonly: tokenObj.readonly,+ key: tokenObj.key,+ cidrWhitelist: whiteList,+ });+ return yield row.save();+ },+ listByUser: function* (user, offset, limit) {+ return yield this.findAll({+ where: {+ user: user,+ },+ limit: limit,+ offset: offset,+ order: 'id asc',+ });+ },+ deleteByKeyOrToken: function* (user, keyOrToken) {+ return yield this.destroy({+ where: {+ user: user,+ $or: [+ {+ key: {+ like: keyOrToken + '%',
key 是索引吗?
comment created time in 10 days
Pull request review commentcnpm/cnpmjs.org
+'use strict';++var should = require('should');+var app = require('../../../../servers/registry');+var request = require('supertest');
按 Python 和 @XadillaX 的硬核习惯,内置模块依赖放最上面,然后是三方模块,然后才是本地模块,所以 supertest 放 should 下面。
comment created time in 10 days
Pull request review commentcnpm/cnpmjs.org
+'use strict';++/*+CREATE TABLE IF NOT EXISTS `token` (+ `id` bigint(20) unsigned NOT NULL AUTO_INCREMENT COMMENT 'primary key',+ `gmt_create` datetime NOT NULL COMMENT 'create time',+ `gmt_modified` datetime NOT NULL COMMENT 'modified time',+ `token` varchar(100) NOT NULL COMMENT 'token',+ `user` varchar(100) NOT NULL COMMENT 'user name',+ `readonly` tinyint NOT NULL DEFAULT 0 COMMENT 'readonly or not, 1: true, other: false',+ `token_key` varchar(200) NOT NULL COMMENT 'token sha512 hash',+ `cidr_whitelist` varchar(500) NOT NULL COMMENT 'ip list, ["127.0.0.1"]',+ PRIMARY KEY (`id`),+ UNIQUE KEY `uk_token` (`token`),+ KEY `idx_user` (`user`)+) ENGINE=InnoDB DEFAULT CHARSET=utf8 COMMENT='token info';+ */++module.exports = function(sequelize, DataTypes) {+ return sequelize.define('Token', {+ token: {+ type: DataTypes.STRING(100),+ allowNull: false,+ comment: 'token',+ },+ user: {+ type: DataTypes.STRING(100),+ allowNull: false,+ comment: 'user name'+ },+ readonly: {+ type: DataTypes.BOOLEAN,+ allowNull: false,+ defaultValue: false,+ comment: 'readonly or not, 1: true, other: false',+ },+ key: {+ field: 'token_key',+ type: DataTypes.STRING(256),+ allowNull: false,+ comment: 'token sha512 hash',+ },+ cidrWhitelist: {+ field: 'cidr_whitelist',+ type: DataTypes.STRING(500),+ allowNull: false,+ comment: 'ip list, ["127.0.0.1"]',+ },+ }, {+ tableName: 'token',+ comment: 'token info',+ indexes: [+ {+ unique: true,+ fields: [ 'token' ],+ },+ {+ fields: [ 'user' ],+ }+ ],+ classMethods: {+ findByToken: function* (token) {+ return yield this.find({ where: { token: token } });+ },+ add: function* (tokenObj) {+ var whiteList = [];+ try {+ whiteList = JSON.stringify(tokenObj.cidrWhitelist);
为什么 cidrWhitelist 的 JSON.stringify 在添加的时候是 model 处理的,而读取的时候是 service 处理的? 我理解应该要么 service 处理,要么 model 处理,否则分开2层,后续变化逻辑会遗漏,而且相同逻辑放到2个地方了。
comment created time in 10 days
Pull request review commentcnpm/cnpmjs.org
+'use strict';++/*+CREATE TABLE IF NOT EXISTS `token` (+ `id` bigint(20) unsigned NOT NULL AUTO_INCREMENT COMMENT 'primary key',+ `gmt_create` datetime NOT NULL COMMENT 'create time',+ `gmt_modified` datetime NOT NULL COMMENT 'modified time',+ `token` varchar(100) NOT NULL COMMENT 'token',+ `user` varchar(100) NOT NULL COMMENT 'user name',+ `readonly` tinyint NOT NULL DEFAULT 0 COMMENT 'readonly or not, 1: true, other: false',+ `token_key` varchar(200) NOT NULL COMMENT 'token sha512 hash',+ `cidr_whitelist` varchar(500) NOT NULL COMMENT 'ip list, ["127.0.0.1"]',+ PRIMARY KEY (`id`),+ UNIQUE KEY `uk_token` (`token`),+ KEY `idx_user` (`user`)+) ENGINE=InnoDB DEFAULT CHARSET=utf8 COMMENT='token info';+ */++module.exports = function(sequelize, DataTypes) {+ return sequelize.define('Token', {+ token: {+ type: DataTypes.STRING(100),+ allowNull: false,+ comment: 'token',+ },+ user: {+ type: DataTypes.STRING(100),+ allowNull: false,+ comment: 'user name'+ },+ readonly: {+ type: DataTypes.BOOLEAN,+ allowNull: false,+ defaultValue: false,+ comment: 'readonly or not, 1: true, other: false',+ },+ key: {+ field: 'token_key',+ type: DataTypes.STRING(256),+ allowNull: false,+ comment: 'token sha512 hash',+ },+ cidrWhitelist: {+ field: 'cidr_whitelist',+ type: DataTypes.STRING(500),+ allowNull: false,+ comment: 'ip list, ["127.0.0.1"]',+ },+ }, {+ tableName: 'token',+ comment: 'token info',+ indexes: [+ {+ unique: true,+ fields: [ 'token' ],+ },+ {+ fields: [ 'user' ],+ }+ ],+ classMethods: {+ findByToken: function* (token) {+ return yield this.find({ where: { token: token } });+ },+ add: function* (tokenObj) {+ var whiteList = [];+ try {+ whiteList = JSON.stringify(tokenObj.cidrWhitelist);+ } catch (_) {+ // ...+ }+ var row = this.build({+ token: tokenObj.token,+ user: tokenObj.user,+ readonly: tokenObj.readonly,+ key: tokenObj.key,+ cidrWhitelist: whiteList,+ });+ return yield row.save();+ },+ listByUser: function* (user, offset, limit) {+ return yield this.findAll({+ where: {+ user: user,+ },+ limit: limit,+ offset: offset,+ order: 'id asc',+ });+ },+ deleteByKeyOrToken: function* (user, keyOrToken) {+ return yield this.destroy({+ where: {+ user: user,+ $or: [+ {+ key: {+ like: keyOrToken + '%',
这样写不会有 sql 注入吧?
comment created time in 10 days
Pull request review commentcnpm/cnpmjs.org
module.exports = function* addUser() { return; } if (loginedUser) {+ var token = yield tokenService.createToken(body.name, {
好吧,忽略我吧,我会在 changelog 写明白需要新增一个表。我想起我们数据库变更部署 major 的。
comment created time in 10 days
Pull request review commentcnpm/cnpmjs.org
module.exports = function* addUser() { return; } if (loginedUser) {+ var token = yield tokenService.createToken(body.name, {
这里需要加个开关判断,没有开启 token 就没有 token 能力,否则 cnpmjs.org 需要发一个 major 版本,因为涉及数据库变更了。
comment created time in 10 days
Pull request review commentcnpm/cnpmjs.org
+'use strict';++var tokenService = require('../../../services/token');++var DEFAULT_PER_PAGE = 10;+var MIN_PER_PAGE = 1;+var MAX_PER_PAGE = 9999;++module.exports = function* createToken() {+ var perPage = typeof this.query.perPage === 'undefined' ? DEFAULT_PER_PAGE : parseInt(this.query.perPage);+ if (Number.isNaN(perPage)) {+ this.status = 400;+ var error = 'perPage ' + this.query.perPage + ' is not a number';+ this.body = {+ error,+ reason: error,+ };+ return;+ }+ if (perPage < MIN_PER_PAGE || perPage > MAX_PER_PAGE) {+ this.status = 400;+ var error = 'perPage ' + this.query.perPage + ' is out of boundary';+ this.body = {+ error,+ reason: error,+ };+ return;+ }++ var page = typeof this.query.page === 'undefined' ? 0 : parseInt(this.query.page);+ if (Number.isNaN(page)) {+ this.status = 400;+ var error = 'page ' + this.query.page + ' is not a number';+ this.body = {+ error,+ reason: error,+ };+ return;+ }+ if (page < 0) {+ this.status = 400;+ var error = 'page ' + this.query.page + ' is invalidate';+ this.body = {+ error,+ reason: error,+ };+ return;+ }++ var tokens = yield tokenService.listToken(this.user.name, {+ page: page,+ perPage: perPage,+ });++ this.status = 200;+ this.body = {+ objects: tokens,+ urls: {},
https://github.com/npm/registry/blob/master/docs/user/authentication.md#page urls 不是可选的?如果不是,那么 total 也应该需要返回。
comment created time in 10 days
Pull request review commentcnpm/cnpmjs.org
+'use strict';++var ipRegex = require('ip-regex');+var tokenService = require('../../../services/token');+var userService = require('../../../services/user');+var ipv4 = ipRegex.v4({ exact: true });++module.exports = function* createToken() {+ var readonly = this.request.body.readonly;+ if (typeof readonly !== 'undefined' && typeof readonly !== 'boolean') {+ this.status = 400;+ var error = '[bad_request] readonly ' + readonly + ' is not boolean';+ this.body = {+ error,+ reason: error,+ };+ return;+ }+ var cidrWhitelist = this.request.body.cidr_whitelist;+ if (typeof cidrWhitelist !== 'undefined') {+ var isValidateWhiteList = Array.isArray(cidrWhitelist) && cidrWhitelist.every(function (cidr) {+ return ipv4.test(cidr);+ });+ if (!isValidateWhiteList) {+ this.status = 400;+ var error = '[bad_request] cide white list ' + JSON.stringify(cidrWhitelist) + ' is not boolean';
is not boolean? 这里应该写错了
comment created time in 10 days
pull request commentnode-modules/hessian.js
@gxcsoccer 老版本也都修复掉吧

comment created time in 11 days
Pull request review commentnode-modules/hessian.js
describe('double.test.js', function () { utils.bytes('v2/double/32766.99999') ); assert.deepEqual(hessian.encode(java.double(32768), '2.0'), utils.bytes('v2/double/32768'));+ assert.deepEqual(hessian.encode(java.double(19400447), '2.0'), utils.bytes('v2/double/19400447'));
循环跑一百次,确保持续稳定性
comment created time in 11 days
Pull request review commentnode-modules/hessian.js
exports.addByteCodes = function addByteCodes(map, codes, method) { } } };++/**+ * float32 may has accuracy issue+ *+ * @example+ * ----------------+ * const buf = Buffer.allocUnsafe(4);+ * buf.writeFloatBE(19400447, 0);+ * buf.readFloatBE(0) // here result is 19400448+ *+ * @param {number} input The input+ * @return {boolean} { description_of_the_return_value }+ */+exports.float32Test = function float32Test(input) {+ FLOAT_TEST_BUF.fill(0);
这个去掉,性能会好很多
comment created time in 11 days
pull request commentcnpm/mirrors
fix: chromium_revisions should be string
https://cnpmjs.org/mirrors/chromium-browser-snapshots/Linux_x64/800071/
comment created time in 15 days
push eventcnpm/mirrors
commit sha 060c6caec47b28f98d871bc848c30f894688721e
fix: chromium_revisions should be string (#259)
push time in 15 days
PR merged cnpm/mirrors
<!-- Reviewable:start --> This change is <img src="https://reviewable.io/review_button.svg" height="34" align="absmiddle" alt="Reviewable"/> <!-- Reviewable:end -->
pr closed time in 15 days
push eventfengmk2/antd-tools
commit sha 407be7afccb796ffc910e12ff55e0e78b04f69c1
fix: package.json to reduce vulnerabilities The following vulnerabilities are fixed with an upgrade: - https://snyk.io/vuln/SNYK-JS-NODEFETCH-674311
push time in 16 days
create barnchfengmk2/antd-tools
branch : snyk-fix-f2499376a5476e0c4e1f0ca2c875d25f
created branch time in 16 days
issue commenteggjs/egg
默认 POST 请求传递的 data 参数就是以 application/x-www-form-urlencoded 传输的。

comment created time in 19 days
issue commentali-sdk/ali-rds
https://github.com/ali-sdk/ali-rds/blob/master/lib/client.js#L37 可以覆盖这个方法实现

comment created time in 19 days
issue closedcnpm/nodeinstall
Error: GET http://alinode.aliyun.com/dist/new-alinode/v5.16.3/SHASUMS256.txt got 404
nodeinstall --install-alinode ^5
Error: GET http://alinode.aliyun.com/dist/new-alinode/v5.16.3/SHASUMS256.txt got 404
System: Ubuntu 18.04
closed time in 20 days
dreamerblue
issue commentcnpm/nodeinstall
Error: GET http://alinode.aliyun.com/dist/new-alinode/v5.16.3/SHASUMS256.txt got 404
Can access now http://alinode.aliyun.com/dist/new-alinode/v5.16.3/SHASUMS256.txt
alt: https://npm.taobao.org/mirrors/alinode/v5.16.3/
comment created time in 20 days
pull request commenteggjs/egg
fix: only set keep-alive header before Node.js 14.8.0
@atian25 你来发版本

comment created time in 21 days
push eventeggjs/egg
commit sha d25d32e584b0bfd80f21cc522b91ac465f2852ac
fix: only set keep-alive header before Node.js 14.8.0 (#4457)
push time in 21 days
PR merged eggjs/egg

<!-- Thank you for your pull request. Please review below requirements. Bug fixes and new features should include tests and possibly benchmarks. Contributors guide: https://github.com/eggjs/egg/blob/master/CONTRIBUTING.md
感谢您贡献代码。请确认下列 checklist 的完成情况。 Bug 修复和新功能必须包含测试,必要时请附上性能测试。 Contributors guide: https://github.com/eggjs/egg/blob/master/CONTRIBUTING.md -->
Checklist
<!-- Remove items that do not apply. For completed items, change [ ] to [x]. -->
- [ ]
npm testpasses - [ ] tests and/or benchmarks are included
- [ ] documentation is changed or added
- [ ] commit message follows commit guidelines
Affected core subsystem(s)
<!-- Provide affected core subsystem(s). -->
Description of change
Node.js 14.8.0 will set Keep-Alive header, so it'll be dup

- https://github.com/nodejs/node/pull/34561
- https://github.com/nodejs/node/pull/34704
unittest is here: https://github.com/eggjs/egg/blob/master/test/app/middleware/meta.test.js#L67
pr closed time in 21 days
Pull request review commenteggjs/egg
fix: only set keep-alive header before Node.js 14.8.0
module.exports = options => { // total response time header ctx.set('x-readtime', Date.now() - ctx.starttime); - // try to support Keep-Alive Header+ // Node.js >=14.8.0 will set Keep-Alive Header, see https://github.com/nodejs/node/pull/34561+ const shouldPatchKeepAliveHeader = semver.lt(process.version, '14.8.0');++ // try to support Keep-Alive Header when < 14.8.0 const server = ctx.app.server;- if (server && server.keepAliveTimeout && server.keepAliveTimeout >= 1000 && ctx.header.connection !== 'close') {+ if (shouldPatchKeepAliveHeader && server && server.keepAliveTimeout && server.keepAliveTimeout >= 1000 && ctx.header.connection !== 'close') {
单测是否有?加上单测确保只会设置一次 header
comment created time in 22 days
create barnchfengmk2/pangyp
branch : snyk-fix-0f81f0e83e41b609028af89a2dbdae0c
created branch time in 22 days
push eventfengmk2/pangyp
commit sha 89cea51861fe15a50a928be475f4a760657acafb
fix: package.json to reduce vulnerabilities The following vulnerabilities are fixed with an upgrade: - https://snyk.io/vuln/SNYK-JS-BL-608877
push time in 22 days
create barnchcnpm/npm
branch : snyk-fix-921cee9f5548a05c2d15b44bab17a49e
created branch time in 22 days
push eventcnpm/npm
commit sha 5032fb64729f4a19791f51284a5c8f87da31bf51
fix: package.json to reduce vulnerabilities The following vulnerabilities are fixed with an upgrade: - https://snyk.io/vuln/SNYK-JS-BL-608877
push time in 22 days
push eventfengmk2/spm
commit sha d7318e763226b740160563b62381c147461037f7
fix: package.json to reduce vulnerabilities The following vulnerabilities are fixed with an upgrade: - https://snyk.io/vuln/SNYK-JS-BL-608877
push time in 23 days
create barnchfengmk2/spm
branch : snyk-fix-2df07a6ead215e7975529a89afbff144
created branch time in 23 days
push eventfengmk2/sief
commit sha c5bdde72cb5920f36cbad0273d9208cf2369a1f8
fix: package.json to reduce vulnerabilities The following vulnerabilities are fixed with an upgrade: - https://snyk.io/vuln/SNYK-JS-BL-608877
push time in 23 days
create barnchfengmk2/sief
branch : snyk-fix-3a31209f6283e06d0655515a3f6cbd8c
created branch time in 23 days
Pull request review commenteggjs/egg-schedule
fix: reject error should detect as fail
module.exports = app => { // execute return schedule.task(ctx, ...info.args) .catch(err => {- logger.error(`[Job#${id}] ${key} execute error.`, err);- return err;+ return is.error(err) ? err : new Error(err);
之前是三个逻辑,error,fail,success,现在变成了2个逻辑了。。。感觉不对啊
comment created time in a month
push eventfengmk2/chrome2calltree
commit sha b8ef8c21ea5bcd6141d3563194d220a7fcd1daa3
fix: package.json to reduce vulnerabilities The following vulnerabilities are fixed with an upgrade: - https://snyk.io/vuln/SNYK-JS-LODASH-608086
push time in a month