








Android Observatory - APK signature/metadata repository
An interactive shell designed for RFC 8555 ACME client/server developers to use for tests, day to day tasks, and exploring the protocol
cpu/ecbb 2
:robot: :book: Electronic Code Book Bot :book: :robot:
Certbot, previously the Let's Encrypt Client, is EFF's tool to obtain certs from Let's Encrypt, and (optionally) autoenable HTTPS on your server. It can also act as a client for any other CA that uses the ACME protocol.
cpu/acme 0
:lock: acmetool, an automatic certificate acquisition tool for ACME (Let's Encrypt)
Go client library implementation for ACME v2
Limited DNS server with RESTful HTTP API to handle ACME DNS challenges easily and securely.
ACME Specification
Java client for ACME (Let's Encrypt)
PR merged zmap/zlint
Updates to https://github.com/zmap/zcrypto/commit/ea3fdbd5ea270b7309385ea8a4148ba27a110e2a ahead of cutting a minor release.
Diff since current version (efd761a7b7b0): https://github.com/zmap/zcrypto/compare/efd761a7b7b0..master

pr closed time in 18 minutes
push eventzmap/zlint
commit sha 7e75dc35e04f682f0d0eb3de6d4af49ccd5db5af
deps: update zcrypto to ea3fdbd (#604)
push time in 18 minutes
push eventletsencrypt/sre-tools
commit sha 9af5cc487ecd62fb01fd04927c2785c9d69addf1
with query
push time in an hour
push eventletsencrypt/sre-tools
commit sha d50531611ef0590c284b3c87c22ac7a369b14dbb
Staging
push time in an hour
startedantirez/hping
started time in an hour
issue commentabetterinternet/crustls
Factor out shared Session code
dyn Connection was my original plan but AFAICT I can't downcast a dyn Connection to ServerConnection or ClientConnection. If I'm wrong about that, that'd be great!
comment created time in 2 hours
issue commentnix-rust/nix
Possible UB since preadv accepts &[IoVec<&mut [u8]>]
Example in the Rust playground that (I think) implements the same behavior as these methods. It works with unsafe, but don't pass the Miri checks. https://play.rust-lang.org/?version=stable&mode=debug&edition=2018&gist=8cb8a4507c42d86f6efd8a81d31f89d6

comment created time in 2 hours
issue commentnix-rust/nix
Possible UB since preadv accepts &[IoVec<&mut [u8]>]
Came here to file the same issue for process_vm_readv, which has the same problem. IANA expert, but I started digging into this when I was writing a wrapper for process_vm_readv, and found I couldn't have it take &&mut [u8] without using unsafe to coerce pointers, and doing so would cause Miri to flag it as UB.
The language docs on interior mutability seem pretty clear that the current implementation is UB. https://rust-lang.github.io/unsafe-code-guidelines/glossary.html#interior-mutability
comment created time in 2 hours
created taggoogle/tink
Tink is a multi-language, cross-platform, open source library that provides cryptographic APIs that are secure, easy to use correctly, and hard(er) to misuse.
created time in 3 hours
created taggoogle/tink
Tink is a multi-language, cross-platform, open source library that provides cryptographic APIs that are secure, easy to use correctly, and hard(er) to misuse.
created time in 3 hours
push eventgoogle/tink
commit sha 871f410d4b6b121361e4b030ca0479b51ec08870
apps-webpush-1.6.0 Javadoc auto-pushed to gh-pages
push time in 3 hours
push eventgoogle/tink
commit sha 97cdb248638b9419a83309c1c517e0edca660f71
apps-rewardedads-1.6.0 Javadoc auto-pushed to gh-pages
push time in 3 hours
push eventcertbot/certbot
commit sha 2df279bc5bb30a38e4f9c1c5e44a7b327c56743c
cli: dont double-print choosing plugins error (#8850)
push time in 3 hours
PR merged certbot/certbot
... for certonly and renew. Other verbs aren't affected.
I don't think the Could not choose appropriate plugin: ... message adds any meaning to the error.
certonly before:

certonly after:

renew before:
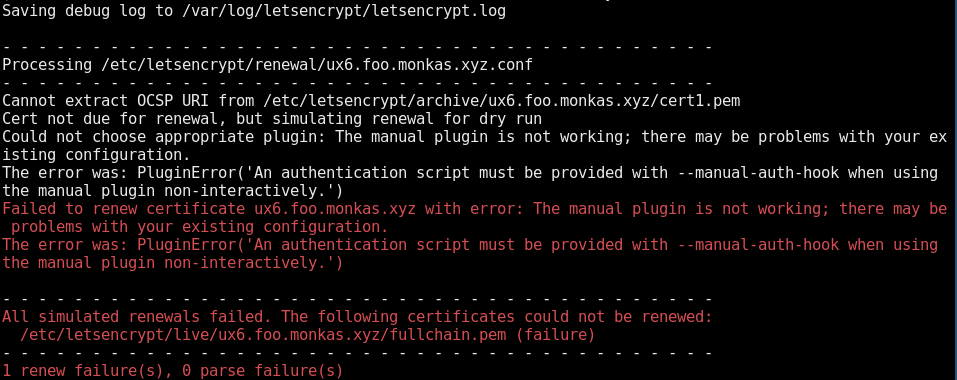
renew after:
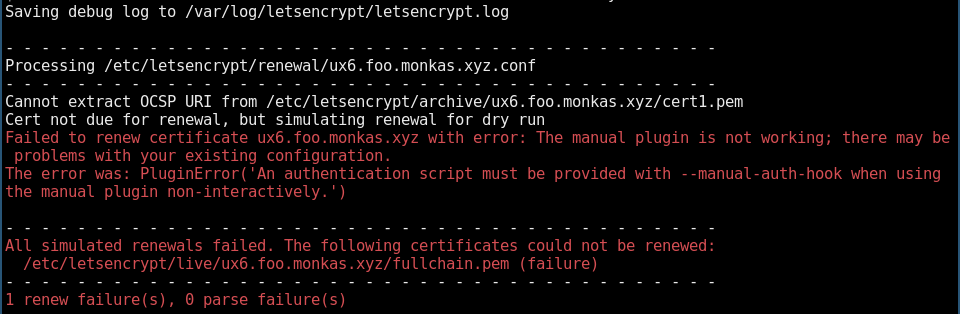

pr closed time in 3 hours
push eventgoogle/tink
commit sha 33d8b99b77381d5aa32f05242a3f3eac2c05baa6
apps-paymentmethodtoken-1.6.0 Javadoc auto-pushed to gh-pages
push time in 3 hours
push eventgoogle/tink
commit sha 625e4825e18cbfa3607a711d0235179b7fd265e8
tink-android-1.6.0 Javadoc auto-pushed to gh-pages
push time in 3 hours
push eventgoogle/tink
commit sha 3ec8544dcd52c5efb46c9af0d7f17bb0c40ecd91
tink-gcpkms-1.6.0 Javadoc auto-pushed to gh-pages
push time in 3 hours
push eventgoogle/tink
commit sha 1c13f96e2f524526cd252604be2922e1d9f2de7c
tink-awskms-1.6.0 Javadoc auto-pushed to gh-pages
push time in 3 hours
push eventgoogle/tink
commit sha de70e4a3e9c823c3bf47edebf2b384d4ce8ae6d1
tink-1.6.0 Javadoc auto-pushed to gh-pages
push time in 3 hours
push eventletsencrypt/boulder
commit sha f2eaa4b6d3772c8d54fd102778eeaf2932e885ca
Addressing Comments
push time in 3 hours
Pull request review commentletsencrypt/boulder
id-exporter: Gather example hostnames in addition to IDs
func (c idExporter) findIDs() ([]id, error) { c.log.AuditErrf("Error finding IDs: %s", err) return nil, err }+ return holder, nil+} - return idsList, nil+// Find all registration IDs with unexpired certificates and gather an+// example hostname.+func (c idExporter) findIDsWithExampleHostnames() (idExporterResults, error) {+ var holder idExporterResults+ _, err := c.dbMap.Select(+ // A previous version of this query resulted in an off-by-one+ // error, the resulting change removed `ANY_VALUE(...)` for the+ // hostname. This query now relies upon undefined behavior.+ // Though, the use of `ANY_VALUE` was itself a defined but+ // nondeterministic behavior.
While reasoning through this I realized that I only yanked this from the writeup that @jcjones did because I wanted a future engineer to avoid introducing the off-by-one error present in the original query. However, we've got tests for that. We can just get rid of this.
@jcjones should probably be the one to address why this query is safe / acceptable though.

comment created time in 3 hours
Pull request review commentletsencrypt/sre-tools
+package main++import (+ "context"+ "errors"+ "flag"+ "fmt"+ "io/ioutil"+ "log"+ "os"++ "github.com/aws/aws-sdk-go-v2/aws"+ "github.com/aws/aws-sdk-go-v2/config"+ "github.com/aws/aws-sdk-go-v2/credentials"+ "github.com/aws/aws-sdk-go-v2/service/s3"+ "gopkg.in/yaml.v2"+)++// Config and it's fields are exported to recieve the contents of a YAML+// configuration file+type Conf struct {+ SecretAccessKey string `yaml:"secret_access_key"`+ AccessKeyID string `yaml:"access_key_id"`+ Region string `yaml:"region"`+ BucketName string `yaml:"bucket_name"`
Nope. Just make sure SRE treats the whole config as a secret when they deploy it.
comment created time in 3 hours
issue openedsmallstep/certificates
Remove requirement for OIDC well-known endpoint to have jwks_uri set
What would you like to be added
Per https://github.com/smallstep/certificates/blob/5a6517ca5b963e09e5d9cc66b66521cc71c6483e/authority/provisioner/oidc.go#L34 and https://github.com/smallstep/certificates/blob/5a6517ca5b963e09e5d9cc66b66521cc71c6483e/authority/provisioner/oidc.go#L195 a jwks_uri needs to be provided.
Why this is needed
Current OIDC provider does not provide jwks_uri in OIDC well-known endpoint, and only supports HS256 (can't be switched to RS256 either).
The well-known endpoint from oidc provider returns:
{
    "issuer": "https://example.com/",
    "authorization_endpoint": "https://example.com/login/oauth/authorize",
    "token_endpoint": "https://example.com/login/oauth/access_token",
    "response_types_supported": [
        "code",
        "id_token"
    ]
}
PS, ❤️ Thanks for Smallstep suite of OSS that you publish.
created time in 4 hours
startedAkihiroSuda/lima
started time in 4 hours
startedqxinGitHub/Remove-web-limits-
started time in 4 hours
Pull request review commentletsencrypt/boulder
id-exporter: Gather example hostnames in addition to IDs
func (c idExporter) findIDs() ([]id, error) { c.log.AuditErrf("Error finding IDs: %s", err) return nil, err }+ return holder, nil+} - return idsList, nil+// Find all registration IDs with unexpired certificates and gather an+// example hostname.+func (c idExporter) findIDsWithExampleHostnames() (idExporterResults, error) {+ var holder idExporterResults+ _, err := c.dbMap.Select(+ // A previous version of this query resulted in an off-by-one+ // error, the resulting change removed `ANY_VALUE(...)` for the+ // hostname. This query now relies upon undefined behavior.+ // Though, the use of `ANY_VALUE` was itself a defined but+ // nondeterministic behavior.+ //+ // It turns out that MariaDB also has a configuration option to+ // prohibit this undefined behavior+ // (https://mariadb.com/kb/en/sql-mode/#only_full_group_by) but+ // it defaults to off, letting us access the multiverse of+ // possibilities that only undefined behavior can truly tap.+ &holder,+ `SELECT SQL_BIG_RESULT cert.registrationID AS id,+ name.reversedName AS hostname
		`SELECT SQL_BIG_RESULT
		        cert.registrationID AS id,
			name.reversedName AS hostname
comment created time in 4 hours
Pull request review commentletsencrypt/boulder
id-exporter: Gather example hostnames in addition to IDs
func (c idExporter) findIDs() ([]id, error) { c.log.AuditErrf("Error finding IDs: %s", err) return nil, err }+ return holder, nil+} - return idsList, nil+// Find all registration IDs with unexpired certificates and gather an+// example hostname.+func (c idExporter) findIDsWithExampleHostnames() (idExporterResults, error) {+ var holder idExporterResults+ _, err := c.dbMap.Select(+ // A previous version of this query resulted in an off-by-one+ // error, the resulting change removed `ANY_VALUE(...)` for the+ // hostname. This query now relies upon undefined behavior.+ // Though, the use of `ANY_VALUE` was itself a defined but+ // nondeterministic behavior.
This comment is confusing because the "previous version" is not visible here. In general when putting a comment in place for the long haul, rather than phrase things in terms of what used to be, it's better to phrase them in terms of "here's why we can't do it X way." In other words, think of the mental state of your future reader: They're not thinking about what the previous query looked like. They're thinking about how else they might implement it.
Also "undefined behavior" is pretty scary! Can you provide an explanation of why it's safe enough to use here?
comment created time in 4 hours
issue commentpyca/cryptography
Being able to read PKCS12 'friendly name'
I did a little more digging and there are in fact specific functions which can retrieve the trusted settings. (See here)
alias (friendlyName) -> X509_alias_get0 keyid (localKeyID) -> X509_keyid_get0
In particular X509_alias_get0 is already included in cryptography so as a temporary hack @felixfontein it would be possible to do the following:
from cryptography.x509 import load_pem_x509_certificate
from cryptography.hazmat.primitives.serialization.pkcs12 import load_key_and_certificates
from cryptography.hazmat.primitives.serialization import Encoding

with open('./any_pkcs12_file', 'rb') as p12:
    pkcs12 = load_key_and_certificates(
        p12.read(),
        password='password'.encode('UTF-8'),
    )

_, cert, _ = pkcs12

print(
    cert._backend._ffi.string(
        cert._backend._lib.X509_alias_get0(
            cert._x509, cert._backend._ffi.new("int *")
        )
    )
)
comment created time in 4 hours
pull request commentletsencrypt/boulder
Add lower, faster duplicate certificate rate limit
We should make sure to update the rate-limits page and do an API Announcement before updating the config in prod.
I wanted to add that a few months back I submitted a PR against the website for a complete overhaul of the rate-limits page (https://github.com/letsencrypt/website/pull/1167) that received a pretty good amount of review and revision. I closed it because I figured things were too hectic and there might be drastic changes needed later. Though I cannot reopen it, I still have the complete text ready to go. If you let me know the upcoming error-wording, I can incorporate this new rate limit and submit a new PR to have a shiny new limits page to go with the shiny new rate limit.

comment created time in 4 hours