








Effortless realtime data management for React + Feathers applications
Isabelle/IsaPlanner SML Library (for PolyML)
KidkArolis/cherrytree-for-react 5
Seamlessly use cherrytree router with React
KidkArolis/cherrytree-redux-react-example 3
A copy of emmenko/redux-react-router-async-example where react-router is replaced with cherrytree
modular JavaScript utilities written in the AMD format
KidkArolis/backbone-bindings 1
Bi-directional bindings between Backbone.View elements and Backbone.Model attributes.
Estimate the size of a package by browserifying it, uglifying and gzipping.
Tweaked combo of tj/deploy and mafintosh/taco-nginx
Stateful, hierarchical router for single page applications
npm in the browser
issue commenthumaans/figbird
Invalid Query Parameter - `useFind` affects `useMutation` methods
Do I understand correctly that using refetch only caches locally to that component, so that cache would be cleared each time it is unmounted?
The refetch mode uses the same cache, so things will stick around forever in cache. Cache control / eviction is something I'm yet to add to this library. I was thinking about manual (you pick what to remove when), unmount (remove on unmount), ttl (remove on unmount after some delay). Caching is nice, because the way it currently works is if you revisit the same page with the same useFinds, you immediately see the data (and it gets refetched in the background) and it usually is the up to date data since it's updating in the background when realtime events come in (!).
Yeah, search is definitely an interesting use case in that it can be highly dynamic (generating many cache entries). One option would indeed be to do it outside figbird, why not. Another option would be go into internals and delete cache manually (scary :D). Yeah, I'll keep this issue open for a while as a reminder to think about these things.

comment created time in 20 hours
issue commenthumaans/figbird
Invalid Query Parameter - `useFind` affects `useMutation` methods
At the core, the issue is that $like is not part of standard Feathers operators, and is also not supported out of the box by figbird or sift - the underlying library used for client side query matching.
To answer you question of why useMutation and useFind are dependant and have an effect on each other - that's because in figbird useFind and useGet are "live queries". This is what happens in more detail:
useMutationis used to create an item- this immediately triggers a "cache" update in all
useGetanduseFindqueries currently being used or used in the past - this cache update is done to see if any of these queries should include the newly created item
- this is done by matching the newly created item against the query passed to
useFind - this works out of the box with any of the "standard" Feathers operators: $in, $nin, $lt, $lte, $gt, $gte, $ne, $or
The same behaviour happens with update/remove, not just create. The same happens when Feathers server sends realtime events, so this live query behaviour works not only when you create something locally, but also if other users / devices / tabs create something and the app receives a realtime event.
I hope that makes sense so far.
The issue is that you used $like which works on the server, because the feathers-objection plugin implements it and other extra operators. I thought this would be relatively easy to fix, but unfortunately, sift, which is used client side for query matching does not support $like out of the box, so the code to add this extra operator is a bit involved: https://github.com/robbyphillips/figbird-issue/pull/1/files
Another approach could be to opt out of the default realtime: 'merge' live query behaviour and instead use realtime: 'refetch'. This would not run query matching client side and would avoid the need to re-implement operators. Instead this would refetch any mounted queries when things are created/updated/removed: https://github.com/robbyphillips/figbird-issue/pull/2/files. Note, this doesn't work in this example repo, because it does not emit realtime events from what I could see. This means that when you create items, the list in the UI will not automagically update (because currently there are no realtime effects getting sent by the server).
There is another issue this example pointed out, although, perhaps not new - you implemented a useFind with a dynamic $like query that gets updated on every key press. This creates many queries in cache that currently don't ever get deleted by figbird, this will work ok, but if users typed many search queries that would inevitably lead to cache getting bloated and slow things down. I think that is something that would get solved once I get around adding cache eviction control/policies.
comment created time in 2 days
PR opened robbyphillips/figbird-issue
However, note that this example repo does not emit realtime events so actually what happens in this particular example, is that when new things are being created, the list won't update and the search results won't be refetched
pr created time in 2 days
push eventKidkArolis/figbird-issue
commit sha 6829fa79ebc6b06e9e8f6789058b4636db3f74a5
Make the demo app work with the $like operator
push time in 2 days
Simple repo to reproduce an issue for figbird
fork in 2 days
push eventKidkArolis/jetpack
commit sha 82f076b5084de664cd0afedf35a5fb95b2f0c921
0.20.0-0
push time in 19 days
push eventKidkArolis/jetpack
commit sha 4ff5a3ef3ab25530ddb5de06aa7ab64789d0d90c
Upgrade all the things
push time in 19 days
push eventhumaans/next-img
commit sha 384581fbd75531410026d0d1e220e2edf01287cc
Create codeql-analysis.yml
push time in 20 days
issue closedhumaans/next-img
Error: Missing an optimised image. Make sure to rerun next-img.
Hey!
I've run into an issue. I had an image (hero.jpg) which I've modified later. And from that point, I can't build or deploy my app to Vercel, because it responds every time with this error:
Error: Missing an optimised image hero-2160-b8e9d34d1c7f658b0b2de7e82f64b291.jpg. Make sure to rerun next-img.
It works perfectly on dev. But when deploying to Vercel or building locally:
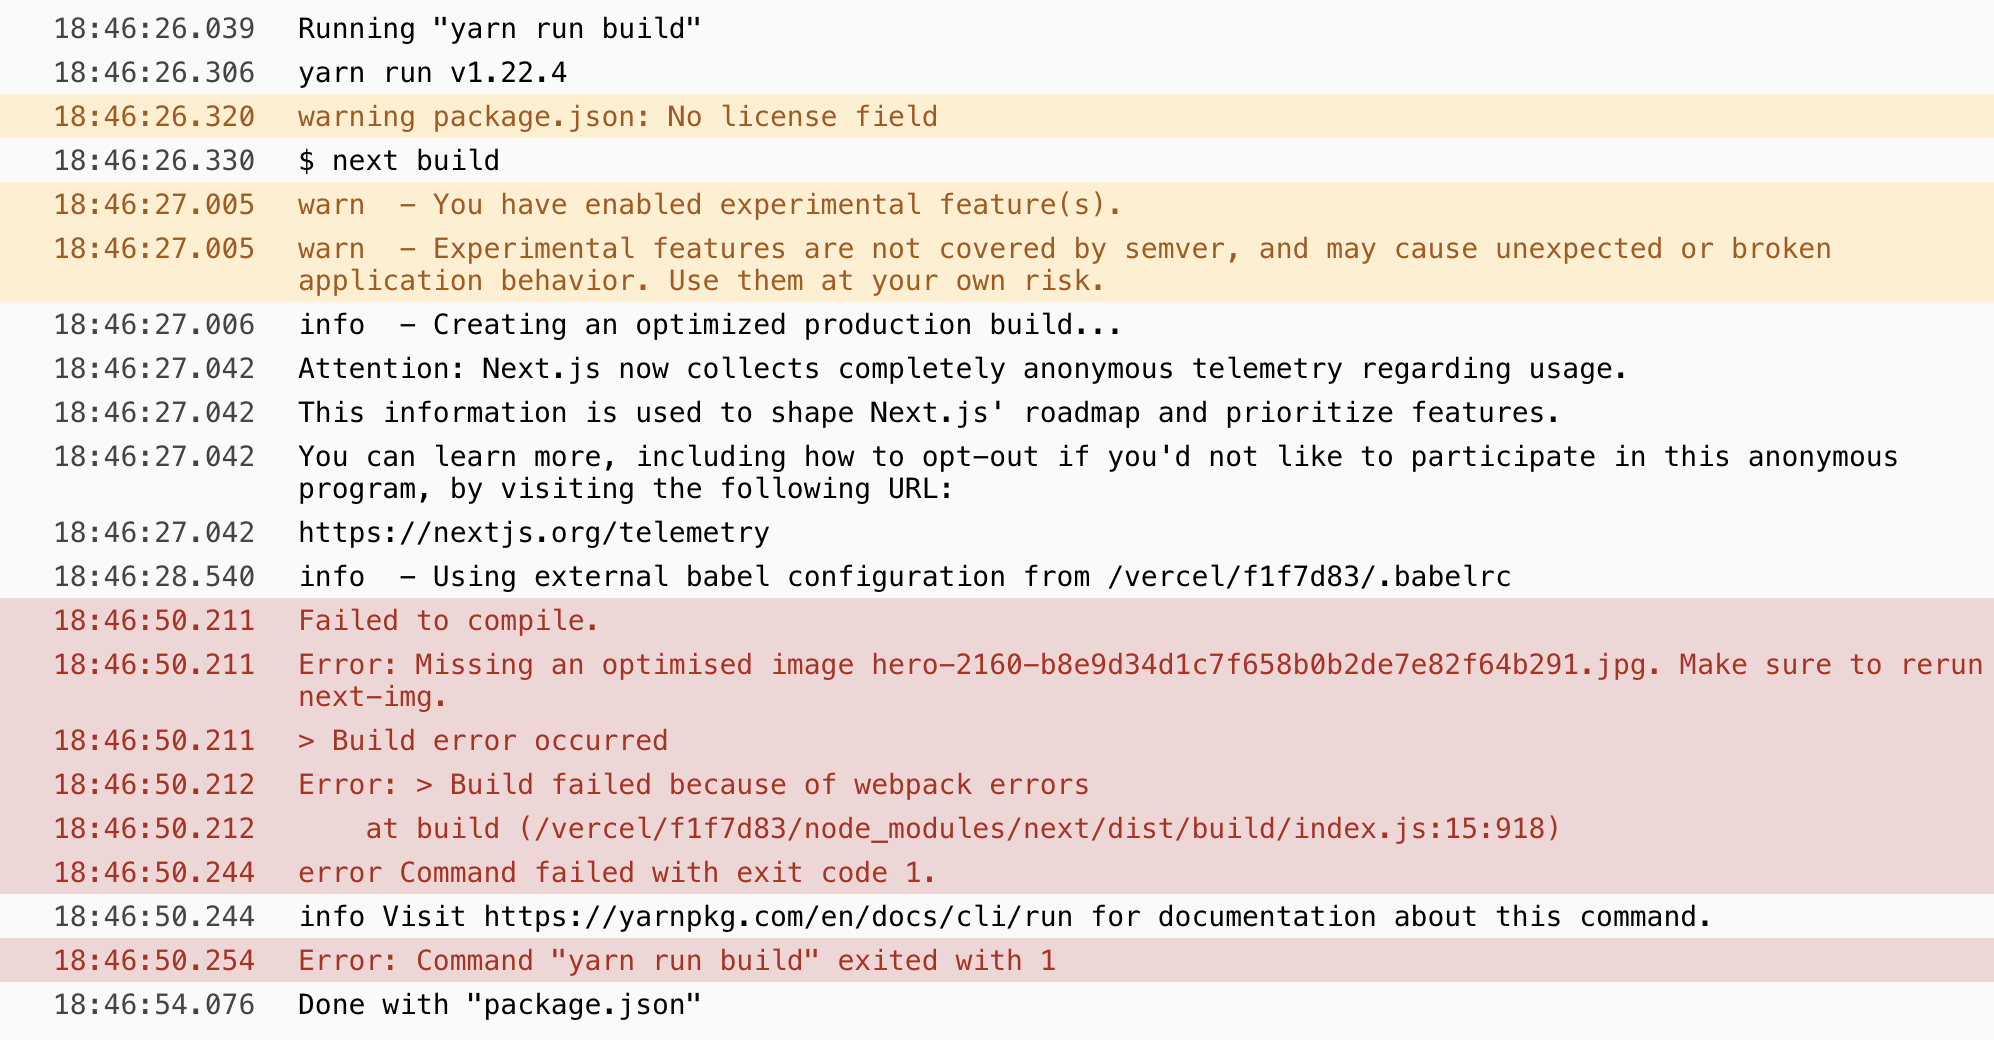
If I run npx next-img I get this result:
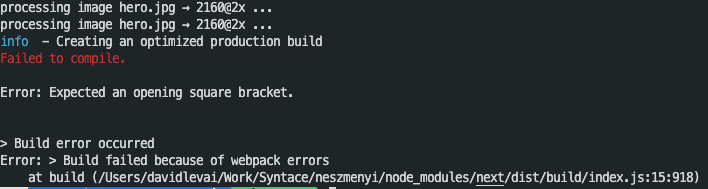
What do you think? Am I missing something?
(When opting out from persistent caching, it works with persistentCache: false,)
closed time in 23 days
DLevai94
issue commenthumaans/next-img
Error: Missing an optimised image. Make sure to rerun next-img.
Sorry for the late reply. In case this is useful, this seems to me that the optimized images have not been check in into the repo. When you run next locally, the plugin will output the images to resources, if that's not in the git repo, a CI / Vercel build will fail, because those images are not there and the plugin explicitly doesn't rebuild them, unless persistentCache is set to false.
comment created time in 23 days
startedchaifeng/ufw-docker
started time in a month
push eventKidkArolis/jetpack
commit sha fa5a837501c966cc5e1a96a71650ad3db5643770
0.19.0
push time in a month
push eventKidkArolis/jetpack
commit sha e72ad4aa55ca75535d3f0da862f27a8157139d2f
Upgrade all deps
commit sha 7a5bda0091853cb269a624f5fbaac2fc6e437030
Default to fast-refresh for React reloading
commit sha fed2eeaf87eef0773c157598892f42031d336200
0.19.0-alpha.0
commit sha 07c908f1650c28ca8040ebdc04a5749786f4b25b
Fix the react-refresh plugin installation
commit sha 6db4e54747fb8b54a0e538c336b6ee61a9f0c4dd
0.19.0-alpha.1
commit sha 6fcee8beae873794faf365dacd5fdf4505fa5a13
Upgrade deps
push time in a month
PR closed KidkArolis/jetpack
Bumps serve from 10.0.2 to 10.1.2. <details> <summary>Release notes</summary> <p><em>Sourced from <a href="https://github.com/zeit/serve/releases">serve's releases</a>.</em></p> <blockquote> <h2>10.1.2</h2> <h3>Patches</h3> <ul> <li>Use os.networkInterfaces() to detect network address: <a href="https://github-redirect.dependabot.com/zeit/serve/issues/492">#492</a></li> <li>Bumped <code>serve-handler</code> to latest version: <a href="https://github-redirect.dependabot.com/zeit/serve/issues/505">#505</a></li> </ul> <h3>Credits</h3> <p>Huge thanks to <a href="https://github.com/saintwinkle">@saintwinkle</a> for helping!</p> <h2>10.1.1</h2> <h3>Patches</h3> <ul> <li>Properly encode redirect responses: <a href="https://github-redirect.dependabot.com/zeit/serve/issues/491">#491</a></li> </ul> <h2>10.1.0</h2> <h3>Minor Changes</h3> <ul> <li>Added support for compression: <a href="https://github-redirect.dependabot.com/zeit/serve/issues/487">#487</a></li> <li>Added <code>NO_UPDATE_CHECK</code> environment flag: <a href="https://github-redirect.dependabot.com/zeit/serve/issues/457">#457</a></li> <li>Brought back support for ephemeral port switching: <a href="https://github-redirect.dependabot.com/zeit/serve/issues/490">#490</a></li> </ul> <h3>Patches</h3> <ul> <li>Bumped <code>serve-handler</code> to the latest version: <a href="https://github-redirect.dependabot.com/zeit/serve/issues/488">#488</a></li> <li>Deprecate support for <code>now.json</code> and <code>package.json</code>: <a href="https://github-redirect.dependabot.com/zeit/serve/issues/489">#489</a></li> </ul> <h3>Credits</h3> <p>Huge thanks to <a href="https://github.com/leeyeh">@leeyeh</a> for helping!</p> </blockquote> </details> <details> <summary>Commits</summary> <ul> <li><a href="https://github.com/vercel/serve/commit/73206336971c38e9f4867dc8cd88f95bd996f37d"><code>7320633</code></a> 10.1.2</li> <li><a href="https://github.com/vercel/serve/commit/7a939b635c83b4551214c171b46367ce5c375d0f"><code>7a939b6</code></a> Bumped <code>serve-handler</code> to latest version (<a href="https://github-redirect.dependabot.com/zeit/serve/issues/505">#505</a>)</li> <li><a href="https://github.com/vercel/serve/commit/b7d9de3f647c78c581d8e9a6d33d4b63ab9cdbfb"><code>b7d9de3</code></a> Use os.networkInterfaces() to detect network address (<a href="https://github-redirect.dependabot.com/zeit/serve/issues/492">#492</a>)</li> <li><a href="https://github.com/vercel/serve/commit/f799412e41723a320368b9190e14903c02de61e9"><code>f799412</code></a> 10.1.1</li> <li><a href="https://github.com/vercel/serve/commit/2136e13f883f5ac65d144df4defabb737a9f74e7"><code>2136e13</code></a> Properly encode redirect responses (<a href="https://github-redirect.dependabot.com/zeit/serve/issues/491">#491</a>)</li> <li><a href="https://github.com/vercel/serve/commit/fa4a460646758629df77ea3de37523d59b51548b"><code>fa4a460</code></a> 10.1.0</li> <li><a href="https://github.com/vercel/serve/commit/f8439ae8ac6c90c2bf5efdbcee3ca2eb87538372"><code>f8439ae</code></a> Brought back support for ephemeral port switching (<a href="https://github-redirect.dependabot.com/zeit/serve/issues/490">#490</a>)</li> <li><a href="https://github.com/vercel/serve/commit/596ae27185e1e22651f9fc0e6b6d51b8e27f6dd5"><code>596ae27</code></a> Deprecate support for <code>now.json</code> and <code>package.json</code> (<a href="https://github-redirect.dependabot.com/zeit/serve/issues/489">#489</a>)</li> <li><a href="https://github.com/vercel/serve/commit/96f840cb3fadfa4026a2b39dc95b545378992b05"><code>96f840c</code></a> Bumped <code>serve-handler</code> to the latest version (<a href="https://github-redirect.dependabot.com/zeit/serve/issues/488">#488</a>)</li> <li><a href="https://github.com/vercel/serve/commit/229a78c879a16ddc51357cc90aef85b43398b549"><code>229a78c</code></a> Added <code>NO_UPDATE_CHECK</code> environment flag (<a href="https://github-redirect.dependabot.com/zeit/serve/issues/457">#457</a>)</li> <li>Additional commits viewable in <a href="https://github.com/zeit/serve/compare/10.0.2...10.1.2">compare view</a></li> </ul> </details> <br />
Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting @dependabot rebase.
<details> <summary>Dependabot commands and options</summary> <br />
You can trigger Dependabot actions by commenting on this PR:
@dependabot rebasewill rebase this PR@dependabot recreatewill recreate this PR, overwriting any edits that have been made to it@dependabot mergewill merge this PR after your CI passes on it@dependabot squash and mergewill squash and merge this PR after your CI passes on it@dependabot cancel mergewill cancel a previously requested merge and block automerging@dependabot reopenwill reopen this PR if it is closed@dependabot closewill close this PR and stop Dependabot recreating it. You can achieve the same result by closing it manually@dependabot ignore this major versionwill close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself)@dependabot ignore this minor versionwill close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself)@dependabot ignore this dependencywill close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself)@dependabot use these labelswill set the current labels as the default for future PRs for this repo and language@dependabot use these reviewerswill set the current reviewers as the default for future PRs for this repo and language@dependabot use these assigneeswill set the current assignees as the default for future PRs for this repo and language@dependabot use this milestonewill set the current milestone as the default for future PRs for this repo and language
You can disable automated security fix PRs for this repo from the Security Alerts page.
</details>

pr closed time in a month
PR closed KidkArolis/jetpack
Bumps serve from 10.0.2 to 10.1.2. <details> <summary>Release notes</summary> <p><em>Sourced from <a href="https://github.com/zeit/serve/releases">serve's releases</a>.</em></p> <blockquote> <h2>10.1.2</h2> <h3>Patches</h3> <ul> <li>Use os.networkInterfaces() to detect network address: <a href="https://github-redirect.dependabot.com/zeit/serve/issues/492">#492</a></li> <li>Bumped <code>serve-handler</code> to latest version: <a href="https://github-redirect.dependabot.com/zeit/serve/issues/505">#505</a></li> </ul> <h3>Credits</h3> <p>Huge thanks to <a href="https://github.com/saintwinkle">@saintwinkle</a> for helping!</p> <h2>10.1.1</h2> <h3>Patches</h3> <ul> <li>Properly encode redirect responses: <a href="https://github-redirect.dependabot.com/zeit/serve/issues/491">#491</a></li> </ul> <h2>10.1.0</h2> <h3>Minor Changes</h3> <ul> <li>Added support for compression: <a href="https://github-redirect.dependabot.com/zeit/serve/issues/487">#487</a></li> <li>Added <code>NO_UPDATE_CHECK</code> environment flag: <a href="https://github-redirect.dependabot.com/zeit/serve/issues/457">#457</a></li> <li>Brought back support for ephemeral port switching: <a href="https://github-redirect.dependabot.com/zeit/serve/issues/490">#490</a></li> </ul> <h3>Patches</h3> <ul> <li>Bumped <code>serve-handler</code> to the latest version: <a href="https://github-redirect.dependabot.com/zeit/serve/issues/488">#488</a></li> <li>Deprecate support for <code>now.json</code> and <code>package.json</code>: <a href="https://github-redirect.dependabot.com/zeit/serve/issues/489">#489</a></li> </ul> <h3>Credits</h3> <p>Huge thanks to <a href="https://github.com/leeyeh">@leeyeh</a> for helping!</p> </blockquote> </details> <details> <summary>Commits</summary> <ul> <li><a href="https://github.com/vercel/serve/commit/73206336971c38e9f4867dc8cd88f95bd996f37d"><code>7320633</code></a> 10.1.2</li> <li><a href="https://github.com/vercel/serve/commit/7a939b635c83b4551214c171b46367ce5c375d0f"><code>7a939b6</code></a> Bumped <code>serve-handler</code> to latest version (<a href="https://github-redirect.dependabot.com/zeit/serve/issues/505">#505</a>)</li> <li><a href="https://github.com/vercel/serve/commit/b7d9de3f647c78c581d8e9a6d33d4b63ab9cdbfb"><code>b7d9de3</code></a> Use os.networkInterfaces() to detect network address (<a href="https://github-redirect.dependabot.com/zeit/serve/issues/492">#492</a>)</li> <li><a href="https://github.com/vercel/serve/commit/f799412e41723a320368b9190e14903c02de61e9"><code>f799412</code></a> 10.1.1</li> <li><a href="https://github.com/vercel/serve/commit/2136e13f883f5ac65d144df4defabb737a9f74e7"><code>2136e13</code></a> Properly encode redirect responses (<a href="https://github-redirect.dependabot.com/zeit/serve/issues/491">#491</a>)</li> <li><a href="https://github.com/vercel/serve/commit/fa4a460646758629df77ea3de37523d59b51548b"><code>fa4a460</code></a> 10.1.0</li> <li><a href="https://github.com/vercel/serve/commit/f8439ae8ac6c90c2bf5efdbcee3ca2eb87538372"><code>f8439ae</code></a> Brought back support for ephemeral port switching (<a href="https://github-redirect.dependabot.com/zeit/serve/issues/490">#490</a>)</li> <li><a href="https://github.com/vercel/serve/commit/596ae27185e1e22651f9fc0e6b6d51b8e27f6dd5"><code>596ae27</code></a> Deprecate support for <code>now.json</code> and <code>package.json</code> (<a href="https://github-redirect.dependabot.com/zeit/serve/issues/489">#489</a>)</li> <li><a href="https://github.com/vercel/serve/commit/96f840cb3fadfa4026a2b39dc95b545378992b05"><code>96f840c</code></a> Bumped <code>serve-handler</code> to the latest version (<a href="https://github-redirect.dependabot.com/zeit/serve/issues/488">#488</a>)</li> <li><a href="https://github.com/vercel/serve/commit/229a78c879a16ddc51357cc90aef85b43398b549"><code>229a78c</code></a> Added <code>NO_UPDATE_CHECK</code> environment flag (<a href="https://github-redirect.dependabot.com/zeit/serve/issues/457">#457</a>)</li> <li>Additional commits viewable in <a href="https://github.com/zeit/serve/compare/10.0.2...10.1.2">compare view</a></li> </ul> </details> <br />
Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting @dependabot rebase.
<details> <summary>Dependabot commands and options</summary> <br />
You can trigger Dependabot actions by commenting on this PR:
@dependabot rebasewill rebase this PR@dependabot recreatewill recreate this PR, overwriting any edits that have been made to it@dependabot mergewill merge this PR after your CI passes on it@dependabot squash and mergewill squash and merge this PR after your CI passes on it@dependabot cancel mergewill cancel a previously requested merge and block automerging@dependabot reopenwill reopen this PR if it is closed@dependabot closewill close this PR and stop Dependabot recreating it. You can achieve the same result by closing it manually@dependabot ignore this major versionwill close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself)@dependabot ignore this minor versionwill close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself)@dependabot ignore this dependencywill close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself)@dependabot use these labelswill set the current labels as the default for future PRs for this repo and language@dependabot use these reviewerswill set the current reviewers as the default for future PRs for this repo and language@dependabot use these assigneeswill set the current assignees as the default for future PRs for this repo and language@dependabot use this milestonewill set the current milestone as the default for future PRs for this repo and language
You can disable automated security fix PRs for this repo from the Security Alerts page.
</details>
pr closed time in a month
PR closed KidkArolis/jetpack
Bumps fastify from 1.13.0 to 2.15.1. <details> <summary>Release notes</summary> <p><em>Sourced from <a href="https://github.com/fastify/fastify/releases">fastify's releases</a>.</em></p> <blockquote> <h2>v2.15.1</h2> <h2>Breaking Change</h2> <p>For security reasons we changed the default in the <code>ajv</code>configuration. Unfortunately <code>allErrors: true</code> is a DoS attack vector for certain schemas. So this changed to <code>allErrors: false</code>.</p> <p>See: ajv-validator/ajv@334071a Ref: <a href="https://hackerone.com/reports/903521">https://hackerone.com/reports/903521</a></p> <h2>📚 PR:</h2> <ul> <li>Add <code>PATCH</code> to <code>body</code> validation (<a href="https://github-redirect.dependabot.com/fastify/fastify/issues/2351">#2351</a>)</li> </ul> <h2>v2.15.0</h2> <p>📚 PR:</p> <ul> <li>Bind error handler to instance (v2) (<a href="https://github-redirect.dependabot.com/fastify/fastify/issues/2305">#2305</a>)</li> <li>Fix custom JSON support (<a href="https://github-redirect.dependabot.com/fastify/fastify/issues/2309">#2309</a>)</li> <li>On ready backport (<a href="https://github-redirect.dependabot.com/fastify/fastify/issues/2296">#2296</a>)</li> </ul> <h2>v2.14.1</h2> <ul> <li>Tweak haproxy config for issue <a href="https://github-redirect.dependabot.com/fastify/fastify/issues/2036">#2036</a> (<a href="https://github-redirect.dependabot.com/fastify/fastify/issues/2270">#2270</a>) (<a href="https://github-redirect.dependabot.com/fastify/fastify/issues/2271">#2271</a>)</li> <li>Fix: call preHandler on reply.callNotFound (<a href="https://github-redirect.dependabot.com/fastify/fastify/issues/2256">#2256</a>) (<a href="https://github-redirect.dependabot.com/fastify/fastify/issues/2264">#2264</a>)</li> <li>doc: doc example to use ajv-errors (<a href="https://github-redirect.dependabot.com/fastify/fastify/issues/2254">#2254</a>)</li> <li>Log clientError as trace to avoid dev confusion (<a href="https://github-redirect.dependabot.com/fastify/fastify/issues/2241">#2241</a>) (<a href="https://github-redirect.dependabot.com/fastify/fastify/issues/2242">#2242</a>)</li> </ul> <h2>v2.14.0</h2> <p>📚 PR:</p> <ul> <li>Support builder-style injection (<a href="https://github-redirect.dependabot.com/fastify/fastify/issues/2209">#2209</a>)</li> <li>fix <a href="https://github-redirect.dependabot.com/fastify/fastify/issues/2214">#2214</a> (<a href="https://github-redirect.dependabot.com/fastify/fastify/issues/2218">#2218</a>)</li> <li>http2: fix HEAD requests hanging (<a href="https://github-redirect.dependabot.com/fastify/fastify/issues/2233">#2233</a>) (<a href="https://github-redirect.dependabot.com/fastify/fastify/issues/2239">#2239</a>)</li> </ul> <h2>v2.13.1</h2> <p>📚 PR:</p> <ul> <li>Ignore pino@6.</li> <li>ignore fast-json-stringify in dependabot</li> <li>Fix link to Fastify Create (<a href="https://github-redirect.dependabot.com/fastify/fastify/issues/2146">#2146</a>)</li> <li>test for issue <a href="https://github-redirect.dependabot.com/fastify/fastify/issues/2148">#2148</a> where typedefs for query params object were wrong (<a href="https://github-redirect.dependabot.com/fastify/fastify/issues/2149">#2149</a>)</li> <li>Replace greenkeeper with dependabot (<a href="https://github-redirect.dependabot.com/fastify/fastify/issues/2162">#2162</a>)</li> <li>add fastify-method-override to ecosystem (<a href="https://github-redirect.dependabot.com/fastify/fastify/issues/2165">#2165</a>)</li> <li>Update Logging.md (<a href="https://github-redirect.dependabot.com/fastify/fastify/issues/2171">#2171</a>)</li> <li>Add to fastify-qrcode into Ecosystem (<a href="https://github-redirect.dependabot.com/fastify/fastify/issues/2170">#2170</a>)</li> <li>docs: errors in async hook (<a href="https://github-redirect.dependabot.com/fastify/fastify/issues/2176">#2176</a>)</li> <li>docs: use direct references in the "Schema Resolver" example (<a href="https://github-redirect.dependabot.com/fastify/fastify/issues/2155">#2155</a>)</li> <li>fix: typo in routes doc (<a href="https://github-redirect.dependabot.com/fastify/fastify/issues/2182">#2182</a>)</li> <li>Add google cloud trace API plugin (<a href="https://github-redirect.dependabot.com/fastify/fastify/issues/2185">#2185</a>)</li> <li>Fixes crash when using a non-standard error code (<a href="https://github-redirect.dependabot.com/fastify/fastify/issues/2184">#2184</a>)</li> <li>Fix package-manager CI (<a href="https://github-redirect.dependabot.com/fastify/fastify/issues/2189">#2189</a>)</li> </ul> <!-- raw HTML omitted --> </blockquote> </details> <details> <summary>Commits</summary> <ul> <li><a href="https://github.com/fastify/fastify/commit/2cfe0df1682f293becfcb435469befd0c470603e"><code>2cfe0df</code></a> Bumped v2.15.1</li> <li><a href="https://github.com/fastify/fastify/commit/74c3157ca90c3ffed9e4434f63c2017471ec970e"><code>74c3157</code></a> Disable allErrors in default Ajv config.</li> <li><a href="https://github.com/fastify/fastify/commit/854e150c0d78e7c31f4f6eca57908f9da19c379f"><code>854e150</code></a> Revert "correct typings for ready() (<a href="https://github-redirect.dependabot.com/fastify/fastify/issues/2345">#2345</a>)"</li> <li><a href="https://github.com/fastify/fastify/commit/6de894352871089027a3b4b29bed3012520c4579"><code>6de8943</code></a> Add <code>PATCH</code> to <code>body</code> validation (<a href="https://github-redirect.dependabot.com/fastify/fastify/issues/2351">#2351</a>)</li> <li><a href="https://github.com/fastify/fastify/commit/65d0e5b15769f67881c37aed8d84b802adf44106"><code>65d0e5b</code></a> correct typings for ready() (<a href="https://github-redirect.dependabot.com/fastify/fastify/issues/2345">#2345</a>)</li> <li><a href="https://github.com/fastify/fastify/commit/fd94ad3bf4bb1c415a92ecf89ee6f4f038448c39"><code>fd94ad3</code></a> Bumped v2.15.0</li> <li><a href="https://github.com/fastify/fastify/commit/655f28fcc36679b4538e0120eecb1f5524325298"><code>655f28f</code></a> On ready backport (<a href="https://github-redirect.dependabot.com/fastify/fastify/issues/2296">#2296</a>)</li> <li><a href="https://github.com/fastify/fastify/commit/12fa71451237e7db202afe1235977cd34e7d8d71"><code>12fa714</code></a> Fix custom JSON support (<a href="https://github-redirect.dependabot.com/fastify/fastify/issues/2309">#2309</a>)</li> <li><a href="https://github.com/fastify/fastify/commit/39e23753240eb18d4f86af736c65e192b4071248"><code>39e2375</code></a> Bind error handler to instance (v2) (<a href="https://github-redirect.dependabot.com/fastify/fastify/issues/2305">#2305</a>)</li> <li><a href="https://github.com/fastify/fastify/commit/6b0ffc6672fb2bf4ba8e4337958c5ee46e6e0300"><code>6b0ffc6</code></a> Bumped v2.14.1</li> <li>Additional commits viewable in <a href="https://github.com/fastify/fastify/compare/v1.13.0...v2.15.1">compare view</a></li> </ul> </details> <br />
Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting @dependabot rebase.
<details> <summary>Dependabot commands and options</summary> <br />
You can trigger Dependabot actions by commenting on this PR:
@dependabot rebasewill rebase this PR@dependabot recreatewill recreate this PR, overwriting any edits that have been made to it@dependabot mergewill merge this PR after your CI passes on it@dependabot squash and mergewill squash and merge this PR after your CI passes on it@dependabot cancel mergewill cancel a previously requested merge and block automerging@dependabot reopenwill reopen this PR if it is closed@dependabot closewill close this PR and stop Dependabot recreating it. You can achieve the same result by closing it manually@dependabot ignore this major versionwill close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself)@dependabot ignore this minor versionwill close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself)@dependabot ignore this dependencywill close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself)@dependabot use these labelswill set the current labels as the default for future PRs for this repo and language@dependabot use these reviewerswill set the current reviewers as the default for future PRs for this repo and language@dependabot use these assigneeswill set the current assignees as the default for future PRs for this repo and language@dependabot use this milestonewill set the current milestone as the default for future PRs for this repo and language
You can disable automated security fix PRs for this repo from the Security Alerts page.
</details>
pr closed time in a month
PR closed KidkArolis/jetpack
Bumps elliptic from 6.5.2 to 6.5.3. <details> <summary>Commits</summary> <ul> <li><a href="https://github.com/indutny/elliptic/commit/8647803dc3d90506aa03021737f7b061ba959ae1"><code>8647803</code></a> 6.5.3</li> <li><a href="https://github.com/indutny/elliptic/commit/856fe4d99fe7b6200556e6400b3bf585b1721bec"><code>856fe4d</code></a> signature: prevent malleability and overflows</li> <li>See full diff in <a href="https://github.com/indutny/elliptic/compare/v6.5.2...v6.5.3">compare view</a></li> </ul> </details> <br />
Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting @dependabot rebase.
<details> <summary>Dependabot commands and options</summary> <br />
You can trigger Dependabot actions by commenting on this PR:
@dependabot rebasewill rebase this PR@dependabot recreatewill recreate this PR, overwriting any edits that have been made to it@dependabot mergewill merge this PR after your CI passes on it@dependabot squash and mergewill squash and merge this PR after your CI passes on it@dependabot cancel mergewill cancel a previously requested merge and block automerging@dependabot reopenwill reopen this PR if it is closed@dependabot closewill close this PR and stop Dependabot recreating it. You can achieve the same result by closing it manually@dependabot ignore this major versionwill close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself)@dependabot ignore this minor versionwill close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself)@dependabot ignore this dependencywill close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself)@dependabot use these labelswill set the current labels as the default for future PRs for this repo and language@dependabot use these reviewerswill set the current reviewers as the default for future PRs for this repo and language@dependabot use these assigneeswill set the current assignees as the default for future PRs for this repo and language@dependabot use this milestonewill set the current milestone as the default for future PRs for this repo and language
You can disable automated security fix PRs for this repo from the Security Alerts page.
</details>
pr closed time in a month
PR closed KidkArolis/jetpack
Bumps elliptic from 6.5.2 to 6.5.3. <details> <summary>Commits</summary> <ul> <li><a href="https://github.com/indutny/elliptic/commit/8647803dc3d90506aa03021737f7b061ba959ae1"><code>8647803</code></a> 6.5.3</li> <li><a href="https://github.com/indutny/elliptic/commit/856fe4d99fe7b6200556e6400b3bf585b1721bec"><code>856fe4d</code></a> signature: prevent malleability and overflows</li> <li>See full diff in <a href="https://github.com/indutny/elliptic/compare/v6.5.2...v6.5.3">compare view</a></li> </ul> </details> <br />
Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting @dependabot rebase.
<details> <summary>Dependabot commands and options</summary> <br />
You can trigger Dependabot actions by commenting on this PR:
@dependabot rebasewill rebase this PR@dependabot recreatewill recreate this PR, overwriting any edits that have been made to it@dependabot mergewill merge this PR after your CI passes on it@dependabot squash and mergewill squash and merge this PR after your CI passes on it@dependabot cancel mergewill cancel a previously requested merge and block automerging@dependabot reopenwill reopen this PR if it is closed@dependabot closewill close this PR and stop Dependabot recreating it. You can achieve the same result by closing it manually@dependabot ignore this major versionwill close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself)@dependabot ignore this minor versionwill close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself)@dependabot ignore this dependencywill close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself)@dependabot use these labelswill set the current labels as the default for future PRs for this repo and language@dependabot use these reviewerswill set the current reviewers as the default for future PRs for this repo and language@dependabot use these assigneeswill set the current assignees as the default for future PRs for this repo and language@dependabot use this milestonewill set the current milestone as the default for future PRs for this repo and language
You can disable automated security fix PRs for this repo from the Security Alerts page.
</details>
pr closed time in a month
PR closed KidkArolis/jetpack
Bumps lodash from 4.17.15 to 4.17.19. <details> <summary>Release notes</summary> <p><em>Sourced from <a href="https://github.com/lodash/lodash/releases">lodash's releases</a>.</em></p> <blockquote> <h2>4.17.16</h2> </blockquote> </details> <details> <summary>Commits</summary> <ul> <li><a href="https://github.com/lodash/lodash/commit/d7fbc52ee0466a6d248f047b5d5c3e6d1e099056"><code>d7fbc52</code></a> Bump to v4.17.19</li> <li><a href="https://github.com/lodash/lodash/commit/2e1c0f22f425e9c013815b2cd7c2ebd51f49a8d6"><code>2e1c0f2</code></a> Add npm-package</li> <li><a href="https://github.com/lodash/lodash/commit/1b6c282299f4e0271f932b466c67f0f822aa308e"><code>1b6c282</code></a> Bump to v4.17.18</li> <li><a href="https://github.com/lodash/lodash/commit/a370ac81408de2da77a82b3c4b61a01a3b9c2fac"><code>a370ac8</code></a> Bump to v4.17.17</li> <li><a href="https://github.com/lodash/lodash/commit/1144918f3578a84fcc4986da9b806e63a6175cbb"><code>1144918</code></a> Rebuild lodash and docs</li> <li><a href="https://github.com/lodash/lodash/commit/3a3b0fd339c2109563f7e8167dc95265ed82ef3e"><code>3a3b0fd</code></a> Bump to v4.17.16</li> <li><a href="https://github.com/lodash/lodash/commit/c84fe82760fb2d3e03a63379b297a1cc1a2fce12"><code>c84fe82</code></a> fix(zipObjectDeep): prototype pollution (<a href="https://github-redirect.dependabot.com/lodash/lodash/issues/4759">#4759</a>)</li> <li><a href="https://github.com/lodash/lodash/commit/e7b28ea6cb17b4ca021e7c9d66218c8c89782f32"><code>e7b28ea</code></a> Sanitize sourceURL so it cannot affect evaled code (<a href="https://github-redirect.dependabot.com/lodash/lodash/issues/4518">#4518</a>)</li> <li><a href="https://github.com/lodash/lodash/commit/0cec225778d4ac26c2bac95031ecc92a94f08bbb"><code>0cec225</code></a> Fix lodash.isEqual for circular references (<a href="https://github-redirect.dependabot.com/lodash/lodash/issues/4320">#4320</a>) (<a href="https://github-redirect.dependabot.com/lodash/lodash/issues/4515">#4515</a>)</li> <li><a href="https://github.com/lodash/lodash/commit/94c3a8133cb4fcdb50db72b4fd14dd884b195cd5"><code>94c3a81</code></a> Document matches* shorthands for over* methods (<a href="https://github-redirect.dependabot.com/lodash/lodash/issues/4510">#4510</a>) (<a href="https://github-redirect.dependabot.com/lodash/lodash/issues/4514">#4514</a>)</li> <li>Additional commits viewable in <a href="https://github.com/lodash/lodash/compare/4.17.15...4.17.19">compare view</a></li> </ul> </details> <details> <summary>Maintainer changes</summary> <p>This version was pushed to npm by <a href="https://www.npmjs.com/~mathias">mathias</a>, a new releaser for lodash since your current version.</p> </details> <br />
Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting @dependabot rebase.
<details> <summary>Dependabot commands and options</summary> <br />
You can trigger Dependabot actions by commenting on this PR:
@dependabot rebasewill rebase this PR@dependabot recreatewill recreate this PR, overwriting any edits that have been made to it@dependabot mergewill merge this PR after your CI passes on it@dependabot squash and mergewill squash and merge this PR after your CI passes on it@dependabot cancel mergewill cancel a previously requested merge and block automerging@dependabot reopenwill reopen this PR if it is closed@dependabot closewill close this PR and stop Dependabot recreating it. You can achieve the same result by closing it manually@dependabot ignore this major versionwill close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself)@dependabot ignore this minor versionwill close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself)@dependabot ignore this dependencywill close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself)@dependabot use these labelswill set the current labels as the default for future PRs for this repo and language@dependabot use these reviewerswill set the current reviewers as the default for future PRs for this repo and language@dependabot use these assigneeswill set the current assignees as the default for future PRs for this repo and language@dependabot use this milestonewill set the current milestone as the default for future PRs for this repo and language
You can disable automated security fix PRs for this repo from the Security Alerts page.
</details>
pr closed time in a month
PR closed KidkArolis/jetpack
Bumps lodash from 4.17.15 to 4.17.19. <details> <summary>Release notes</summary> <p><em>Sourced from <a href="https://github.com/lodash/lodash/releases">lodash's releases</a>.</em></p> <blockquote> <h2>4.17.16</h2> </blockquote> </details> <details> <summary>Commits</summary> <ul> <li><a href="https://github.com/lodash/lodash/commit/d7fbc52ee0466a6d248f047b5d5c3e6d1e099056"><code>d7fbc52</code></a> Bump to v4.17.19</li> <li><a href="https://github.com/lodash/lodash/commit/2e1c0f22f425e9c013815b2cd7c2ebd51f49a8d6"><code>2e1c0f2</code></a> Add npm-package</li> <li><a href="https://github.com/lodash/lodash/commit/1b6c282299f4e0271f932b466c67f0f822aa308e"><code>1b6c282</code></a> Bump to v4.17.18</li> <li><a href="https://github.com/lodash/lodash/commit/a370ac81408de2da77a82b3c4b61a01a3b9c2fac"><code>a370ac8</code></a> Bump to v4.17.17</li> <li><a href="https://github.com/lodash/lodash/commit/1144918f3578a84fcc4986da9b806e63a6175cbb"><code>1144918</code></a> Rebuild lodash and docs</li> <li><a href="https://github.com/lodash/lodash/commit/3a3b0fd339c2109563f7e8167dc95265ed82ef3e"><code>3a3b0fd</code></a> Bump to v4.17.16</li> <li><a href="https://github.com/lodash/lodash/commit/c84fe82760fb2d3e03a63379b297a1cc1a2fce12"><code>c84fe82</code></a> fix(zipObjectDeep): prototype pollution (<a href="https://github-redirect.dependabot.com/lodash/lodash/issues/4759">#4759</a>)</li> <li><a href="https://github.com/lodash/lodash/commit/e7b28ea6cb17b4ca021e7c9d66218c8c89782f32"><code>e7b28ea</code></a> Sanitize sourceURL so it cannot affect evaled code (<a href="https://github-redirect.dependabot.com/lodash/lodash/issues/4518">#4518</a>)</li> <li><a href="https://github.com/lodash/lodash/commit/0cec225778d4ac26c2bac95031ecc92a94f08bbb"><code>0cec225</code></a> Fix lodash.isEqual for circular references (<a href="https://github-redirect.dependabot.com/lodash/lodash/issues/4320">#4320</a>) (<a href="https://github-redirect.dependabot.com/lodash/lodash/issues/4515">#4515</a>)</li> <li><a href="https://github.com/lodash/lodash/commit/94c3a8133cb4fcdb50db72b4fd14dd884b195cd5"><code>94c3a81</code></a> Document matches* shorthands for over* methods (<a href="https://github-redirect.dependabot.com/lodash/lodash/issues/4510">#4510</a>) (<a href="https://github-redirect.dependabot.com/lodash/lodash/issues/4514">#4514</a>)</li> <li>Additional commits viewable in <a href="https://github.com/lodash/lodash/compare/4.17.15...4.17.19">compare view</a></li> </ul> </details> <details> <summary>Maintainer changes</summary> <p>This version was pushed to npm by <a href="https://www.npmjs.com/~mathias">mathias</a>, a new releaser for lodash since your current version.</p> </details> <br />
Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting @dependabot rebase.
<details> <summary>Dependabot commands and options</summary> <br />
You can trigger Dependabot actions by commenting on this PR:
@dependabot rebasewill rebase this PR@dependabot recreatewill recreate this PR, overwriting any edits that have been made to it@dependabot mergewill merge this PR after your CI passes on it@dependabot squash and mergewill squash and merge this PR after your CI passes on it@dependabot cancel mergewill cancel a previously requested merge and block automerging@dependabot reopenwill reopen this PR if it is closed@dependabot closewill close this PR and stop Dependabot recreating it. You can achieve the same result by closing it manually@dependabot ignore this major versionwill close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself)@dependabot ignore this minor versionwill close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself)@dependabot ignore this dependencywill close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself)@dependabot use these labelswill set the current labels as the default for future PRs for this repo and language@dependabot use these reviewerswill set the current reviewers as the default for future PRs for this repo and language@dependabot use these assigneeswill set the current assignees as the default for future PRs for this repo and language@dependabot use this milestonewill set the current milestone as the default for future PRs for this repo and language
You can disable automated security fix PRs for this repo from the Security Alerts page.
</details>
pr closed time in a month
PR closed KidkArolis/jetpack
Bumps lodash from 4.17.15 to 4.17.19. <details> <summary>Release notes</summary> <p><em>Sourced from <a href="https://github.com/lodash/lodash/releases">lodash's releases</a>.</em></p> <blockquote> <h2>4.17.16</h2> </blockquote> </details> <details> <summary>Commits</summary> <ul> <li><a href="https://github.com/lodash/lodash/commit/d7fbc52ee0466a6d248f047b5d5c3e6d1e099056"><code>d7fbc52</code></a> Bump to v4.17.19</li> <li><a href="https://github.com/lodash/lodash/commit/2e1c0f22f425e9c013815b2cd7c2ebd51f49a8d6"><code>2e1c0f2</code></a> Add npm-package</li> <li><a href="https://github.com/lodash/lodash/commit/1b6c282299f4e0271f932b466c67f0f822aa308e"><code>1b6c282</code></a> Bump to v4.17.18</li> <li><a href="https://github.com/lodash/lodash/commit/a370ac81408de2da77a82b3c4b61a01a3b9c2fac"><code>a370ac8</code></a> Bump to v4.17.17</li> <li><a href="https://github.com/lodash/lodash/commit/1144918f3578a84fcc4986da9b806e63a6175cbb"><code>1144918</code></a> Rebuild lodash and docs</li> <li><a href="https://github.com/lodash/lodash/commit/3a3b0fd339c2109563f7e8167dc95265ed82ef3e"><code>3a3b0fd</code></a> Bump to v4.17.16</li> <li><a href="https://github.com/lodash/lodash/commit/c84fe82760fb2d3e03a63379b297a1cc1a2fce12"><code>c84fe82</code></a> fix(zipObjectDeep): prototype pollution (<a href="https://github-redirect.dependabot.com/lodash/lodash/issues/4759">#4759</a>)</li> <li><a href="https://github.com/lodash/lodash/commit/e7b28ea6cb17b4ca021e7c9d66218c8c89782f32"><code>e7b28ea</code></a> Sanitize sourceURL so it cannot affect evaled code (<a href="https://github-redirect.dependabot.com/lodash/lodash/issues/4518">#4518</a>)</li> <li><a href="https://github.com/lodash/lodash/commit/0cec225778d4ac26c2bac95031ecc92a94f08bbb"><code>0cec225</code></a> Fix lodash.isEqual for circular references (<a href="https://github-redirect.dependabot.com/lodash/lodash/issues/4320">#4320</a>) (<a href="https://github-redirect.dependabot.com/lodash/lodash/issues/4515">#4515</a>)</li> <li><a href="https://github.com/lodash/lodash/commit/94c3a8133cb4fcdb50db72b4fd14dd884b195cd5"><code>94c3a81</code></a> Document matches* shorthands for over* methods (<a href="https://github-redirect.dependabot.com/lodash/lodash/issues/4510">#4510</a>) (<a href="https://github-redirect.dependabot.com/lodash/lodash/issues/4514">#4514</a>)</li> <li>Additional commits viewable in <a href="https://github.com/lodash/lodash/compare/4.17.15...4.17.19">compare view</a></li> </ul> </details> <details> <summary>Maintainer changes</summary> <p>This version was pushed to npm by <a href="https://www.npmjs.com/~mathias">mathias</a>, a new releaser for lodash since your current version.</p> </details> <br />
Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting @dependabot rebase.
<details> <summary>Dependabot commands and options</summary> <br />
You can trigger Dependabot actions by commenting on this PR:
@dependabot rebasewill rebase this PR@dependabot recreatewill recreate this PR, overwriting any edits that have been made to it@dependabot mergewill merge this PR after your CI passes on it@dependabot squash and mergewill squash and merge this PR after your CI passes on it@dependabot cancel mergewill cancel a previously requested merge and block automerging@dependabot reopenwill reopen this PR if it is closed@dependabot closewill close this PR and stop Dependabot recreating it. You can achieve the same result by closing it manually@dependabot ignore this major versionwill close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself)@dependabot ignore this minor versionwill close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself)@dependabot ignore this dependencywill close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself)@dependabot use these labelswill set the current labels as the default for future PRs for this repo and language@dependabot use these reviewerswill set the current reviewers as the default for future PRs for this repo and language@dependabot use these assigneeswill set the current assignees as the default for future PRs for this repo and language@dependabot use this milestonewill set the current milestone as the default for future PRs for this repo and language
You can disable automated security fix PRs for this repo from the Security Alerts page.
</details>
pr closed time in a month
PR closed KidkArolis/jetpack
Bumps minimist from 1.2.0 to 1.2.5. <details> <summary>Commits</summary> <ul> <li><a href="https://github.com/substack/minimist/commit/aeb3e27dae0412de5c0494e9563a5f10c82cc7a9"><code>aeb3e27</code></a> 1.2.5</li> <li><a href="https://github.com/substack/minimist/commit/278677b171d956b46613a158c6c486c3ef979b20"><code>278677b</code></a> 1.2.4</li> <li><a href="https://github.com/substack/minimist/commit/4cf1354839cb972e38496d35e12f806eea92c11f"><code>4cf1354</code></a> security notice</li> <li><a href="https://github.com/substack/minimist/commit/1043d212c3caaf871966e710f52cfdf02f9eea4b"><code>1043d21</code></a> additional test for constructor prototype pollution</li> <li><a href="https://github.com/substack/minimist/commit/6457d7440a47f329c12c4a5abfbce211c4235b93"><code>6457d74</code></a> 1.2.3</li> <li><a href="https://github.com/substack/minimist/commit/38a4d1caead72ef99e824bb420a2528eec03d9ab"><code>38a4d1c</code></a> even more aggressive checks for protocol pollution</li> <li><a href="https://github.com/substack/minimist/commit/13c01a5327736903704984b7f65616b8476850cc"><code>13c01a5</code></a> more failing proto pollution tests</li> <li><a href="https://github.com/substack/minimist/commit/f34df077a6b2bee1344188849a95e66777109e89"><code>f34df07</code></a> 1.2.2</li> <li><a href="https://github.com/substack/minimist/commit/67d3722413448d00a62963d2d30c34656a92d7e2"><code>67d3722</code></a> cleanup</li> <li><a href="https://github.com/substack/minimist/commit/63e7ed05aa4b1889ec2f3b196426db4500cbda94"><code>63e7ed0</code></a> don't assign onto <strong>proto</strong></li> <li>Additional commits viewable in <a href="https://github.com/substack/minimist/compare/1.2.0...1.2.5">compare view</a></li> </ul> </details> <br />
Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting @dependabot rebase.
<details> <summary>Dependabot commands and options</summary> <br />
You can trigger Dependabot actions by commenting on this PR:
@dependabot rebasewill rebase this PR@dependabot recreatewill recreate this PR, overwriting any edits that have been made to it@dependabot mergewill merge this PR after your CI passes on it@dependabot squash and mergewill squash and merge this PR after your CI passes on it@dependabot cancel mergewill cancel a previously requested merge and block automerging@dependabot reopenwill reopen this PR if it is closed@dependabot closewill close this PR and stop Dependabot recreating it. You can achieve the same result by closing it manually@dependabot ignore this major versionwill close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself)@dependabot ignore this minor versionwill close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself)@dependabot ignore this dependencywill close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself)@dependabot use these labelswill set the current labels as the default for future PRs for this repo and language@dependabot use these reviewerswill set the current reviewers as the default for future PRs for this repo and language@dependabot use these assigneeswill set the current assignees as the default for future PRs for this repo and language@dependabot use this milestonewill set the current milestone as the default for future PRs for this repo and language
You can disable automated security fix PRs for this repo from the Security Alerts page.
</details>
pr closed time in a month
PR closed KidkArolis/jetpack
Bumps minimist from 1.2.0 to 1.2.5. <details> <summary>Commits</summary> <ul> <li><a href="https://github.com/substack/minimist/commit/aeb3e27dae0412de5c0494e9563a5f10c82cc7a9"><code>aeb3e27</code></a> 1.2.5</li> <li><a href="https://github.com/substack/minimist/commit/278677b171d956b46613a158c6c486c3ef979b20"><code>278677b</code></a> 1.2.4</li> <li><a href="https://github.com/substack/minimist/commit/4cf1354839cb972e38496d35e12f806eea92c11f"><code>4cf1354</code></a> security notice</li> <li><a href="https://github.com/substack/minimist/commit/1043d212c3caaf871966e710f52cfdf02f9eea4b"><code>1043d21</code></a> additional test for constructor prototype pollution</li> <li><a href="https://github.com/substack/minimist/commit/6457d7440a47f329c12c4a5abfbce211c4235b93"><code>6457d74</code></a> 1.2.3</li> <li><a href="https://github.com/substack/minimist/commit/38a4d1caead72ef99e824bb420a2528eec03d9ab"><code>38a4d1c</code></a> even more aggressive checks for protocol pollution</li> <li><a href="https://github.com/substack/minimist/commit/13c01a5327736903704984b7f65616b8476850cc"><code>13c01a5</code></a> more failing proto pollution tests</li> <li><a href="https://github.com/substack/minimist/commit/f34df077a6b2bee1344188849a95e66777109e89"><code>f34df07</code></a> 1.2.2</li> <li><a href="https://github.com/substack/minimist/commit/67d3722413448d00a62963d2d30c34656a92d7e2"><code>67d3722</code></a> cleanup</li> <li><a href="https://github.com/substack/minimist/commit/63e7ed05aa4b1889ec2f3b196426db4500cbda94"><code>63e7ed0</code></a> don't assign onto <strong>proto</strong></li> <li>Additional commits viewable in <a href="https://github.com/substack/minimist/compare/1.2.0...1.2.5">compare view</a></li> </ul> </details> <br />
Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting @dependabot rebase.
<details> <summary>Dependabot commands and options</summary> <br />
You can trigger Dependabot actions by commenting on this PR:
@dependabot rebasewill rebase this PR@dependabot recreatewill recreate this PR, overwriting any edits that have been made to it@dependabot mergewill merge this PR after your CI passes on it@dependabot squash and mergewill squash and merge this PR after your CI passes on it@dependabot cancel mergewill cancel a previously requested merge and block automerging@dependabot reopenwill reopen this PR if it is closed@dependabot closewill close this PR and stop Dependabot recreating it. You can achieve the same result by closing it manually@dependabot ignore this major versionwill close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself)@dependabot ignore this minor versionwill close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself)@dependabot ignore this dependencywill close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself)@dependabot use these labelswill set the current labels as the default for future PRs for this repo and language@dependabot use these reviewerswill set the current reviewers as the default for future PRs for this repo and language@dependabot use these assigneeswill set the current assignees as the default for future PRs for this repo and language@dependabot use this milestonewill set the current milestone as the default for future PRs for this repo and language
You can disable automated security fix PRs for this repo from the Security Alerts page.
</details>
pr closed time in a month
PR closed KidkArolis/jetpack
Bumps minimist from 1.2.0 to 1.2.5. <details> <summary>Commits</summary> <ul> <li><a href="https://github.com/substack/minimist/commit/aeb3e27dae0412de5c0494e9563a5f10c82cc7a9"><code>aeb3e27</code></a> 1.2.5</li> <li><a href="https://github.com/substack/minimist/commit/278677b171d956b46613a158c6c486c3ef979b20"><code>278677b</code></a> 1.2.4</li> <li><a href="https://github.com/substack/minimist/commit/4cf1354839cb972e38496d35e12f806eea92c11f"><code>4cf1354</code></a> security notice</li> <li><a href="https://github.com/substack/minimist/commit/1043d212c3caaf871966e710f52cfdf02f9eea4b"><code>1043d21</code></a> additional test for constructor prototype pollution</li> <li><a href="https://github.com/substack/minimist/commit/6457d7440a47f329c12c4a5abfbce211c4235b93"><code>6457d74</code></a> 1.2.3</li> <li><a href="https://github.com/substack/minimist/commit/38a4d1caead72ef99e824bb420a2528eec03d9ab"><code>38a4d1c</code></a> even more aggressive checks for protocol pollution</li> <li><a href="https://github.com/substack/minimist/commit/13c01a5327736903704984b7f65616b8476850cc"><code>13c01a5</code></a> more failing proto pollution tests</li> <li><a href="https://github.com/substack/minimist/commit/f34df077a6b2bee1344188849a95e66777109e89"><code>f34df07</code></a> 1.2.2</li> <li><a href="https://github.com/substack/minimist/commit/67d3722413448d00a62963d2d30c34656a92d7e2"><code>67d3722</code></a> cleanup</li> <li><a href="https://github.com/substack/minimist/commit/63e7ed05aa4b1889ec2f3b196426db4500cbda94"><code>63e7ed0</code></a> don't assign onto <strong>proto</strong></li> <li>Additional commits viewable in <a href="https://github.com/substack/minimist/compare/1.2.0...1.2.5">compare view</a></li> </ul> </details> <br />
Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting @dependabot rebase.
<details> <summary>Dependabot commands and options</summary> <br />
You can trigger Dependabot actions by commenting on this PR:
@dependabot rebasewill rebase this PR@dependabot recreatewill recreate this PR, overwriting any edits that have been made to it@dependabot mergewill merge this PR after your CI passes on it@dependabot squash and mergewill squash and merge this PR after your CI passes on it@dependabot cancel mergewill cancel a previously requested merge and block automerging@dependabot reopenwill reopen this PR if it is closed@dependabot closewill close this PR and stop Dependabot recreating it. You can achieve the same result by closing it manually@dependabot ignore this major versionwill close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself)@dependabot ignore this minor versionwill close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself)@dependabot ignore this dependencywill close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself)@dependabot use these labelswill set the current labels as the default for future PRs for this repo and language@dependabot use these reviewerswill set the current reviewers as the default for future PRs for this repo and language@dependabot use these assigneeswill set the current assignees as the default for future PRs for this repo and language@dependabot use this milestonewill set the current milestone as the default for future PRs for this repo and language
You can disable automated security fix PRs for this repo from the Security Alerts page.
</details>
pr closed time in a month
PR closed KidkArolis/jetpack
Bumps minimist from 1.2.0 to 1.2.5. <details> <summary>Commits</summary> <ul> <li><a href="https://github.com/substack/minimist/commit/aeb3e27dae0412de5c0494e9563a5f10c82cc7a9"><code>aeb3e27</code></a> 1.2.5</li> <li><a href="https://github.com/substack/minimist/commit/278677b171d956b46613a158c6c486c3ef979b20"><code>278677b</code></a> 1.2.4</li> <li><a href="https://github.com/substack/minimist/commit/4cf1354839cb972e38496d35e12f806eea92c11f"><code>4cf1354</code></a> security notice</li> <li><a href="https://github.com/substack/minimist/commit/1043d212c3caaf871966e710f52cfdf02f9eea4b"><code>1043d21</code></a> additional test for constructor prototype pollution</li> <li><a href="https://github.com/substack/minimist/commit/6457d7440a47f329c12c4a5abfbce211c4235b93"><code>6457d74</code></a> 1.2.3</li> <li><a href="https://github.com/substack/minimist/commit/38a4d1caead72ef99e824bb420a2528eec03d9ab"><code>38a4d1c</code></a> even more aggressive checks for protocol pollution</li> <li><a href="https://github.com/substack/minimist/commit/13c01a5327736903704984b7f65616b8476850cc"><code>13c01a5</code></a> more failing proto pollution tests</li> <li><a href="https://github.com/substack/minimist/commit/f34df077a6b2bee1344188849a95e66777109e89"><code>f34df07</code></a> 1.2.2</li> <li><a href="https://github.com/substack/minimist/commit/67d3722413448d00a62963d2d30c34656a92d7e2"><code>67d3722</code></a> cleanup</li> <li><a href="https://github.com/substack/minimist/commit/63e7ed05aa4b1889ec2f3b196426db4500cbda94"><code>63e7ed0</code></a> don't assign onto <strong>proto</strong></li> <li>Additional commits viewable in <a href="https://github.com/substack/minimist/compare/1.2.0...1.2.5">compare view</a></li> </ul> </details> <br />
Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting @dependabot rebase.
<details> <summary>Dependabot commands and options</summary> <br />
You can trigger Dependabot actions by commenting on this PR:
@dependabot rebasewill rebase this PR@dependabot recreatewill recreate this PR, overwriting any edits that have been made to it@dependabot mergewill merge this PR after your CI passes on it@dependabot squash and mergewill squash and merge this PR after your CI passes on it@dependabot cancel mergewill cancel a previously requested merge and block automerging@dependabot reopenwill reopen this PR if it is closed@dependabot closewill close this PR and stop Dependabot recreating it. You can achieve the same result by closing it manually@dependabot ignore this major versionwill close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself)@dependabot ignore this minor versionwill close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself)@dependabot ignore this dependencywill close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself)@dependabot use these labelswill set the current labels as the default for future PRs for this repo and language@dependabot use these reviewerswill set the current reviewers as the default for future PRs for this repo and language@dependabot use these assigneeswill set the current assignees as the default for future PRs for this repo and language@dependabot use this milestonewill set the current milestone as the default for future PRs for this repo and language
You can disable automated security fix PRs for this repo from the Security Alerts page.
</details>
pr closed time in a month
PR closed KidkArolis/jetpack
Bumps acorn from 6.4.0 to 6.4.1. <details> <summary>Commits</summary> <ul> <li><a href="https://github.com/acornjs/acorn/commit/9a2e9b6678e243d66846b91179d650d28453e70c"><code>9a2e9b6</code></a> Mark version 6.4.1</li> <li><a href="https://github.com/acornjs/acorn/commit/90a9548ea0ce351b54f956e2c4ed27cca9631284"><code>90a9548</code></a> More rigorously check surrogate pairs in regexp validator</li> <li>See full diff in <a href="https://github.com/acornjs/acorn/compare/6.4.0...6.4.1">compare view</a></li> </ul> </details> <br />
Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting @dependabot rebase.
<details> <summary>Dependabot commands and options</summary> <br />
You can trigger Dependabot actions by commenting on this PR:
@dependabot rebasewill rebase this PR@dependabot recreatewill recreate this PR, overwriting any edits that have been made to it@dependabot mergewill merge this PR after your CI passes on it@dependabot squash and mergewill squash and merge this PR after your CI passes on it@dependabot cancel mergewill cancel a previously requested merge and block automerging@dependabot reopenwill reopen this PR if it is closed@dependabot closewill close this PR and stop Dependabot recreating it. You can achieve the same result by closing it manually@dependabot ignore this major versionwill close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself)@dependabot ignore this minor versionwill close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself)@dependabot ignore this dependencywill close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself)@dependabot use these labelswill set the current labels as the default for future PRs for this repo and language@dependabot use these reviewerswill set the current reviewers as the default for future PRs for this repo and language@dependabot use these assigneeswill set the current assignees as the default for future PRs for this repo and language@dependabot use this milestonewill set the current milestone as the default for future PRs for this repo and language
You can disable automated security fix PRs for this repo from the Security Alerts page.
</details>
pr closed time in a month
PR closed KidkArolis/jetpack
Bumps acorn from 6.1.1 to 6.4.1. <details> <summary>Commits</summary> <ul> <li><a href="https://github.com/acornjs/acorn/commit/9a2e9b6678e243d66846b91179d650d28453e70c"><code>9a2e9b6</code></a> Mark version 6.4.1</li> <li><a href="https://github.com/acornjs/acorn/commit/90a9548ea0ce351b54f956e2c4ed27cca9631284"><code>90a9548</code></a> More rigorously check surrogate pairs in regexp validator</li> <li><a href="https://github.com/acornjs/acorn/commit/df0cf1a3e2b1a51a26c14984dc0f5412b7151b10"><code>df0cf1a</code></a> Mark version 6.4.0</li> <li><a href="https://github.com/acornjs/acorn/commit/53034126864b492da4e278628bb972cb2a9313d4"><code>5303412</code></a> Also export Parser via Parser.acorn</li> <li><a href="https://github.com/acornjs/acorn/commit/efe273e70123449a458157dbf578afaf109a49ab"><code>efe273e</code></a> give token types and etc to plugins</li> <li><a href="https://github.com/acornjs/acorn/commit/ac6decb94a3aa4eee99230fdaf5883dfaafe8479"><code>ac6decb</code></a> Mark version 6.3.0</li> <li><a href="https://github.com/acornjs/acorn/commit/7e9817d17639d95cc6dbacfde734a0626b2a7dea"><code>7e9817d</code></a> Allow sourceType: module even with ecmaVersion < 6</li> <li><a href="https://github.com/acornjs/acorn/commit/e2b8cc087386eccc2ad6fd4a02b4257833557cb3"><code>e2b8cc0</code></a> Fix broken parsing of new expressions when allowReserved=="never"</li> <li><a href="https://github.com/acornjs/acorn/commit/1555c528855b10320ce98b4154906d7898c92990"><code>1555c52</code></a> Update acorn.d.ts</li> <li><a href="https://github.com/acornjs/acorn/commit/77c20fa2c2f490e646b67e6a0ff7e75fb54ab6c8"><code>77c20fa</code></a> Mark version 6.2.1</li> <li>Additional commits viewable in <a href="https://github.com/acornjs/acorn/compare/6.1.1...6.4.1">compare view</a></li> </ul> </details> <br />
Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting @dependabot rebase.
<details> <summary>Dependabot commands and options</summary> <br />
You can trigger Dependabot actions by commenting on this PR:
@dependabot rebasewill rebase this PR@dependabot recreatewill recreate this PR, overwriting any edits that have been made to it@dependabot mergewill merge this PR after your CI passes on it@dependabot squash and mergewill squash and merge this PR after your CI passes on it@dependabot cancel mergewill cancel a previously requested merge and block automerging@dependabot reopenwill reopen this PR if it is closed@dependabot closewill close this PR and stop Dependabot recreating it. You can achieve the same result by closing it manually@dependabot ignore this major versionwill close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself)@dependabot ignore this minor versionwill close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself)@dependabot ignore this dependencywill close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself)@dependabot use these labelswill set the current labels as the default for future PRs for this repo and language@dependabot use these reviewerswill set the current reviewers as the default for future PRs for this repo and language@dependabot use these assigneeswill set the current assignees as the default for future PRs for this repo and language@dependabot use this milestonewill set the current milestone as the default for future PRs for this repo and language
You can disable automated security fix PRs for this repo from the Security Alerts page.
</details>
pr closed time in a month
PR closed KidkArolis/jetpack
Bumps handlebars from 4.1.2 to 4.7.3. <details> <summary>Changelog</summary>
Sourced from handlebars's changelog.
v4.7.3 - February 5th, 2020
Chore/Housekeeping:
- #1644 - Download links to aws broken on handlebarsjs.com - access denied (@Tea56)
- Fix spelling and punctuation in changelog - d78cc73
Bugfixes:
- Add Type Definition for Handlebars.VERSION, Fixes #1647 - 4de51fe
- Include Type Definition for runtime.js in Package - a32d05f
Compatibility notes:
- No incompatibilities are to be expected
v4.7.2 - January 13th, 2020
Bugfixes:
- fix: don't wrap helpers that are not functions - 9d5aa36, #1639
Chore/Build:
- chore: execute saucelabs-task only if access-key exists - a4fd391
Compatibility notes:
- No breaking changes are to be expected
v4.7.1 - January 12th, 2020
Bugfixes:
- fix: fix log output in case of illegal property access - f152dfc
- fix: log error for illegal property access only once per property - 3c1e252
Compatibility notes:
- no incompatibilities are to be expected.
v4.7.0 - January 10th, 2020
Features: </tr></table> ... (truncated) </details> <details> <summary>Commits</summary>
c978969v4.7.39278f21Update release notesd78cc73Fixes spelling and punctuation4de51feAdd Type Definition for Handlebars.VERSION, Fixes #1647a32d05fInclude Type Definition for runtime.js in Packagead63f51chore: add missing "await" in aws-s3 publishing code586e672v4.7.2f0c6c4cUpdate release notesa4fd391chore: execute saucelabs-task only if access-key exists9d5aa36fix: don't wrap helpers that are not functions- Additional commits viewable in compare view </details> <br />
Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting @dependabot rebase.
<details> <summary>Dependabot commands and options</summary> <br />
You can trigger Dependabot actions by commenting on this PR:
@dependabot rebasewill rebase this PR@dependabot recreatewill recreate this PR, overwriting any edits that have been made to it@dependabot mergewill merge this PR after your CI passes on it@dependabot squash and mergewill squash and merge this PR after your CI passes on it@dependabot cancel mergewill cancel a previously requested merge and block automerging@dependabot reopenwill reopen this PR if it is closed@dependabot closewill close this PR and stop Dependabot recreating it. You can achieve the same result by closing it manually@dependabot ignore this major versionwill close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself)@dependabot ignore this minor versionwill close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself)@dependabot ignore this dependencywill close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself)@dependabot use these labelswill set the current labels as the default for future PRs for this repo and language@dependabot use these reviewerswill set the current reviewers as the default for future PRs for this repo and language@dependabot use these assigneeswill set the current assignees as the default for future PRs for this repo and language@dependabot use this milestonewill set the current milestone as the default for future PRs for this repo and language
You can disable automated security fix PRs for this repo from the Security Alerts page.
</details>
pr closed time in a month
startedmicrosoft/FluidFramework
started time in a month
startedjosephg/statecraft
started time in a month
startedbraid-work/braidjs
started time in a month
startedautomerge/hypermerge
started time in a month
issue commenthumaans/next-img
There's some discussion here on sharp's support for avif: https://github.com/lovell/sharp/issues/2289

comment created time in 2 months
startedhumaans/next-img
started time in 2 months
issue commenthumaans/next-img
100%, will be adding that in the near future. Need to understand if Sharp's implementation will work or if another lib will be necessary.
comment created time in 2 months
startedFedericoDiRosa/react-window-scroller
started time in 2 months
PR opened FedericoDiRosa/react-window-scroller
Haven't tested 😬 But noticed some React warnings about setting state on unmounted components and I think this might be it.
pr created time in 2 months
push eventKidkArolis/react-window-scroller
commit sha e6e87331cf4b660405c3734907f1082ce8032c84
Cancel throttled fn on unmount
push time in 2 months
fork KidkArolis/react-window-scroller
Window scroller component for react-window
https://federicodirosa.github.io/react-window-scroller/
fork in 2 months
push eventKidkArolis/jetpack
commit sha 6db4e54747fb8b54a0e538c336b6ee61a9f0c4dd
0.19.0-alpha.1
push time in 2 months
push eventKidkArolis/jetpack
commit sha 07c908f1650c28ca8040ebdc04a5749786f4b25b
Fix the react-refresh plugin installation
push time in 2 months
push eventKidkArolis/jetpack
commit sha fed2eeaf87eef0773c157598892f42031d336200
0.19.0-alpha.0
push time in 2 months
push eventKidkArolis/jetpack
commit sha 7a5bda0091853cb269a624f5fbaac2fc6e437030
Default to fast-refresh for React reloading
push time in 2 months
issue closedhumaans/next-img
Resizing PNG increases size instead reducing
Hi, I started using this plugin (great work btw) this week and am trying to run a few resizing and optimisations with PNG and JPG files. So far, no issues with JPG.
Today i'm running the resize for my PNG file and i noticed the final result in /resources contain a file that has a bigger size than the original.
Do you happen to know what would be the cause for this behaviour ?
Thanks a lot!
my code:
import { Picture } from 'next-img';
<Picture src={require('../public/images/proposal.png?sizes=375,800')} />
Result in /resources folder:
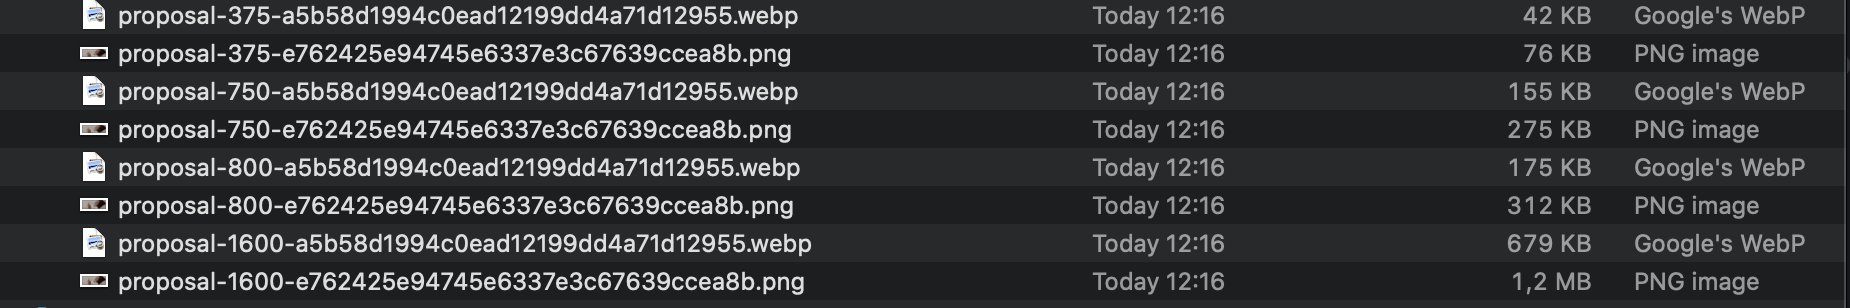
My original image in src/public/images folder:

original size dimension: 2880x1036
closed time in 2 months
victorkurauchi
issue commenthumaans/next-img
Resizing PNG increases size instead reducing
I had a quick look into this.
The issue here is that these images are not very suited for .png format (png is a lossless image format). If you re-save these images as .jpg you will immediately get a smaller file size right off the bat. And then, passing those through next-img, you'll get even more compression across both jpg and webp outputs, depending on your plugin configuration.
If you keep them as png, then they get recompressed as part of the resizing process, and the sharp optimisation is not as effective as it could be if the best optimisation plugins were used. I briefly talk about it in the FAQ in the readme: https://github.com/humaans/next-img#faq and why it's not part of the next-img.
In other words, under normal circumstances, where normal in this case would be to use jpg for photos, not png, the plugin should work as expected:
- yields much smaller file size webp image compared to original
- yields smaller file size jpg image compared to original (depending on jpg quality plugin configuration setting)
And your case I'd say is a bit of an edge case, since you're using png for a photo, which:
- yields slightly smaller file size webp image compared to original (lossless by default because source is png)
- yields larger file size png image, because the plugin is not maximally optimizing png images
In the future, we might introduce an ability to add further png optimization plugins into the pipeline. But in a general case that should not be necessary. My recommendation is to use jpg format for these specific source images (since they're photos), which should yield the smallest file sizes with imperceptible quality drop (you might have to bump up the jpeg: { quality: 80 } setting though).
comment created time in 2 months
issue commenthumaans/next-img
Resizing PNG increases size instead reducing
Hm, that's strange. I'll have a closer look tmrw. Any chance you could share the image, or try reproducing the issue with some public image?
comment created time in 2 months
push eventhumaans/figbird
commit sha 5449a64899a7089057341435ba8e3cd14878d252
Updates
push time in 3 months
issue closedhumaans/figbird
I was unable to figure out how to use figbird because the example was incomplete. It doesn't include the client configuration module. Here's what the code should look like, according to David Luecke
import React, {useState} from 'react';
import {Provider} from 'figbird';
**import client from './feathers';**
import Users from './Notes.js';

function App() {
    return (
        <Provider feathers={**client**}>
            <Notes/>
        </Provider>
    )
}
export default App;
Note that, in this example, the module in ./feathers contains the feathers configuration (URL, socket, etc.). In the current example, it would be impossible to specify a different port.
closed time in 3 months
lemlich
push eventhumaans/figbird
commit sha 964a164f3c02933a6d03394e73548de38eaef4e4
Fix error in docs
commit sha e2114985a0158ffd352c9cecca8cf3d77b84015a
Merge pull request #10 from joeinnes/patch-2 Fix error in docs
push time in 3 months
push eventhumaans/figbird
commit sha 5454ea62f77129ab5b73e967783870804904ce76
More verbose example Added feathers client configuration
commit sha 89a1a05f6365c24b6a3534d218ea37902d4295d1
Merge pull request #9 from joeinnes/patch-1 More verbose example
push time in 3 months
PR merged humaans/figbird
Added feathers client configuration

pr closed time in 3 months
delete branch humaans/figbird
delete branch : dependabot/npm_and_yarn/lodash-4.17.19
delete time in 3 months
PR closed humaans/figbird
Bumps lodash from 4.17.15 to 4.17.19. <details> <summary>Release notes</summary> <p><em>Sourced from <a href="https://github.com/lodash/lodash/releases">lodash's releases</a>.</em></p> <blockquote> <h2>4.17.16</h2> </blockquote> </details> <details> <summary>Commits</summary> <ul> <li><a href="https://github.com/lodash/lodash/commit/d7fbc52ee0466a6d248f047b5d5c3e6d1e099056"><code>d7fbc52</code></a> Bump to v4.17.19</li> <li><a href="https://github.com/lodash/lodash/commit/2e1c0f22f425e9c013815b2cd7c2ebd51f49a8d6"><code>2e1c0f2</code></a> Add npm-package</li> <li><a href="https://github.com/lodash/lodash/commit/1b6c282299f4e0271f932b466c67f0f822aa308e"><code>1b6c282</code></a> Bump to v4.17.18</li> <li><a href="https://github.com/lodash/lodash/commit/a370ac81408de2da77a82b3c4b61a01a3b9c2fac"><code>a370ac8</code></a> Bump to v4.17.17</li> <li><a href="https://github.com/lodash/lodash/commit/1144918f3578a84fcc4986da9b806e63a6175cbb"><code>1144918</code></a> Rebuild lodash and docs</li> <li><a href="https://github.com/lodash/lodash/commit/3a3b0fd339c2109563f7e8167dc95265ed82ef3e"><code>3a3b0fd</code></a> Bump to v4.17.16</li> <li><a href="https://github.com/lodash/lodash/commit/c84fe82760fb2d3e03a63379b297a1cc1a2fce12"><code>c84fe82</code></a> fix(zipObjectDeep): prototype pollution (<a href="https://github-redirect.dependabot.com/lodash/lodash/issues/4759">#4759</a>)</li> <li><a href="https://github.com/lodash/lodash/commit/e7b28ea6cb17b4ca021e7c9d66218c8c89782f32"><code>e7b28ea</code></a> Sanitize sourceURL so it cannot affect evaled code (<a href="https://github-redirect.dependabot.com/lodash/lodash/issues/4518">#4518</a>)</li> <li><a href="https://github.com/lodash/lodash/commit/0cec225778d4ac26c2bac95031ecc92a94f08bbb"><code>0cec225</code></a> Fix lodash.isEqual for circular references (<a href="https://github-redirect.dependabot.com/lodash/lodash/issues/4320">#4320</a>) (<a href="https://github-redirect.dependabot.com/lodash/lodash/issues/4515">#4515</a>)</li> <li><a href="https://github.com/lodash/lodash/commit/94c3a8133cb4fcdb50db72b4fd14dd884b195cd5"><code>94c3a81</code></a> Document matches* shorthands for over* methods (<a href="https://github-redirect.dependabot.com/lodash/lodash/issues/4510">#4510</a>) (<a href="https://github-redirect.dependabot.com/lodash/lodash/issues/4514">#4514</a>)</li> <li>Additional commits viewable in <a href="https://github.com/lodash/lodash/compare/4.17.15...4.17.19">compare view</a></li> </ul> </details> <details> <summary>Maintainer changes</summary> <p>This version was pushed to npm by <a href="https://www.npmjs.com/~mathias">mathias</a>, a new releaser for lodash since your current version.</p> </details> <br />
Dependabot will resolve any conflicts with this PR as long as you don't alter it yourself. You can also trigger a rebase manually by commenting @dependabot rebase.
<details> <summary>Dependabot commands and options</summary> <br />
You can trigger Dependabot actions by commenting on this PR:
@dependabot rebasewill rebase this PR@dependabot recreatewill recreate this PR, overwriting any edits that have been made to it@dependabot mergewill merge this PR after your CI passes on it@dependabot squash and mergewill squash and merge this PR after your CI passes on it@dependabot cancel mergewill cancel a previously requested merge and block automerging@dependabot reopenwill reopen this PR if it is closed@dependabot closewill close this PR and stop Dependabot recreating it. You can achieve the same result by closing it manually@dependabot ignore this major versionwill close this PR and stop Dependabot creating any more for this major version (unless you reopen the PR or upgrade to it yourself)@dependabot ignore this minor versionwill close this PR and stop Dependabot creating any more for this minor version (unless you reopen the PR or upgrade to it yourself)@dependabot ignore this dependencywill close this PR and stop Dependabot creating any more for this dependency (unless you reopen the PR or upgrade to it yourself)@dependabot use these labelswill set the current labels as the default for future PRs for this repo and language@dependabot use these reviewerswill set the current reviewers as the default for future PRs for this repo and language@dependabot use these assigneeswill set the current assignees as the default for future PRs for this repo and language@dependabot use this milestonewill set the current milestone as the default for future PRs for this repo and language
You can disable automated security fix PRs for this repo from the Security Alerts page.
</details>
pr closed time in 3 months
issue commentmatthewp/robot
Best way to avoid invoking promises multiple times (or keeping context up to date)
Another idea.. what if invoke was more like action, except it also gets send passed in... in fact, you could get rid of invoke altogether if action received send, e.g.:
const save = (ctx, ev, send) => { // <-- notice send, a new param, enables async behaviours not just promises
  send({ type: 'assign, saving: true })
  post(ev.id, ev.data)
    .then((data) => { send({ type: 'done', data }) })
    .catch((error) => { send({ type: 'error, error }) })
}

const machine = machine({
  saving: state(
      immediate('saving', guard(ctx => !ctx.saving), action(save)),
      transition('done', 'closing', action(close)),
      transition('error', 'configure', reduce(assign)),
      transition('close', 'closing', action(close)),
      assignable('saving'),
    )
})

comment created time in 3 months
push eventhumaans/figbird
commit sha 2df0fae294e49092a7f2de23e388b6609f71734b
0.8.1
push time in 3 months
created taghumaans/figbird
Effortless realtime data management for React + Feathers applications
created time in 3 months
push eventhumaans/figbird
commit sha 35b6ac0b4af4d566eab8f1bbeb6ca5d5c78a618e
Increase ava timeout
push time in 3 months
push eventhumaans/figbird
commit sha 099dc9c7f4309c4dbe5c1a68e4310d898e2ce761
Do not dispatch when mutation promises resolve after unmounting
commit sha 6ef3994b1aadbbe2365e649cbd5a03a722074020
Upgrade deps
push time in 3 months
issue openedmatthewp/robot
Best way to avoid invoking promises multiple times (or keeping context up to date)
Hi, thanks for a great library, been enjoying getting to learn using it.
I don't know how common this is, but I want to keep various bits of data (props, data from other hooks) in the context and I want to keep them up to date even if I'm in a middle of invocation.
To do so, I've added an 'assign' transition to every state:
const close = ctx => ctx.onClose()
const assign = (ctx, { type, ...data }) => ({ ...ctx, ...data })
const assignable = name => transition('assign', name, reduce(assign))

const machine = createMachine({
    initialising: state(
      immediate('configure', guard(loadingDone)),
      immediate('initialisingFailed', guard(loadingError)),
      transition('close', 'closing', action(close)),
      assignable('initialising'),
    ),
    initialisingFailed: state(
      transition('close', 'closing', action(close)),
      assignable('initialisingFailed'),
    ),
    configure: state(
      transition('close', 'closing', action(close)),
      transition('save', 'saving'),
      assignable('configure'),
    ),
    saving: invoke(
      save,
      transition('done', 'closing', action(close)),
      transition('error', 'configure', reduce(assign)),
      transition('close', 'closing', action(close)),
      assignable('saving'), // <--- a problem! because transitioning back to itself will invoke again
    ),
    closing: state(),
  })
A few thoughts / questions / learnings from this so far:
- Having to manually add assignable to each state is a bit tedious, but not too bad. Given that you might always want to keep context up to date wrt to external data (e.g.
onClosefunction passed via prop, or some other bits of context), wondering if there should be an easier way to update the context (in xstate, I think you can do that by handling an even in the root machine). - My assignable helper seems "unidiomatic", because I have to specify the name of the state I'm adding the transition to. There is no way to transition to self without knowing the name of the state. and so I have to pass the name of the state to each
assignablecall. Wondering if self transitions could be made easier.. Or perhaps the first problem is solved in a different way, this would also go away.
I'm not really saying these are even a problem, I think it's good to be explicit and keep the rule set small and simple.
But the next bit is more challenging. The issue is that if you're in the saving state and send 'assign' event to update context (if say the parent component rerendered passing a new onClose prop), you invoke the save function again, but we don't want that in this case of self transition. Now, the best way I found so far to avoid this was to create a custom invokeOnce helper, which only invokes the function on entering the state and not on "self" transitions:
const valueEnumerable = value => ({ enumerable: true, value })
const create = (a, b) => Object.freeze(Object.create(a, b))
const invokePromiseOnceType = {
  enter(machine, service, event) {
    const name = machine.current
    const prev = service.machine.current
    if (prev !== name) {
      this.fn
        .call(service, service.context, event)
        .then(data => service.send({ type: 'done', data }))
        .catch(error => service.send({ type: 'error', error }))
    }

    return machine
  },
}

export function invokeOnce(fn, ...transitions) {
  const s = state(...transitions)
  return create(invokePromiseOnceType, {
    fn: valueEnumerable(fn),
    transitions: valueEnumerable(s.transitions),
  })
}
Only sharing all this to get feedback from any current / future users of robot about how they handle this sort of stuff.
For example, would it be better if invoke always triggered on enter only, and to allow invoking multiple times you'd have to transition out and back in?
Or should there be a way to guard an invoke? (not sure that's semantically correct).
Or perhaps another way would to solve this is to use an intermediate state:
    configure: state(
      transition('save', 'save'),
      assignable('configure'),
    ),
    save: invoke(
      save,
      immediate('saving')
    ),
    saving: state(
      transition('done', 'closing', action(close)),
      transition('error', 'configure', reduce(assign)),
      assignable('saving'), // no longer a problem, since we're no longer in an invoke state
    ),
created time in 3 months
push eventhumaans/figbird
commit sha 345335b1437ba9701e83c90ea8485566f525ecb3
0.8.0
push time in 3 months
created taghumaans/figbird
Effortless realtime data management for React + Feathers applications
created time in 3 months
push eventhumaans/figbird
commit sha 7f6ef7fb264497d3378d731d5a256a947ae63678
Add useMemo/useCallback to reduce how often functions/objects change
push time in 3 months
startedmatthewp/robot
started time in 3 months
created tagKidkArolis/healthier
🧘♀️ Healthier is an opinionated style agnostic code linter – a friendly companion to Prettier
created time in 3 months
push eventKidkArolis/healthier
commit sha eb1344e31ec3c6e84e6266b33075729e2906bcd0
4.0.0
push time in 3 months
created tagKidkArolis/healthier
🧘♀️ Healthier is an opinionated style agnostic code linter – a friendly companion to Prettier
created time in 3 months
push eventKidkArolis/healthier
commit sha 7a3a4f4be09abd5149199f6d4668bcb63caf95fa
3.3.0
commit sha fdc9d62623dcc5a0f4c923a27e7ba8257a55cf84
Upgrade deps
commit sha c4232b50241b1d7ed812b9fe6e7585dc958845f5
Update CHANGELOG
push time in 3 months